Web Security focuses on protecting web applications, websites, and online platforms against modern cyber attacks, vulnerabilities, and exploitation techniques.
This category covers SQL injection, XSS, CSRF, SSRF, authentication flaws, access control issues, business logic vulnerabilities, and OWASP Top 10 security risks.
Readers can learn about web application penetration testing, bug bounty methodologies, secure coding practices, WAF bypass techniques, and web attack detection strategies.
The blog also shares practical exploitation examples, remediation techniques, testing workflows, security tools, and real-world vulnerability case studies.
Whether you are a web developer, penetration tester, bug bounty hunter, or cybersecurity learner, this category provides practical and technical web security knowledge.
File uploads are a common feature in modern web applications. Users upload profile pictures, invoices, identity documents, reports, spreadsheets, videos, and other...
Modern web applications rarely perform important business operations through a single request. Actions such as transferring money, approving invoices, processing refunds, changing...
JavaScript powers modern web applications, REST APIs, browser-based platforms, and server-side applications built with Node.js. Its flexible object model makes development easier,...
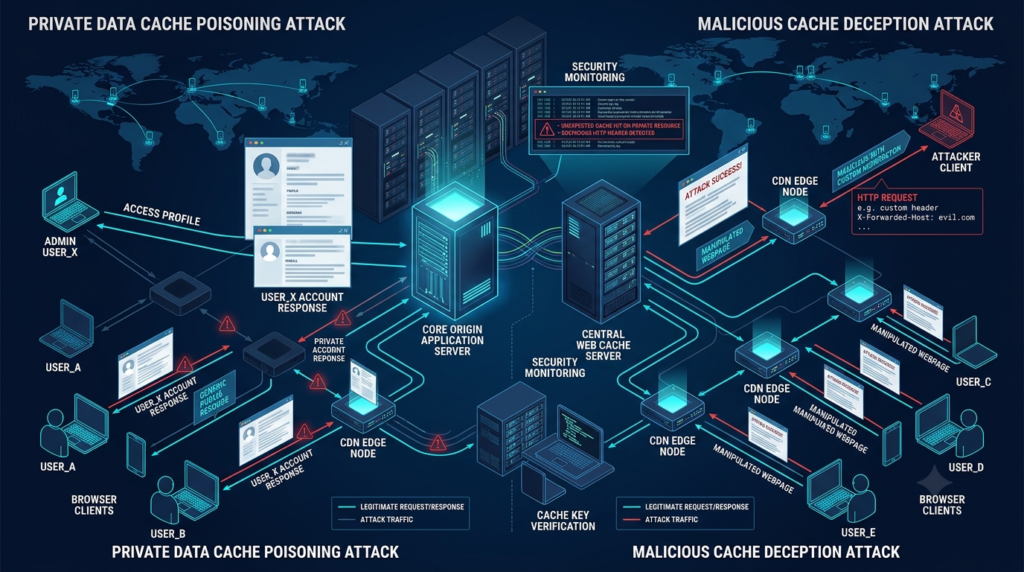
Web applications rely on caching to improve performance, reduce server load, and deliver content quickly to users. Content Delivery Networks (CDNs), reverse...
Online shopping and digital payment systems process thousands of transactions every minute. Customers expect checkout operations to be fast, reliable, and secure....
WebSocket Security Testing is an important part of modern application security because real-time applications depend on persistent connections to exchange data between...
Multi-tenant SaaS penetration testing is an important part of securing cloud-based applications that serve multiple customers through a shared platform. A single...
Web servers form the backbone of modern digital infrastructure. Whether powering customer portals, e-commerce platforms, or enterprise REST APIs, web applications are...
SQLMap Tutorial guides are useful for security professionals because SQL injection remains one of the most important web application vulnerabilities to understand....