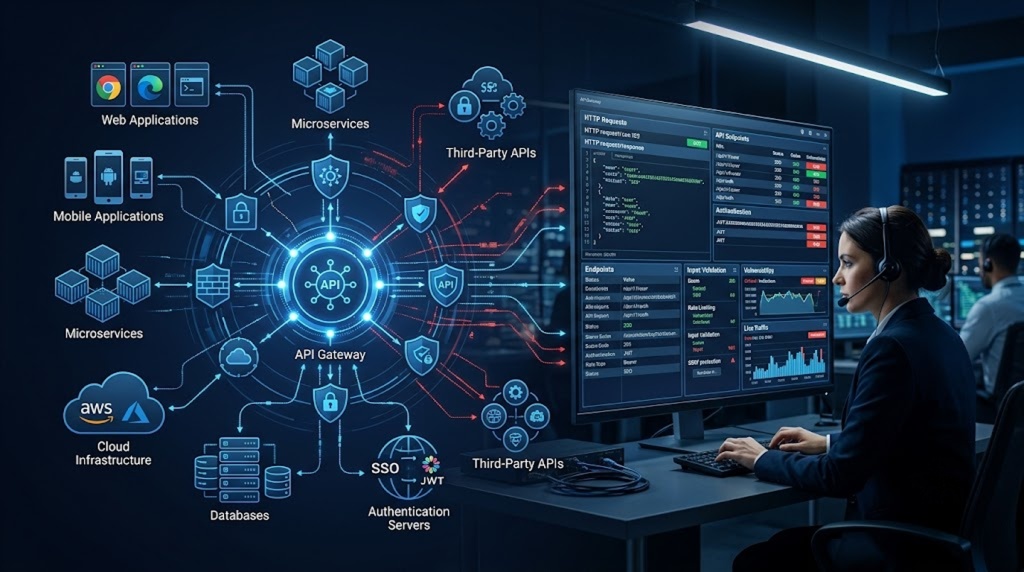
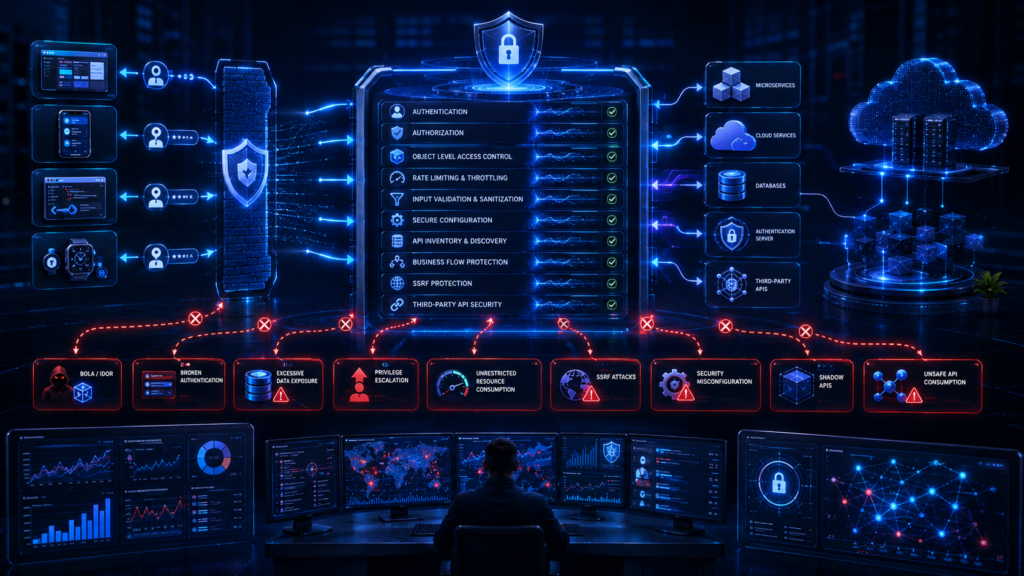
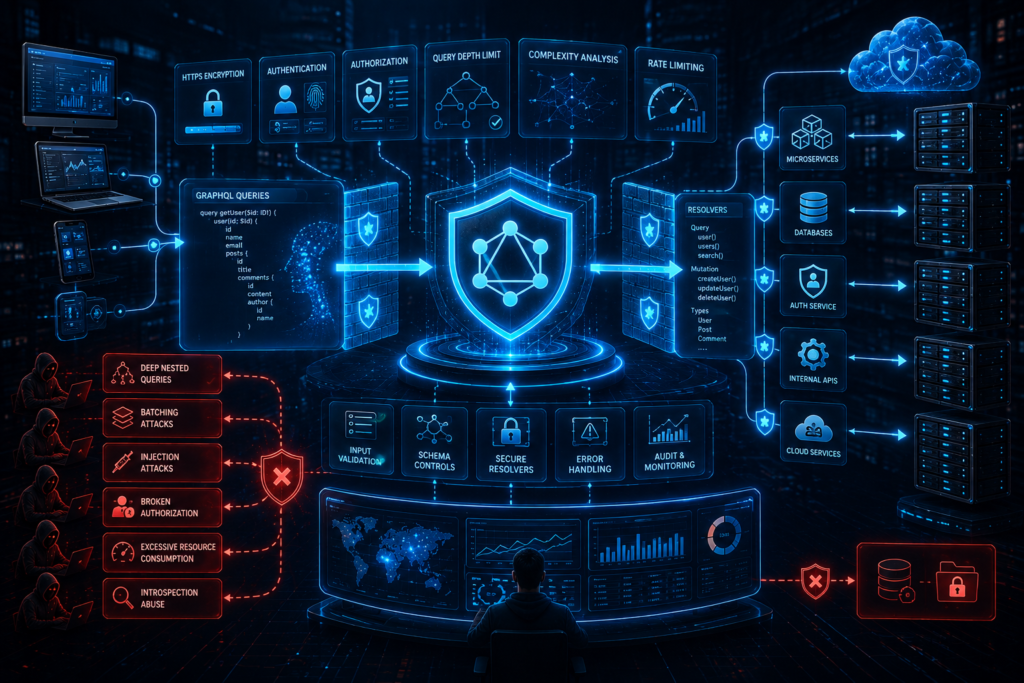
API Security focuses on identifying, testing, and securing vulnerabilities within REST APIs, GraphQL APIs, and modern backend communication systems.
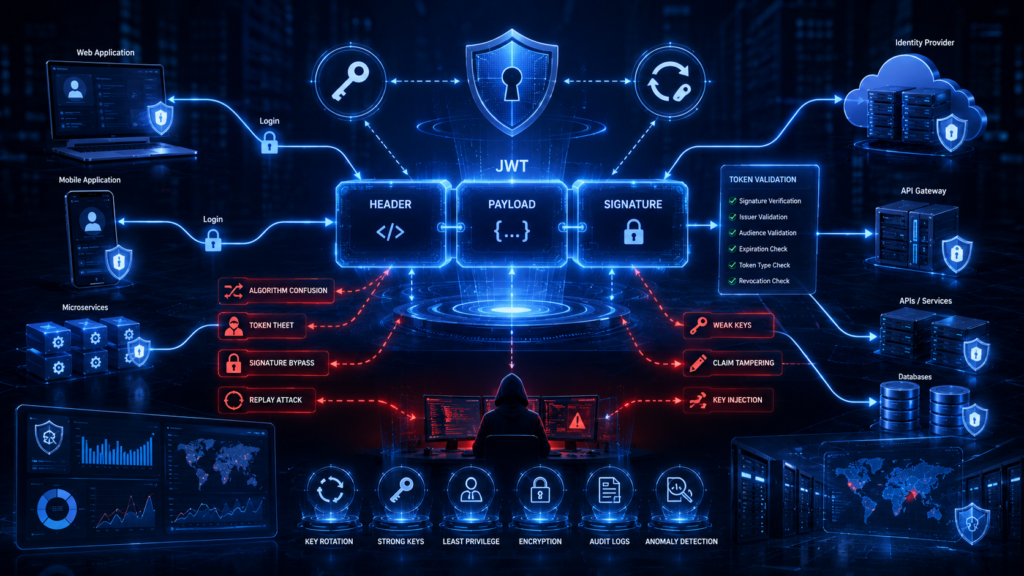
This category covers API authentication flaws, authorization bypass issues, JWT vulnerabilities, insecure object references, rate limiting weaknesses, and API penetration testing methodologies.
Readers can explore real-world API attack scenarios, API fuzzing techniques, token manipulation, OAuth security, API gateway security, and OWASP API Security Top 10 risks.
The blog also provides practical testing workflows using tools such as Burp Suite, Postman, curl, and automation scripts commonly used during API security assessments.
Whether you are a developer, penetration tester, bug bounty hunter, or cybersecurity learner, this category helps strengthen API security knowledge through practical and technical content.
Modern applications increasingly rely on AI-powered systems to read documents, summarize web pages, analyze emails, and retrieve information from internal knowledge bases....
Modern enterprise applications increasingly depend on microservices to handle authentication, payments, customer information, internal communication, and business operations. These services need a...
WebSocket Security Testing is an important part of modern application security because real-time applications depend on persistent connections to exchange data between...
Webhook Security Testing is an important part of modern API security because webhooks allow external applications and services to send event notifications...
APIs have become the backbone of modern applications. Web applications, mobile apps, SaaS platforms, cloud services, payment systems, microservices, and third-party integrations...
APIs are now at the center of modern applications. Mobile apps, SaaS platforms, cloud services, payment systems, microservices, and third-party integrations all...
Modern applications depend heavily on APIs. Mobile applications, SaaS platforms, payment systems, cloud services, microservices, and third-party integrations may generate thousands or...
JSON Web Tokens are widely used to carry authentication and authorization information between applications, APIs, identity providers, and microservices. Because JWTs can...
OAuth 2.0 has become one of the most widely used authorization frameworks for modern web applications, APIs, mobile applications, and cloud services....
GraphQL has changed how modern applications communicate with backend services. Instead of exposing many fixed endpoints like a traditional REST API, GraphQL...