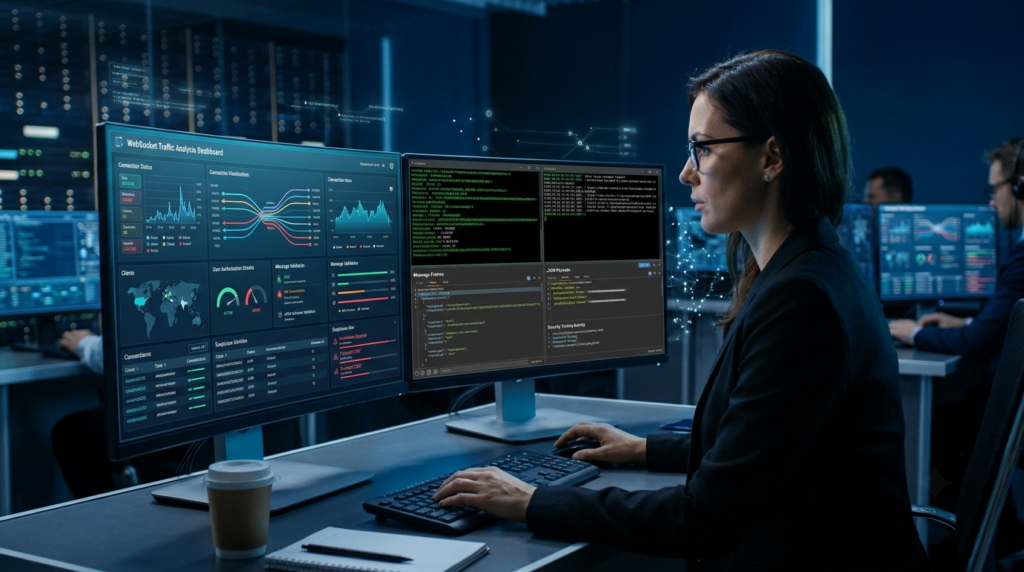
WebSocket Security Testing is an important part of modern application security because real-time applications depend on persistent connections to exchange data between clients and servers. Chat applications, online trading platforms, multiplayer games, collaboration tools, and live notification systems commonly use WebSockets to deliver information without repeatedly establishing new HTTP connections.
Unlike traditional HTTP communication, WebSockets support continuous, bidirectional data exchange over a single connection. This improves application responsiveness, but it also introduces security challenges that developers and penetration testers must understand.
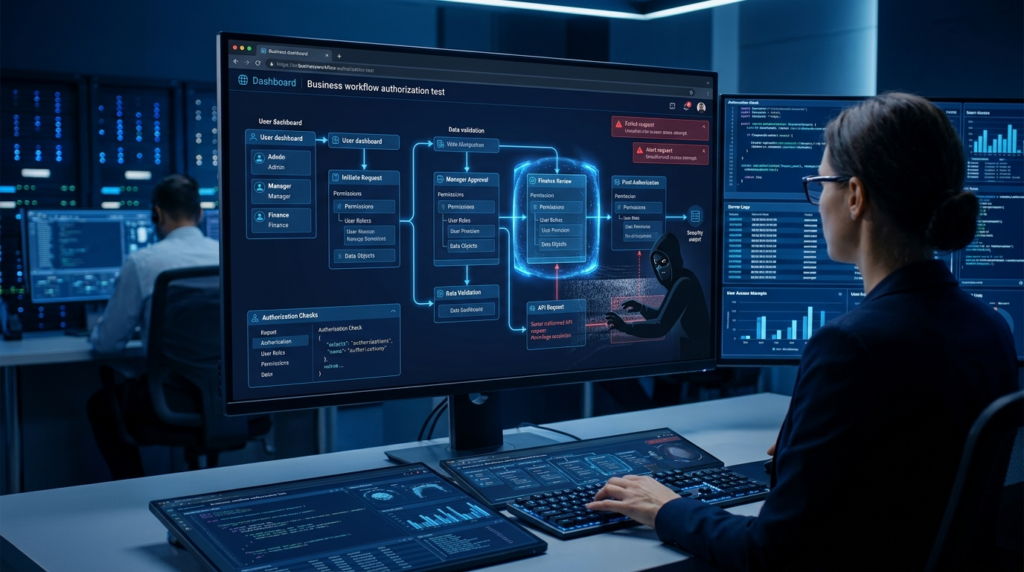
A WebSocket connection may be authenticated during its initial handshake, but that does not guarantee that every message sent afterward is authorized. An authenticated user could still attempt to access another user’s data, modify message parameters, trigger restricted actions, or exploit weaknesses in message validation.
This guide explains how WebSocket communication works, the vulnerabilities that affect real-time applications, and how security professionals can test connection-level and message-level controls.
What Is a WebSocket?
WebSocket is a communication protocol that enables two-way communication between a client and a server over a persistent connection.
Traditional HTTP generally follows a request-response model. A client sends a request, and the server returns a response. If the client needs updated information, it may need to send another request.
WebSockets work differently. Once a connection is established, both the client and server can send messages independently without creating a new HTTP request for every interaction.
For example, consider a live chat application:
- A user opens the chat application.
- The browser sends a WebSocket handshake request.
- The server validates the handshake and accepts the connection.
- The browser and server exchange messages over the established connection.
- The server delivers new messages without requiring the browser to repeatedly poll an HTTP endpoint.
WebSocket communication commonly uses:
ws://for unencrypted connections.wss://for encrypted connections using TLS.
A simplified handshake request looks like this:
GET /chat HTTP/1.1
Host: chat.example.com
Upgrade: websocket
Connection: Upgrade
Sec-WebSocket-Key: dGhlIHNhbXBsZSBub25jZQ==
Sec-WebSocket-Version: 13
Origin: https://app.example.com
A successful server response typically includes:
HTTP/1.1 101 Switching Protocols
Upgrade: websocket
Connection: Upgrade
Sec-WebSocket-Accept: <calculated-value>
After the handshake, communication continues through WebSocket frames rather than ordinary HTTP request-response exchanges.
The protocol is defined in RFC 6455.
Why Is WebSocket Security Testing Important?
WebSocket applications often handle sensitive information and business operations in real time.
A weakness in a persistent connection can expose information or allow unauthorized actions throughout the connection’s lifetime.
For example, imagine a financial application where users receive live account updates through WebSockets. If the server checks authentication only during the initial connection but does not enforce authorization for individual messages, one user might attempt to subscribe to another user’s account updates.
Several security risks make WebSocket testing necessary.
1. Weak Message-Level Authorization
Authentication confirms who a user is. Authorization determines what that user can access or perform.
A WebSocket connection may be established successfully for an authenticated user, but the server must still verify permission for every sensitive operation.
For example, a user may be allowed to view their own notifications but not another customer’s notifications.
If the server trusts a client-supplied user ID without checking ownership, an attacker may manipulate the message to access another user’s information.
2. Cross-Site WebSocket Hijacking
Cross-Site WebSocket Hijacking (CSWSH) is a vulnerability in which a malicious website attempts to establish a WebSocket connection to a vulnerable application using a victim’s authenticated browser session.
This can happen when an application relies on automatically attached cookies but does not properly validate the Origin header or implement appropriate protections.
If the connection succeeds, the malicious website may be able to interact with the application through the victim’s browser, depending on the application’s authorization and message-handling controls.
3. Message Manipulation
WebSocket messages often contain JSON objects with fields such as user IDs, account IDs, message types, roles, and transaction details.
An attacker may modify these values to test whether the server enforces access controls and validates incoming data.
For example:
{
  "action": "get_messages",
  "user_id": "1002"
}
Changing the user ID may reveal an insecure direct object reference if the server returns information belonging to another user.
4. Injection Attacks
WebSocket messages may be processed by backend services, databases, templates, or other application components.
If the server uses untrusted message data without proper validation, vulnerabilities such as SQL injection, command injection, or cross-site scripting may become possible.
The WebSocket protocol itself does not automatically prevent these application-level vulnerabilities.
5. Denial-of-Service Risks
Persistent connections consume server resources.
An attacker may attempt to open excessive connections, send oversized messages, or generate high volumes of requests.
Without suitable limits, this can affect application availability and degrade the experience for legitimate users.
Common WebSocket Security Vulnerabilities
Security testers should understand the most common weaknesses before assessing a real-time application.
1. Missing Authentication
Some WebSocket endpoints accept connections without requiring a valid user session or access token.
This may expose functionality intended only for authenticated users.
During testing, assess whether the endpoint accepts:
- Connections without authentication cookies.
- Missing authorization headers.
- Invalid or expired tokens.
- Revoked sessions.
- Unauthenticated access to restricted message types.
Expected secure behavior: The server should reject connections that do not meet the application’s authentication requirements.
2. Broken Message-Level Authorization
This is one of the most important WebSocket security risks.
A server may authenticate a user during the handshake but fail to verify permissions when processing individual messages.
Consider a support dashboard where an agent can access only assigned customer conversations.
A message might contain:
{
  "action": "view_conversation",
  "conversation_id": "5001"
}
If the agent changes the conversation ID to 5002 and receives another customer’s messages, the application may have a broken object-level authorization vulnerability.
Security recommendation: Verify ownership, role permissions, and resource access on the server for every sensitive message.
3. Insecure Origin Validation
The Origin header helps a server identify the origin of a browser-based WebSocket connection.
If the application accepts connections from arbitrary origins, it may become vulnerable to Cross-Site WebSocket Hijacking when browser credentials are automatically included.
Test whether the server:
- Allows unexpected origins.
- Accepts missing origins where browser-origin validation is required.
- Uses unsafe wildcard origin rules.
- Incorrectly compares origin values.
- Allows untrusted subdomains.
Security recommendation: Maintain an explicit allowlist of trusted origins and validate the origin during the handshake. Do not treat origin validation as a replacement for authentication or authorization.
4. Sensitive Data Exposure
WebSocket connections may transmit:
- Personal information.
- Authentication-related information.
- Account balances.
- Private messages.
- Session details.
- Internal application data.
- Transaction notifications.
If an application sends sensitive information to unauthorized users or exposes it through insecure connections, the data may be compromised.
Security recommendation: Use wss://, enforce message-level access controls, and avoid transmitting unnecessary sensitive information.
5. Insufficient Input Validation
A WebSocket server may accept JSON messages without checking their structure, type, length, or permitted values.
An attacker may send:
- Unexpected message types.
- Missing required fields.
- Invalid JSON.
- Unexpected data types.
- Excessively large payloads.
- Unexpected nested objects.
- Invalid identifiers.
Security recommendation: Validate every message against a strict server-side schema before processing it.
6. Insecure Session Handling
WebSocket connections may remain active after a user logs out or their session expires.
If the server does not terminate or revalidate the connection, a previously authenticated session may continue to perform actions.
Security recommendation: Define session expiration behavior, revoke connections when necessary, and recheck authentication state before sensitive operations.
7. Rate Limiting and Resource Exhaustion
WebSocket applications may allow clients to send messages continuously.
Without appropriate controls, attackers can generate excessive traffic or consume server resources.
Security recommendation: Apply connection limits, message-size restrictions, per-user rate limits, and monitoring for abnormal activity.
How WebSocket Security Testing Works
A structured testing process helps identify weaknesses in both the initial connection and the messages exchanged afterward.
Step 1: Identify WebSocket Endpoints
Start by identifying where the application establishes WebSocket connections.
Use browser developer tools or an HTTP interception proxy to inspect network traffic.
Look for:
ws://endpoints.wss://endpoints.- HTTP upgrade requests.
- WebSocket paths.
- Authentication cookies.
- Authorization headers.
- Origin values.
Document the endpoints and identify which application features use them.
Step 2: Inspect the Handshake
The handshake is the initial HTTP request that upgrades the connection to WebSocket communication.
Check whether the server properly handles authentication and connection parameters.
Useful test cases include:
- Missing authentication credentials.
- Invalid session cookies.
- Expired access tokens.
- Unexpected Origin headers.
- Unsupported WebSocket versions.
- Malformed handshake requests.
A successful handshake should not be treated as proof that the entire WebSocket implementation is secure.
Step 3: Capture WebSocket Messages
After establishing an authorized test connection, capture messages exchanged between the browser and server.
Record the message structure and identify fields that may affect authorization or business logic.
For example:
{
  "type": "subscribe",
  "channel": "private_notifications",
  "user_id": "1001"
}
Pay attention to identifiers, action names, roles, permissions, and resource references.
Step 4: Test Message-Level Authorization
Modify client-controlled values in a controlled test environment.
For example:
- Change a conversation ID.
- Replace a customer ID.
- Request a restricted channel.
- Attempt a privileged action with a low-privilege account.
- Subscribe to another user’s notification stream.
Use test accounts with different roles to compare application behavior.
Expected result: The server should reject unauthorized operations without exposing restricted information.
Step 5: Test Input Validation
Send unexpected message formats and values.
For example, if the application expects a numeric quantity, test whether it safely rejects a string or an unexpected object.
Also check how the server handles invalid JSON, unknown action names, oversized messages, and unexpected nested properties.
The objective is to confirm that malformed messages do not cause application errors, unexpected behavior, or unauthorized operations.
Step 6: Test Session Expiration
Establish a valid WebSocket connection and then expire or revoke the associated session using an authorized test account.
Attempt to perform a restricted operation through the existing connection.
Expected result: The application should enforce its session policy and prevent access after the session is no longer valid.
Step 7: Evaluate Rate Limits
Send a controlled number of messages to understand how the application handles repeated requests.
Test connection limits and message frequency within the agreed assessment scope.
Avoid uncontrolled traffic generation against production services.
Expected result: The application should enforce reasonable resource limits and handle excessive requests safely.
Practical Example: Testing Authorization in a Live Chat Application
Consider a customer support platform where users can exchange messages with support agents in real time.
The application uses WebSockets to deliver new messages without refreshing the page.
Each conversation has a unique identifier.
A penetration tester is asked to evaluate whether users can access conversations belonging to other customers.
Initial Message
The tester captures a message from an authorized test account:
{
  "action": "get_conversation",
  "conversation_id": "5001"
}
The server returns messages belonging to conversation 5001.
Authorization Test
The tester changes the conversation identifier:
{
  "action": "get_conversation",
  "conversation_id": "5002"
}
The tester sends the modified message using the same authorized connection.
Vulnerable Behavior
If the server returns conversation 5002, even though the test user does not have permission to access it, the application may contain a broken object-level authorization vulnerability.
This issue can expose private customer conversations and personal information.
Secure Behavior
The server should verify that the authenticated user is authorized to access the requested conversation.
If the user does not have permission, the server should reject the operation and avoid returning sensitive information.
How to Document the Finding
A professional penetration testing report should include:
- WebSocket endpoint.
- Affected application functionality.
- User role used during testing.
- Original message.
- Modified message.
- Server response.
- Evidence of unauthorized access, if confirmed.
- Business impact.
- Recommended remediation.
Use only authorized test accounts and data. Avoid accessing real customer conversations during testing.
WebSocket Security Testing Tools
Several security tools can help penetration testers inspect WebSocket handshakes and message-level behavior.
1. Burp Suite
Burp Suite is one of the most useful tools for WebSocket security testing.
It supports WebSocket traffic inspection and provides functionality to view and manipulate messages.
Testers can use it to:
- Capture WebSocket handshakes.
- Inspect incoming and outgoing frames.
- Modify message parameters.
- Replay messages.
- Compare server responses.
- Investigate authorization weaknesses.
2. OWASP ZAP
OWASP ZAP is an open-source web application security testing tool.
It can help testers inspect WebSocket communication alongside traditional HTTP traffic.
It is useful for understanding application behavior and supporting manual security assessments.
3. Browser Developer Tools
Modern browsers provide built-in developer tools that allow testers to inspect WebSocket connections.
In Chrome, the Network tab can display WebSocket requests and their exchanged frames.
This is particularly useful during initial reconnaissance and application behavior analysis.
4. wscat
wscat is a command-line WebSocket client.
It can help establish connections and send messages to an authorized WebSocket endpoint.
Example:
wscat -c wss://test.example.com/wsFor an endpoint requiring authentication, supply the required credentials using the supported options and follow the application’s authorization requirements.
5. Python WebSocket Libraries
Python libraries such as websockets can be used to create test clients and automate authorized message exchanges.
They are useful when testing:
- Message formats.
- Authentication behavior.
- Connection handling.
- Repeated requests.
- Server responses.
- Application-specific workflows.
Automation should follow the agreed testing scope and respect production rate limits.
Best Practices for Securing WebSocket Applications
Developers should apply security controls throughout the WebSocket connection lifecycle rather than relying only on the initial handshake.
The following practices help protect real-time applications.
- Use WSS: Encrypt WebSocket traffic using TLS. Avoid transmitting sensitive information over unencrypted
ws://connections. - Authenticate connections: Require valid authentication before granting access to protected functionality.
- Enforce message-level authorization: Check permissions for every sensitive action and resource requested through a message.
- Validate origins: Use an explicit allowlist of trusted origins to reduce Cross-Site WebSocket Hijacking risks.
- Validate message schemas: Check message types, required fields, data types, and permitted values on the server.
- Apply rate limits: Limit connection attempts and message frequency based on application requirements.
- Restrict message sizes: Set maximum payload sizes and reject oversized messages.
- Manage sessions: Terminate or restrict connections when sessions expire, users log out, or access is revoked.
- Avoid trusting client-side roles: Determine permissions using trusted server-side session or identity information.
- Protect sensitive data: Send only the information required by the authorized user.
- Log security events: Record authentication failures, rejected messages, suspicious activity, and authorization violations.
- Handle errors safely: Avoid exposing stack traces, internal identifiers, or sensitive application details in WebSocket error messages.
For applications that support multiple tenants, ensure that every subscription, channel, and message operation enforces tenant isolation. A user authenticated within one tenant should not be able to access another tenant’s data by changing a client-controlled identifier.
WebSocket Security Testing Checklist
Use the following checklist when assessing a WebSocket-enabled application.
| Test Area | What to Verify | Expected Secure Behavior |
|---|---|---|
| Authentication | Connect without valid credentials | Unauthorized connections rejected |
| Session handling | Use expired or revoked sessions | Access restricted |
| Origin validation | Connect from an untrusted origin | Untrusted browser origins rejected |
| Message authorization | Modify user or resource identifiers | Unauthorized access blocked |
| Role validation | Attempt privileged actions with a low-privilege account | Restricted actions rejected |
| Input validation | Send malformed or unexpected messages | Messages safely rejected |
| Injection | Test inputs processed by backend components | Unsafe input cannot trigger injection |
| Data exposure | Subscribe to unauthorized channels | Private information remains protected |
| Rate limiting | Send repeated messages | Excessive activity controlled |
| Message size | Submit oversized payloads | Payload limits enforced |
| Error handling | Trigger invalid operations | No sensitive internal details exposed |
| Session termination | Log out while connection remains active | Connection follows session revocation policy |
The checklist should be adapted to the application’s architecture, user roles, and business requirements.
Real-World Scenarios Where WebSocket Security Matters
WebSocket vulnerabilities can affect different types of applications.
Financial and Trading Platforms
Trading platforms use real-time communication to deliver price updates, order notifications, and account information.
Weak authorization may allow a user to subscribe to another customer’s private account stream or attempt restricted trading operations.
Healthcare Applications
Healthcare platforms may use WebSockets for live notifications, patient dashboards, and communication between medical staff.
A missing authorization check could expose sensitive patient information.
Online Collaboration Tools
Collaboration platforms use persistent connections for document updates, chat messages, and shared workspaces.
Improper access controls may allow unauthorized users to join private channels or receive restricted messages.
Multiplayer Games
Online games often exchange player positions, scores, actions, and session events through real-time communication.
Weak server-side validation may allow manipulated messages to affect game state or other users.
These examples demonstrate why WebSocket security should be considered part of application security testing rather than treated as a separate networking concern.
Relevant Security References
The following resources provide useful technical guidance for developers and penetration testers.
OWASP WebSocket Security
The OWASP WebSocket Security Cheat Sheet provides practical recommendations for securing WebSocket connections, including origin validation, authentication, authorization, input validation, and logging.
OWASP Web Security Testing Guide
The OWASP Web Security Testing Guide provides structured guidance for testing web application security controls.
OWASP API Security Top 10
The OWASP API Security Top 10 covers authorization and authentication weaknesses that can also affect applications using WebSockets.
RFC 6455
RFC 6455 defines the WebSocket protocol, including the handshake process, framing, and communication behavior.
Frequently Asked Questions (FAQs)
1. What is WebSocket security testing?
WebSocket security testing is the process of evaluating persistent, bidirectional application connections for vulnerabilities. It includes testing authentication, message-level authorization, input validation, session handling, origin validation, and resource controls.
2. What are the most common WebSocket vulnerabilities?
Common WebSocket vulnerabilities include missing authentication, broken message-level authorization, Cross-Site WebSocket Hijacking, insecure origin validation, injection flaws, sensitive data exposure, and denial-of-service risks.
3. What is Cross-Site WebSocket Hijacking?
Cross-Site WebSocket Hijacking is an attack in which a malicious website attempts to establish a WebSocket connection to a vulnerable application using a victim’s authenticated browser session. Weak origin validation and unsafe cookie-based authentication can make this possible.
4. How do you test WebSocket authorization?
Capture a legitimate WebSocket message using an authorized test account. Modify resource identifiers, channel names, or action parameters and observe the server response. If the server returns information or performs an operation outside the user’s permissions, an authorization weakness may exist.
5. Is WebSocket communication encrypted?
WebSocket communication can be encrypted using WSS, which operates over TLS. The unencrypted ws:// scheme does not provide transport encryption. Sensitive production applications should use WSS.
6. Which tools are best for WebSocket penetration testing?
Burp Suite, OWASP ZAP, browser developer tools, wscat, and Python WebSocket libraries are useful for inspecting handshakes, modifying messages, testing authorization, and analyzing server responses.
7. Does WebSocket authentication need to be checked for every message?
The initial connection should be authenticated, but applications must also enforce authorization for every sensitive message. They should revalidate session state when required by the application’s security design, especially for long-lived connections.
8. How can developers prevent WebSocket vulnerabilities?
Developers should use WSS, authenticate connections, validate trusted origins, enforce message-level authorization, validate incoming data, apply rate limits, manage session expiration, and monitor suspicious activity.
Conclusion
WebSockets make modern applications more responsive by supporting continuous communication between clients and servers. However, their persistent nature creates security challenges that cannot be addressed through handshake authentication alone.
Effective WebSocket security testing must examine the entire communication lifecycle. This includes connection authentication, origin validation, message-level authorization, input handling, session management, and resource protection.
One of the most important lessons is that an authenticated connection does not automatically authorize every action performed through it. Servers must verify permissions for each sensitive message and ensure users can access only the resources assigned to them.
Organizations should include WebSocket endpoints in regular vulnerability assessments and penetration tests, particularly when their applications handle financial information, customer records, private conversations, or other sensitive data.
At PentestHint, we focus on helping cybersecurity professionals build practical application security and penetration testing skills. Explore our cyber security labs to practise identifying and validating security weaknesses in realistic environments.
Secure the connection, validate every message, and never assume that an authenticated WebSocket user is authorized to perform every action.