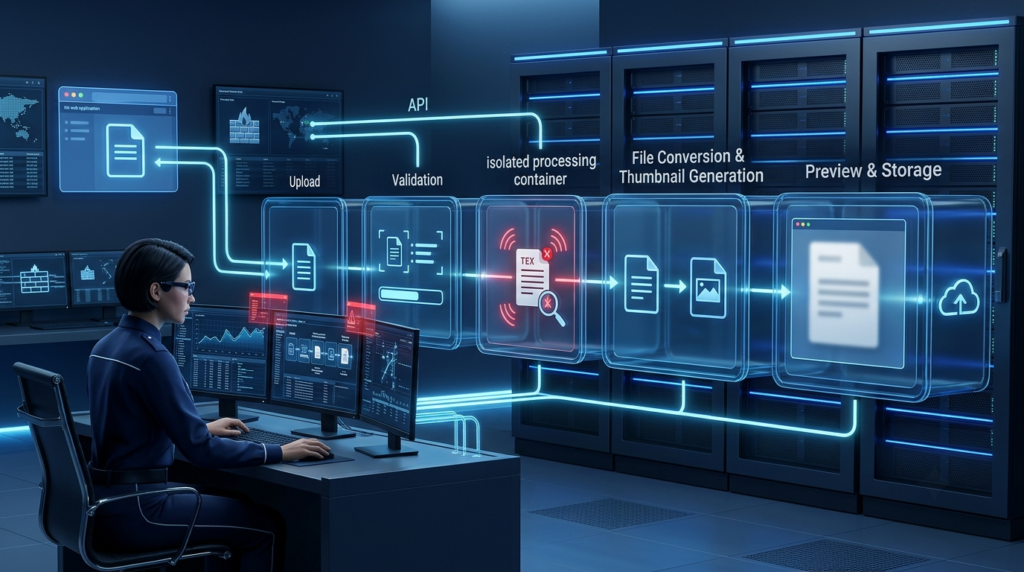
File uploads are a common feature in modern web applications. Users upload profile pictures, invoices, identity documents, reports, spreadsheets, videos, and other files every day. Behind a simple upload button, however, an application may run several backend operations, including file validation, malware scanning, conversion, thumbnail generation, preview rendering, and storage.
File Processing Pipeline Security focuses on identifying vulnerabilities across these connected operations. A file that passes the initial upload check may still cause problems during conversion or preview generation. An unsafe document processor, poorly isolated conversion service, or incorrectly configured storage system can expose sensitive data and create opportunities for server-side attacks.
These risks affect content management systems, document management platforms, online office applications, e-commerce websites, recruitment portals, and cloud storage services. As applications increasingly rely on automated document processing and third-party libraries, security testing must cover the complete file lifecycle rather than checking only the upload endpoint.
This guide explains how file processing pipelines work, where vulnerabilities commonly appear, how penetration testers can assess each stage, and which controls developers should implement to reduce risk.
What Is a File Processing Pipeline?
A file processing pipeline is a sequence of operations that an application performs after receiving a file from a user or external system.
The pipeline may inspect the file, validate its format, scan it for malicious content, transform it into another format, generate a preview, and store the final result.
For example, when a user uploads a PDF to an online document management platform, the application might:
- Receive the uploaded PDF.
- Check its size and permitted file type.
- Validate its structure.
- Scan it for malware.
- Extract metadata.
- Generate a thumbnail or preview.
- Store the original and processed files.
- Make the document available to authorized users.
Each operation introduces a potential security boundary.
A weakness in one stage can affect the entire application. A file may pass upload validation but exploit a vulnerable conversion library later in the process.
Common Components of a File Processing Pipeline
A typical pipeline contains several components.
Upload handler: Receives files through an HTTP endpoint or application interface.
Validation service: Checks file extensions, MIME types, size limits, and other permitted properties.
Malware scanning service: Examines uploaded content for known malicious patterns.
Conversion engine: Changes files into formats such as PDF, PNG, JPEG, or HTML.
Preview generator: Creates thumbnails, document previews, or extracted text.
Metadata extractor: Reads properties such as author, dimensions, creation date, and document information.
Storage service: Saves original and processed files.
Delivery service: Allows authorized users to download or view stored content.
Not every application uses all these components. Some applications process files synchronously, while others place uploaded files into background queues for asynchronous processing.
Why File Processing Pipeline Security Is Important
File processing services handle untrusted content. Even when a file comes from an authenticated user, the application should not assume that its contents are safe.
An attacker may create a file that appears valid but contains unexpected structures, malicious metadata, embedded content, or data designed to trigger a vulnerability in a parser.
Important reasons to assess file processing security include:
1. Uploaded Files Can Contain Malicious Content
An attacker may upload a file designed to exploit a vulnerable parser or processing library.
If the backend processes that file without sufficient isolation, the vulnerability may affect the application server or processing environment.
2. Conversion Services Expand the Attack Surface
Applications often use external tools and libraries to convert documents and images.
For example, a document uploaded as a Word file may be converted into PDF before previewing. The conversion engine becomes another component that must safely handle untrusted input.
3. Preview Features Can Expose Sensitive Information
Preview services may extract text, render documents, or load embedded resources.
If they process files insecurely, they may expose internal information or create opportunities for server-side request forgery and other attacks.
4. Temporary Files Can Create Security Problems
Processing services often create temporary copies of uploaded files.
If these files are stored in publicly accessible directories, retained longer than necessary, or assigned predictable names, attackers may gain access to sensitive content.
5. File Processing Often Involves Third-Party Dependencies
Applications may rely on image libraries, PDF parsers, archive handlers, office document converters, and media processing tools.
An outdated or vulnerable dependency can expose the pipeline even when the application’s own code appears secure.
How a File Processing Pipeline Works
Understanding the normal processing sequence helps testers identify where security controls should exist.
Stage 1: File Upload
The browser sends a file to the application through an HTTP request.
A typical request may look like this:
POST /api/files/upload HTTP/1.1
Host: example.com
Content-Type: multipart/form-data; boundary=----Boundary123
Authorization: Bearer <access_token>

------Boundary123
Content-Disposition: form-data; name="file"; filename="report.pdf"
Content-Type: application/pdf

[File content]
------Boundary123--
The backend receives the file and may temporarily store it before further processing.
Security testing at this stage should examine authentication, authorization, upload restrictions, size limits, and filename handling.
Stage 2: File Validation
The application checks whether the uploaded file is permitted.
Common validation methods include:
- Filename extension checks.
- MIME type inspection.
- File signature or magic-byte verification.
- File size restrictions.
- Content structure validation.
- Business-specific upload rules.
No single validation method is sufficient.
For example, the Content-Type header is supplied by the client and can be modified. A request claiming to contain an image does not prove that the uploaded content is actually a valid image.
Stage 3: Malware Scanning
Some applications scan uploaded files before making them available.
A scanning service may use antivirus signatures, file reputation, or additional inspection techniques.
Testers should verify that files cannot bypass required scanning steps and that the application handles scanning failures safely.
A scanner should not be treated as a complete replacement for secure parsing and isolated processing.
Stage 4: File Conversion
Applications may convert uploaded files into other formats.
Examples include:
- DOCX to PDF.
- PDF to images.
- SVG to PNG.
- Video to compressed formats.
- Audio to streaming formats.
- Images to thumbnails.
Conversion tools process complex file structures. A vulnerable parser or unsafe command invocation can introduce serious security risks.
Stage 5: Preview Generation
Preview services display files inside the application without requiring users to download them.
They may use browser rendering, server-side conversion, document extraction, or thumbnail generation.
Preview functionality should be assessed separately from upload functionality because it may use different libraries, permissions, and execution environments.
Stage 6: Storage and File Delivery
The application stores the original and processed files and provides access to authorized users.
Security controls should ensure that files cannot be retrieved by changing identifiers, guessing filenames, or accessing public storage paths.
Common Vulnerabilities in File Processing Pipelines
1. Unrestricted File Upload
Unrestricted file upload occurs when an application accepts files without properly limiting their type, content, size, or intended use.
For example, a profile image feature may accept any uploaded content because it checks only the filename extension.
A tester should verify whether the application relies on weak extension checks or trusts client-provided MIME types.
Testing approach:
- Identify upload endpoints and permitted file types.
- Inspect filename and MIME type validation.
- Compare file extensions with actual file signatures.
- Test unexpected but harmless file formats in an authorized environment.
- Check whether the server stores uploads in an executable location.
- Verify that rejected files are not accessible afterward.
The impact depends on how the application processes and serves uploaded content.
2. MIME Type and File Signature Validation Issues
MIME types describe the media format of a file, but the value supplied in an HTTP request can be manipulated.
An application that trusts the request’s Content-Type header may accept content that does not match its declared format.
For example, a request may identify a file as:
Content-Type: image/jpegeven when the file contains something else.
A stronger implementation checks the file’s actual structure and signature, validates it with an appropriate parser, and applies business-specific restrictions.
3. Path Traversal Through Filenames
Some applications use uploaded filenames when creating server-side storage paths.
If the application does not safely normalize and handle filenames, an attacker may attempt to access or overwrite files outside the intended upload directory.
For example, a poorly implemented application might construct a storage path directly from a user-controlled filename.
Testing should examine whether filenames are replaced with server-generated identifiers and whether path normalization prevents directory traversal.
Applications should never rely on user-supplied filenames as trusted filesystem paths.
4. Server-Side Request Forgery in Preview Services
Server-Side Request Forgery (SSRF) can occur when a backend service makes network requests based on attacker-controlled input.
Some preview systems retrieve remote images, import documents from URLs, or load external resources during rendering.
If the application accepts arbitrary URLs and the backend retrieves them without appropriate restrictions, an attacker may attempt to make the server access internal resources.
Example scenario:
A document preview feature accepts a remote image URL. The backend downloads the image before rendering the document.
If the service does not restrict destination addresses and network access, it may be abused to reach internal services.
Testing approach:
- Identify features that retrieve remote files or resources.
- Determine whether the backend makes outbound requests.
- Use an authorized external callback endpoint to observe request behavior.
- Review how redirects and DNS resolution are handled.
- Verify that internal and sensitive network destinations are blocked.
SSRF testing must be performed carefully to avoid accessing systems outside the agreed testing scope.
5. Vulnerable Document and Image Parsers
File conversion and preview services rely on parsers that interpret complex file formats.
A parser vulnerability may lead to denial of service, memory corruption, information disclosure, or in some cases remote code execution.
For example, an outdated image processing library may contain a known vulnerability triggered by a specially crafted image.
Testers should identify the libraries and versions used by the application, review security advisories, and verify whether vulnerable components process untrusted files.
Relevant sources include the MITRE CVE database and vendor security advisories.
6. XML External Entity (XXE) Processing
Some document formats use XML internally. Office documents, SVG files, and other XML-based formats may be processed by libraries that support external entity resolution.
If an XML parser allows unsafe external entity processing, an attacker may attempt to access local files or trigger server-side requests.
Testing should determine whether XML parsing is involved and whether external entities, DTD processing, and external resource resolution are disabled where unnecessary.
Use controlled test files and non-sensitive targets during authorized assessments.
7. Archive Extraction Vulnerabilities
Applications may accept ZIP archives or other compressed files.
A dangerous extraction implementation may allow archive entries to escape the intended extraction directory. This is commonly associated with path traversal during archive extraction, sometimes called Zip Slip.
Other archive risks include:
- Excessive decompression ratios.
- Extremely large extracted files.
- Nested archives.
- Unexpected symbolic links.
- Duplicate filenames.
- Excessive file counts.
These issues can lead to file overwrites, storage exhaustion, or access to unintended locations.
8. Insecure Temporary File Handling
Processing services often create temporary files while converting or previewing documents.
Problems occur when temporary files:
- Use predictable names.
- Have overly broad filesystem permissions.
- Remain accessible through public web directories.
- Are not deleted after processing.
- Are shared between users without proper isolation.
Testers should examine whether temporary content can be accessed by another user or retrieved through predictable paths.
9. Cross-Site Scripting Through File Previews
Some file formats can contain active content or markup.
For example, SVG files support XML-based markup and can contain elements that require careful handling when rendered in a browser.
If an application displays uploaded content directly from its main application origin without appropriate restrictions, unsafe rendering may introduce cross-site scripting or related browser security risks.
Testing should examine:
- Whether files are rendered inline or downloaded.
- Which origin serves uploaded content.
- Whether HTML and SVG content is sanitized or safely isolated.
- Whether appropriate content types and security headers are applied.
- Whether previews use a separate, restricted origin.
10. Denial of Service Through Resource-Intensive Files
A file may be valid but require excessive resources to process.
Examples include:
- Very large images.
- Documents with thousands of pages.
- Highly compressed archives.
- Complex vector graphics.
- Media files with unusual dimensions or duration.
- Files designed to trigger excessive parser work.
An attacker may use these files to consume CPU, memory, disk space, or processing capacity.
Applications should enforce limits on file size, extracted size, page count, dimensions, processing time, and concurrent jobs.
How to Perform File Processing Pipeline Security Testing
A complete assessment should examine every stage that handles untrusted files.
Step 1: Discover File Upload and Processing Features
Explore the application and identify every place where users can upload or import content.
Common features include:
- Profile image uploads.
- Document attachments.
- Invoice submissions.
- Resume uploads.
- Media galleries.
- Document previews.
- Bulk archive imports.
- Remote URL imports.
Record the endpoint, supported formats, user permissions, and expected processing behavior.
Step 2: Map the Complete Processing Flow
Determine what happens after an upload.
Ask questions such as:
- Is the file scanned?
- Is it converted?
- Does the application extract metadata?
- Is a preview generated?
- Is processing synchronous or asynchronous?
- Where are temporary files stored?
- Where are final files stored?
- Which service delivers the processed file?
This helps identify components that may not be visible from the upload interface.
Step 3: Inspect Upload Requests
Use an intercepting proxy such as Burp Suite to capture the upload request.
Review:
- HTTP method and endpoint.
- Authentication requirements.
- Filename handling.
- MIME type.
- File extension.
- Request size.
- Additional metadata fields.
- Response behavior.
Determine whether the server performs validation or simply trusts the values provided by the browser.
Step 4: Test File Type Validation
Use harmless test files to verify whether the application correctly checks file types.
Compare declared MIME types, extensions, and actual file formats.
Check whether the application rejects unsupported files consistently across different upload endpoints.
Do not assume that one upload feature uses the same validation rules as another.
Step 5: Test Conversion and Preview Services
Identify the file formats processed by external tools or backend libraries.
Test whether the application safely handles malformed, unusually structured, or unsupported files.
Observe:
- Conversion errors.
- Processing time.
- Resource usage.
- Error messages.
- Generated preview content.
- Whether failed files remain accessible.
Avoid tests that could crash production services or damage stored documents.
Step 6: Test Storage and Access Controls
After uploading a test file, examine how the application stores and delivers it.
Verify whether:
- Another user can access the file without permission.
- File identifiers can be modified to retrieve other users’ content.
- Temporary files remain accessible.
- Storage paths expose sensitive information.
- Deleted files remain retrievable.
- Public URLs provide access beyond the intended scope.
This stage often reveals IDOR and insecure direct object reference issues in file management features.
Step 7: Review Processing Dependencies
Identify the libraries and external tools used for conversion, parsing, scanning, and preview generation.
Review their versions and security advisories.
Check whether the application uses maintained dependencies and whether security patches have been applied.
Do not assume a component is vulnerable merely because its version appears old. Confirm whether the affected functionality and vulnerable code path are present.
Step 8: Validate Findings and Document Evidence
For each confirmed issue, document:
- Vulnerability name.
- Affected endpoint or processing component.
- File format involved.
- Required user permissions.
- Reproduction steps.
- Relevant request and response evidence.
- Security impact.
- Recommended remediation.
A useful report explains not only how a file was accepted, but also what happened when the application processed or delivered it.
Practical Example: Exploiting an Unsafe Document Preview Workflow
Consider an online document management platform that allows employees to upload PDF and office documents.
After an upload, the application sends the document to a backend conversion service. That service generates a PDF preview and stores it in a shared storage location.
During testing, a penetration tester identifies that the preview service retrieves external resources referenced by certain document content.
The tester uses a controlled test environment and an external callback endpoint to determine whether the backend makes outbound requests while processing the document.
The callback confirms that the preview service attempts to retrieve an external resource.
Further testing reveals that the service does not adequately restrict outbound destinations.
Potential security impact:
- The backend may access internal services.
- Sensitive internal endpoints may be exposed.
- The processing environment may reveal information through error responses.
- Other systems may be affected if the service has excessive network permissions.
Recommended remediation:
The organization should restrict outbound network access from the conversion service, disable unnecessary external resource loading, validate remote destinations, and isolate document processing from sensitive internal infrastructure.
This example demonstrates why testing should continue beyond the upload endpoint. The weakness exists in the processing stage, not necessarily in the initial file acceptance logic.
Tools Used for File Processing Pipeline Security Testing
Different tools help assess file validation, parsing, conversion, storage, and application behavior.
Burp Suite
Burp Suite helps intercept and modify HTTP requests and responses.
It is useful for:
- Inspecting multipart upload requests.
- Testing filename and MIME type handling.
- Modifying file metadata.
- Reviewing upload authorization.
- Testing file access controls.
- Replaying requests.
OWASP ZAP
OWASP ZAP can help inspect web application traffic and identify common vulnerabilities.
It can support initial testing, although file processing issues often require manual review of the backend workflow.
ExifTool
ExifTool reads and edits metadata in many image, audio, video, and document formats.
It can help testers understand how applications handle metadata and whether sensitive information is exposed through uploaded files.
ClamAV
ClamAV is an open-source antivirus engine that can be used to scan files for known malicious content.
It can help organizations evaluate malware scanning integration. However, antivirus scanning does not replace file validation, parser security, or sandboxing.
OWASP Dependency-Check
OWASP Dependency-Check identifies known vulnerabilities in project dependencies.
It can help developers review libraries used by file processing services and identify components that require updates.
File Format Inspection Tools
Depending on the formats supported by an application, testers may also use:
filefor identifying file types.pdfinfofor inspecting PDF properties.unzipfor reviewing archive contents.- ImageMagick utilities for image inspection and conversion.
- MediaInfo for audio and video metadata.
- Browser developer tools for preview behavior.
Use these tools only on files and systems within the authorized testing scope.
Best Practices to Secure File Processing Pipelines
Developers should treat every uploaded file as untrusted, regardless of the user’s identity or the file’s declared format.
1. Use Allowlisted File Types
Define which file formats the application actually needs.
Validate file extensions, MIME types, file signatures, and content structure. Avoid accepting arbitrary formats when they are not required.
2. Generate Server-Side Filenames
Replace user-supplied filenames with randomly generated identifiers.
Store the original filename as metadata if the application needs to display it. Do not use it directly to construct filesystem paths.
3. Store Uploads Outside the Web Root
Uploaded files should not be stored in directories where the web server can execute them.
Use controlled storage locations and deliver files through an authorization-aware service.
4. Isolate Conversion Services
Run file converters and preview generators in restricted environments.
Use containers or sandboxing with:
- Limited filesystem access.
- Restricted network access.
- Non-privileged accounts.
- Resource limits.
- Separate temporary directories.
- Strict process permissions.
5. Keep Processing Libraries Updated
Maintain PDF parsers, image libraries, archive tools, media processors, and other dependencies.
Monitor security advisories and remove components that are no longer required.
6. Enforce File and Resource Limits
Set limits for:
- Maximum upload size.
- Maximum extracted archive size.
- Number of archive entries.
- Image dimensions.
- Document page count.
- Processing time.
- Concurrent processing jobs.
- Temporary storage usage.
These controls help reduce denial-of-service risks.
7. Secure File Previews
Serve untrusted previews from an isolated origin where possible.
Apply appropriate content types and security headers. Avoid rendering active content directly within the trusted application origin.
8. Restrict Outbound Network Access
Conversion and preview services should not have unrestricted access to internal networks.
Use network controls to prevent processing services from reaching sensitive infrastructure unless explicitly required.
9. Protect File Access with Authorization
Every download and preview request should verify whether the authenticated user can access the requested file.
Do not rely on unpredictable filenames or hidden URLs as the only access control.
10. Monitor Processing Activity
Log important events such as:
- Upload attempts.
- Validation failures.
- Malware scan results.
- Conversion errors.
- Processing timeouts.
- Unusual resource consumption.
- File access failures.
Monitoring helps security teams detect suspicious activity and investigate incidents.
Common Mistakes During File Processing Security Testing
Testers can miss serious vulnerabilities when they focus only on the upload form.
Common mistakes include:
- Testing file extensions but not actual file content.
- Trusting client-provided MIME types.
- Ignoring conversion and preview services.
- Overlooking temporary storage.
- Failing to test file access across different user accounts.
- Ignoring metadata extraction.
- Not reviewing third-party processing libraries.
- Overlooking archive extraction behavior.
- Testing only small and simple files.
- Treating antivirus scanning as complete protection.
- Ignoring outbound network requests made by preview services.
A complete assessment follows the file from initial upload to final delivery.
Career Opportunities in File Processing Security
Understanding file processing security is useful for professionals working in web application penetration testing, API security, cloud security, and application security engineering.
Relevant roles include:
- Web Application Penetration Tester.
- Junior Penetration Tester.
- Application Security Analyst.
- API Security Tester.
- Security Consultant.
- Cloud Security Engineer.
- Product Security Engineer.
- Bug Bounty Researcher.
Professionals should develop a strong understanding of HTTP, file formats, web application architecture, backend processing, operating system permissions, and secure storage.
Structured “https://academy.pentesthint.com/” cyber security training can help build the required foundation. Practising in authorized “https://vuln.pentesthint.com/” vulnerability labs can also help learners understand how upload and processing vulnerabilities appear in real applications.
Future Scope of File Processing Pipeline Security
File processing systems are becoming more complex as organizations adopt cloud storage, automated document workflows, and third-party conversion services.
Several areas will remain important for security professionals.
Cloud-Based File Processing
Applications increasingly use managed storage and serverless processing services.
Security testing must consider cloud permissions, temporary object storage, signed URLs, event triggers, and access policies.
Microservices and Asynchronous Processing
A file may pass through multiple services before it becomes available to a user.
Each service must enforce its own security requirements and avoid trusting data simply because another internal service supplied it.
Software Supply Chain Security
File processing depends heavily on third-party libraries.
Dependency monitoring, secure build pipelines, software inventories, and timely patching will remain essential.
Stronger Isolation and Sandboxing
Organizations are adopting isolated processing environments to reduce the impact of malicious files.
Restricted containers, sandboxed parsers, and network segmentation can limit what a compromised processing component can access.
Automated Security Monitoring
Security teams can monitor unusual file types, processing failures, unexpected outbound requests, and abnormal resource consumption.
These signals can help detect suspicious activity earlier in the file lifecycle.
Conclusion
File processing pipeline security is not limited to checking whether an upload endpoint accepts the correct file extension. It requires a complete assessment of how an application validates, scans, converts, previews, stores, and delivers untrusted content.
Common risks include unrestricted uploads, unsafe file parsing, SSRF, XXE, archive extraction vulnerabilities, insecure temporary files, preview-based XSS, and resource exhaustion.
The most effective approach is to follow each file through the entire processing lifecycle and verify that every component applies appropriate security controls.
For developers, this means using strict validation, isolated processing environments, secure storage, updated dependencies, and reliable authorization checks. For penetration testers, it means looking beyond the upload form and understanding the backend services that handle the file.
To explore more application security resources and professional security guidance, visit “https://pentesthint.com/” PentestHint.