File Processing Pipeline Security: Testing Upload and Preview Risks
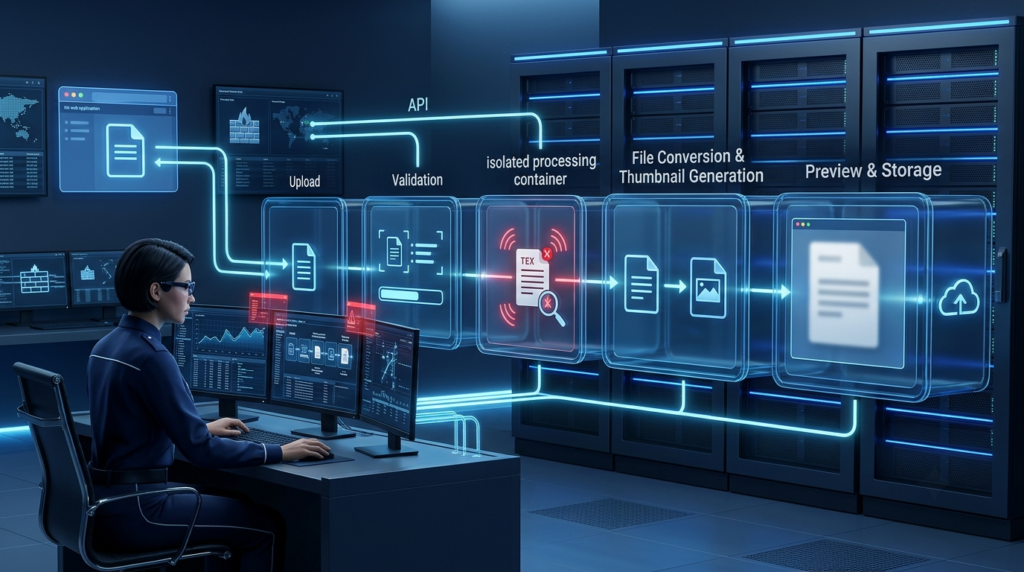
File uploads are a common feature in modern web applications. Users upload profile pictures, invoices, identity documents, reports, spreadsheets, videos, and other...
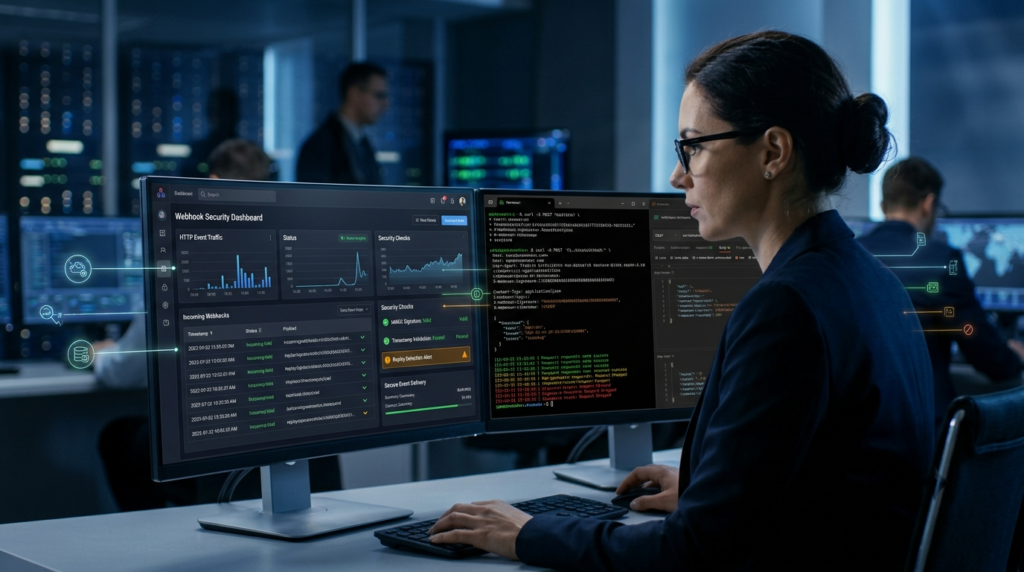
Webhook Security Testing is an important part of modern API security because webhooks allow external applications and services to send event notifications...
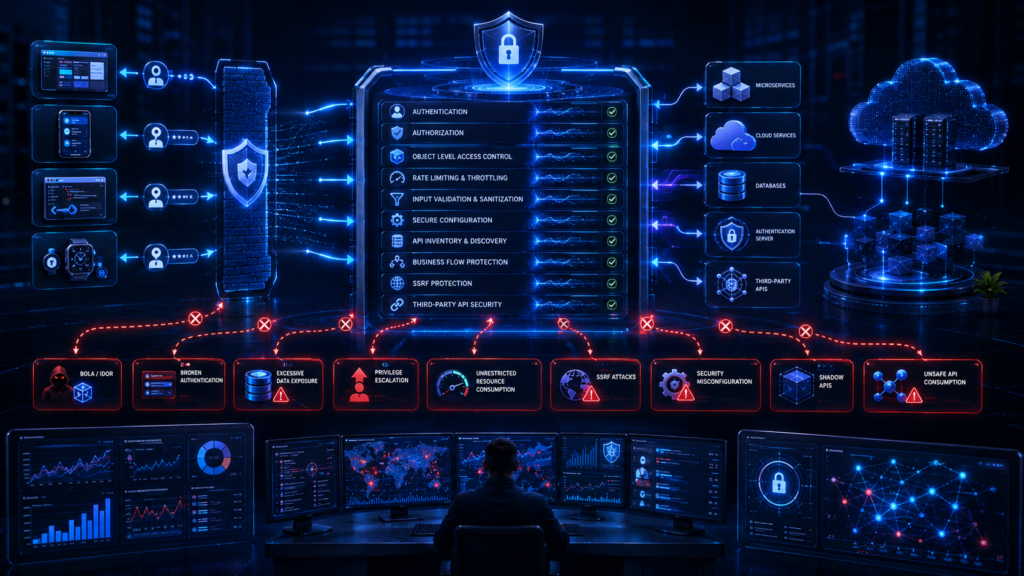
APIs are now at the center of modern applications. Mobile apps, SaaS platforms, cloud services, payment systems, microservices, and third-party integrations all...
Server-Side Request Forgery (SSRF) is a web application security vulnerability that allows an attacker to influence requests made by a server. Instead...
XML remains widely used across enterprise applications, APIs, document processing systems, SOAP web services, and data exchange platforms. While many organizations have...
Server-Side Request Forgery (SSRF) is one of the most dangerous web application vulnerabilities affecting modern organizations. As cloud computing, APIs, microservices, and...