Server-Side Request Forgery (SSRF) is one of the most dangerous web application vulnerabilities affecting modern organizations. As cloud computing, APIs, microservices, and third-party integrations continue to dominate application development, SSRF attacks have become increasingly attractive to attackers.
Unlike traditional attacks that target users directly, SSRF allows an attacker to abuse a vulnerable server and force it to send requests on their behalf. This capability can expose internal services, cloud metadata endpoints, sensitive data, and even lead to remote system compromise.
The growing adoption of cloud-native architectures has increased the importance of understanding SSRF vulnerabilities. Security teams, developers, and penetration testers must understand how SSRF works, how attackers exploit it, and how organizations can defend against it.
This guide explores SSRF attack vectors, real-world incidents, exploitation techniques, detection methods, and practical mitigation strategies that can significantly reduce risk.
What is Server-Side Request Forgery (SSRF)?
Server-Side Request Forgery occurs when an application accepts user-controlled input and uses it to make server-side requests without proper validation.
In a vulnerable application, attackers can manipulate URLs or request parameters and force the server to access resources that should not be reachable.
For example:
POST /fetch-image

{
  "url":"https://example.com/image.jpg"
}
The application downloads the image from the supplied URL.
An attacker may replace the URL with:
http://localhost/adminor
http://169.254.169.254/If the application processes the request without validation, sensitive internal resources may become accessible.
According to the OWASP SSRF Guide, SSRF vulnerabilities can lead to severe security consequences, especially in cloud environments.
Why SSRF Vulnerabilities Matter
SSRF vulnerabilities are particularly dangerous because they allow attackers to leverage the trust relationship of the vulnerable server.
Potential impacts include:
- Internal network discovery
- Access to cloud metadata services
- Credential theft
- Sensitive data exposure
- Remote code execution in specific scenarios
- Lateral movement within internal networks
Many organizations deploy strong perimeter security controls while assuming internal resources are trusted. SSRF attacks exploit this assumption.
For professionals pursuing cyber security training, SSRF remains an essential topic due to its frequent appearance in bug bounty programs and penetration testing engagements.
How SSRF Works
The Basic Concept
Applications often retrieve resources from external systems.
Common examples include:
- Importing images
- Fetching web content
- URL previews
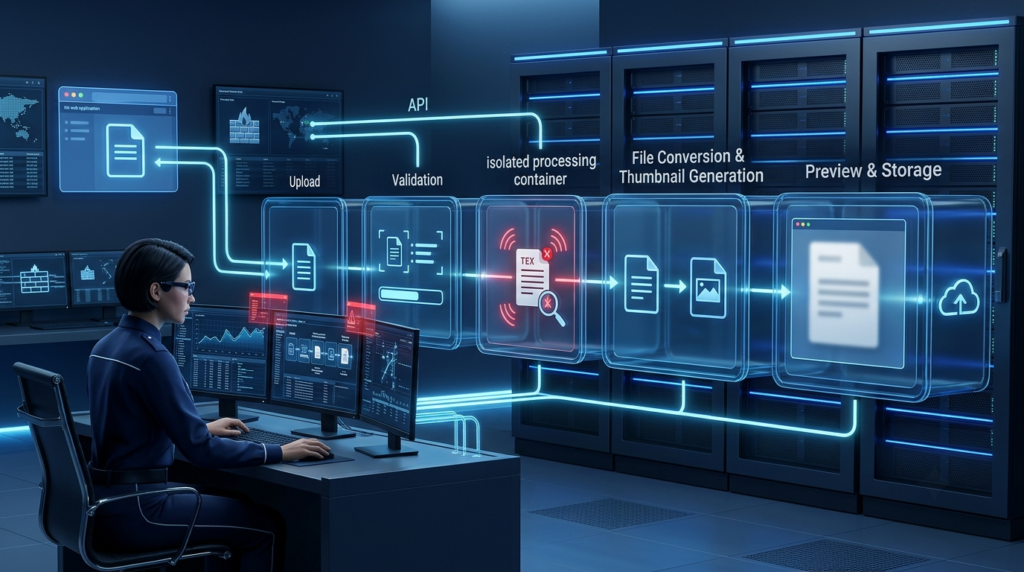
- Document conversion services
- Third-party API integrations
A vulnerable application may allow users to specify a URL without validating its destination.
Instead of requesting:
https://example.com/profile.pngAn attacker may supply:
http://internal-server.local/adminThe application unknowingly retrieves internal resources and returns the response.
Trust Exploitation
The server often has access to:
- Internal applications
- Databases
- Cloud services
- Administrative interfaces
Attackers exploit these trusted connections to bypass external security controls.
Common SSRF Attack Vectors
URL Parameter Manipulation
Many applications accept URLs directly from users.
Example:
GET /preview?url=https://example.comManipulating the URL parameter can trigger SSRF.
File Import Features
Applications that import files from remote locations often introduce SSRF risks.
Examples include:
- PDF generators
- Image processors
- Data import tools
API Integrations
Modern applications frequently communicate with external APIs.
Improper URL validation may allow attackers to redirect requests toward internal systems.
Webhook Functionality
Webhooks commonly receive URLs supplied by users.
If validation is weak, attackers may target internal resources.
XML External Entities (XXE)
Some XXE vulnerabilities can trigger SSRF-like behavior by forcing servers to access external resources.
Types of SSRF Attacks
Basic SSRF
The attacker accesses an internal resource through a vulnerable server.
Example:
http://localhost/adminBlind SSRF
The attacker cannot see the server response directly.
Instead, they infer success through:
- DNS interactions
- Timing differences
- Outbound network requests
Blind SSRF is common in mature environments.
Semi-Blind SSRF
The application returns limited information about the response, allowing partial reconnaissance.
Real-World SSRF Incidents
Capital One Cloud Breach
One of the most well-known SSRF incidents involved Capital One in 2019.
Attackers exploited an SSRF vulnerability to access AWS metadata services and obtain temporary credentials. This ultimately exposed sensitive customer information.
The incident highlighted the risks associated with cloud metadata endpoints.
Reference:
https://www.justice.gov/
Microsoft Azure Security Research
Security researchers have repeatedly demonstrated SSRF exploitation against cloud environments to access internal services and metadata endpoints.
Cloud providers now publish extensive security guidance to mitigate these risks.
Reference:
https://learn.microsoft.com/
Bug Bounty Discoveries
Major organizations including technology companies, e-commerce platforms, and SaaS providers regularly receive SSRF reports through bug bounty programs.
Many high-severity reports involve:
- Internal API access
- Metadata service exposure
- Sensitive configuration disclosure
SSRF in Cloud Environments
AWS Metadata Service
One of the most targeted SSRF endpoints is:
http://169.254.169.254/latest/meta-data/This endpoint provides instance metadata.
Misconfigured cloud environments may expose:
- Temporary credentials
- Instance details
- IAM role information
Azure Metadata Service
Microsoft Azure provides metadata services accessible through internal addresses.
Improper filtering can expose cloud resources.
Google Cloud Metadata Service
Google Cloud also uses metadata endpoints that must be protected against SSRF attacks.
Cloud-native applications should carefully validate outbound requests.
Common SSRF Exploitation Techniques
Internal Port Scanning
Attackers can use SSRF to identify active services.
Example targets:
localhost:80
localhost:443
localhost:8080
localhost:3306
Metadata Service Access
Attackers attempt to access cloud metadata endpoints.
These often contain valuable information.
Internal API Enumeration
Organizations commonly expose administrative APIs internally.
SSRF can provide access to these services.
Service Discovery
Attackers identify:
- Databases
- Management consoles
- Monitoring systems
- Container services
Chained Exploitation
SSRF often acts as an initial foothold.
Attackers may combine SSRF with:
- Remote code execution
- Authentication bypass
- Privilege escalation
Tools Used for SSRF Testing
Burp Suite
Burp Suite remains one of the most effective tools for SSRF testing.
Useful modules include:
- Repeater
- Collaborator
- Intruder
Official site:
OWASP ZAP
OWASP ZAP provides a free platform for SSRF testing and web application assessments.
Official site:
Interactsh
Interactsh assists in detecting blind SSRF vulnerabilities.
Official site:
https://github.com/projectdiscovery/interactsh
Nuclei
Nuclei includes templates capable of identifying SSRF-related issues.
Official site:
https://github.com/projectdiscovery/nuclei
Professionals can safely practice SSRF techniques within hands-on labs and controlled environments before testing production systems.
How to Detect SSRF Vulnerabilities
Review User-Controlled Inputs
Identify parameters accepting:
- URLs
- Hostnames
- IP addresses
- Webhooks
Monitor Outbound Requests
Unexpected outbound traffic often indicates SSRF activity.
Analyze Application Logs
Look for:
- Internal IP access attempts
- Metadata endpoint requests
- Suspicious DNS lookups
Conduct Security Assessments
Regular penetration testing helps uncover SSRF weaknesses before attackers do.
Organizations frequently use professional VAPT services to evaluate these risks.
Prevention and Mitigation Strategies
Implement URL Allowlisting
Only permit requests to trusted domains.
Avoid unrestricted URL fetching.
Block Internal Network Access
Applications should never access:
127.0.0.1
localhost
169.254.169.254
10.0.0.0/8
172.16.0.0/12
192.168.0.0/16
unless explicitly required.
Validate User Input
Validate:
- Protocols
- Domains
- IP addresses
- Redirect destinations
Disable Unnecessary Protocols
Restrict protocols such as:
- file://
- ftp://
- gopher://
where possible.
Use Network Segmentation
Separate sensitive services from internet-facing applications.
Restrict Metadata Access
Cloud providers recommend:
- AWS IMDSv2
- Azure security controls
- Google Cloud metadata protections
Apply Defense in Depth
Combine:
- Input validation
- Network controls
- Monitoring
- Access controls
for maximum protection.
Security Best Practices for Developers
Follow Secure Coding Standards
Use guidance from:
- OWASP
- NIST
- CISA
- Microsoft Security Documentation
Conduct Regular Security Reviews
Review:
- Third-party integrations
- API implementations
- URL fetching mechanisms
Train Development Teams
Organizations investing in online cyber security courses often reduce common application security mistakes.
Practice Secure Testing
Use dedicated vulnerability labs to validate security controls and improve detection capabilities.
Career Relevance of SSRF Knowledge
Understanding SSRF is valuable for:
- Penetration Testers
- Security Researchers
- Application Security Engineers
- SOC Analysts
- Bug Bounty Hunters
- Secure Software Developers
Many high-paying bug bounty programs classify SSRF findings as critical because of their potential impact.
Individuals looking to learn cyber security should prioritize SSRF alongside SQL Injection, XSS, and Broken Access Control.
Future Scope of SSRF Security
As organizations continue migrating to cloud-native architectures, SSRF will remain a major security concern.
Future trends include:
- Enhanced cloud metadata protections
- Automated SSRF detection
- Zero Trust networking
- API security automation
- Continuous security validation
Organizations that proactively address SSRF risks will be better equipped to secure modern infrastructures.
Conclusion
Server-Side Request Forgery (SSRF) is far more than a simple web application vulnerability. It can provide attackers with access to internal services, cloud metadata endpoints, sensitive credentials, and critical infrastructure components.
Understanding SSRF attack vectors, cloud-specific risks, exploitation methods, and defense strategies is essential for modern security teams. By implementing strong validation controls, network segmentation, outbound request restrictions, and continuous security testing, organizations can significantly reduce their exposure.
Whether you are a developer, security analyst, or penetration tester, mastering SSRF concepts is a valuable investment. For practical experience, security research, and advanced learning resources, explore PentestHint and strengthen your application security expertise.
FAQs
What is SSRF in cybersecurity?
SSRF is a vulnerability that allows attackers to force a server to make unauthorized requests to internal or external resources.
Why is SSRF considered dangerous?
SSRF can expose internal systems, cloud metadata services, credentials, and sensitive business data.
What is Blind SSRF?
Blind SSRF occurs when attackers cannot directly view responses but can confirm successful requests through external interactions.
Can SSRF lead to cloud account compromise?
Yes. SSRF vulnerabilities can expose cloud metadata services and temporary credentials if proper protections are not implemented.
How do penetration testers identify SSRF vulnerabilities?
They test user-controlled URL inputs, analyze outbound requests, use tools like Burp Collaborator, and validate server-side request handling.
What is the AWS metadata service?
It is an internal endpoint that provides information about cloud instances and may expose credentials if SSRF protections are missing.
How can developers prevent SSRF?
Developers should implement allowlisting, input validation, network segmentation, metadata protection, and outbound traffic restrictions.
Is SSRF part of the OWASP Top 10?
SSRF is recognized by OWASP as a significant web application security risk and appears in the OWASP Top 10 categories.