

Cyber Security
How to Build an Ethical Hacking Portfolio That Gets Noticed
Knowing how to perform a vulnerability scan or exploit a lab machine is useful, but it does not always show an employer...
Knowing how to perform a vulnerability scan or exploit a lab machine is useful, but it does not always show an employer...

The top mistakes beginners make in ethical hacking are usually not caused by a lack of tools. Most beginners can quickly install...

Career paths in offensive security have expanded significantly as organizations invest more heavily in penetration testing, application security, cloud security, adversary simulation,...
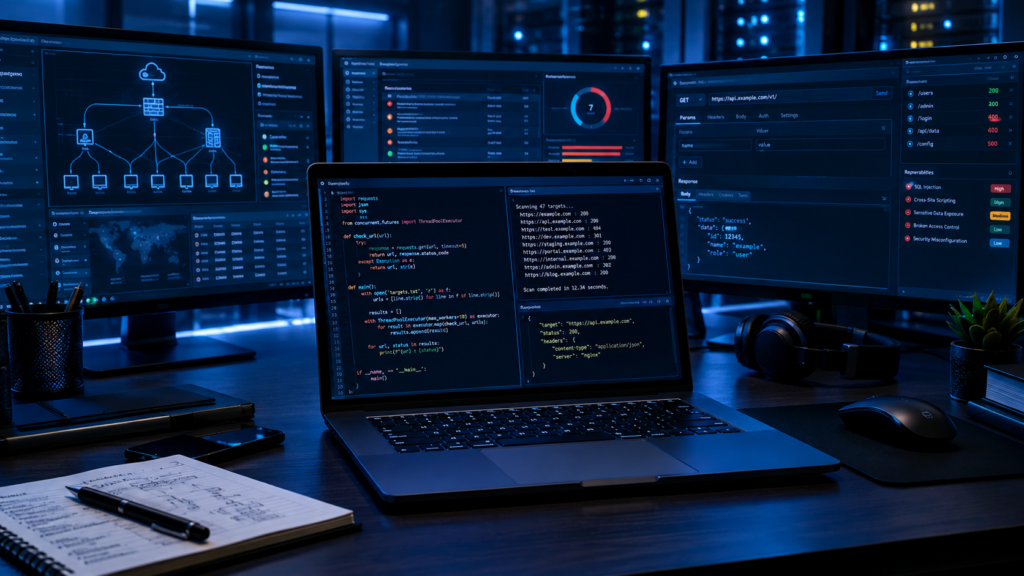
Python programming for ethical hackers is one of the most useful technical skills for anyone entering penetration testing, vulnerability assessment, bug bounty...

Learning cyber security from books and videos can build a strong foundation, but practical experience is what turns theoretical knowledge into usable...

Ethical hacking is one of the most practical areas of cybersecurity, but learning it does not necessarily require expensive courses or certifications....

Server-Side Request Forgery (SSRF) is a web application security vulnerability that allows an attacker to influence requests made by a server. Instead...

Cross-Site Request Forgery (CSRF) remains one of the most important web application security vulnerabilities despite significant improvements in browser security and modern...
File upload functionality is one of the most common features in modern web applications. Users upload profile pictures, documents, invoices, resumes, and...

Cross-Site Scripting (XSS) remains one of the most common and dangerous web application vulnerabilities. Despite years of awareness and improved security frameworks,...