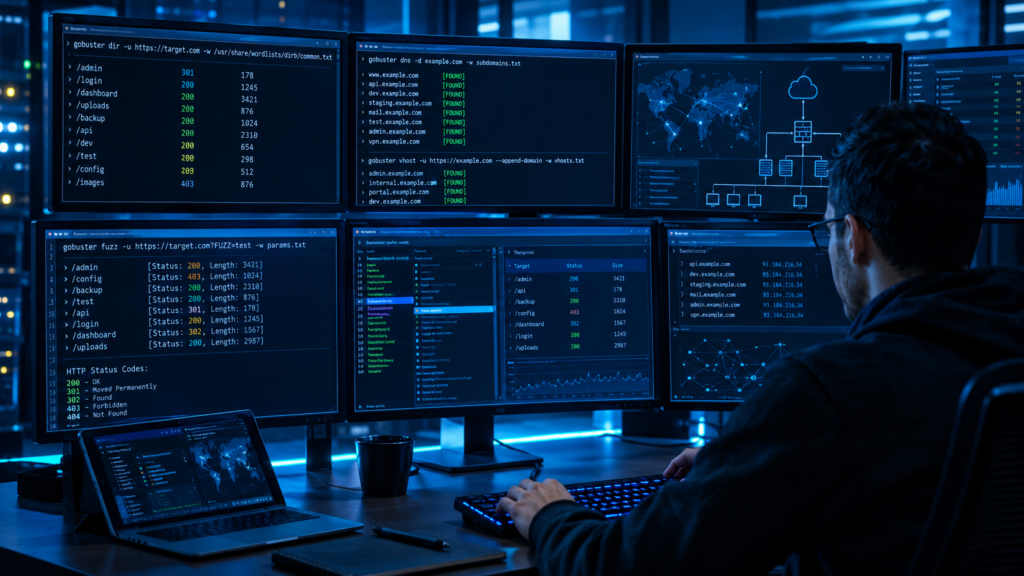
Gobuster is a popular command-line tool used by penetration testers and security researchers to discover hidden directories, files, DNS subdomains, virtual hosts, and other resources exposed by web infrastructure. Its speed and simple syntax make it especially useful during the reconnaissance and enumeration phases of a security assessment.
In a typical penetration test, knowing that a website exists is only the beginning. A tester needs to understand what applications, endpoints, directories, subdomains, and virtual hosts are available. This enumeration process can reveal forgotten administrative panels, development environments, backup files, API endpoints, and other parts of an application’s attack surface.
Gobuster is particularly useful because it supports multiple enumeration modes rather than focusing on a single task. The current project supports directory/file enumeration, DNS enumeration, virtual host discovery, cloud-storage-related modes, TFTP enumeration, and fuzzing.
This guide explains how Gobuster works, how to install it, the most useful commands, common mistakes, practical workflows, and how security professionals can use the tool responsibly.
Important: Only scan systems you own or systems for which you have explicit authorization to perform security testing. Enumeration can generate significant traffic and may trigger security controls.
What Is Gobuster?
Gobuster is an open-source brute-force and enumeration tool written in Go. It was designed for security professionals who need to quickly discover resources that are not immediately visible from a website’s main navigation.
Unlike a normal browser, Gobuster can take a large wordlist and systematically test potential resource names.
For example, suppose a website contains:
https://example.com/A normal visitor may only see the homepage.
A directory enumeration scan might test names such as:
/admin
/login
/dashboard
/uploads
/backup
/api
/dev
/test
If one of those resources exists, the web server may return an HTTP response indicating that the resource is available.
This makes Gobuster valuable during the information-gathering stage of a penetration test. OWASP also emphasizes application enumeration and attack-surface mapping as important parts of web application security testing.
Why Is Gobuster Important in Penetration Testing?
Modern web applications are rarely limited to a single public page.
A company might operate:
www.example.com
api.example.com
dev.example.com
admin.example.com
staging.example.com
The main website may expose very little information, while another application contains an outdated framework, forgotten test interface, or administrative endpoint.
Gobuster helps testers identify these resources efficiently.
Common discoveries include:
- Hidden directories
- Administrative panels
- Backup files
- Configuration files
- API endpoints
- Development environments
- Staging applications
- Subdomains
- Virtual hosts
- Cloud storage names
- Interesting file extensions
Enumeration does not automatically mean that a vulnerability exists. Instead, it expands the tester’s understanding of the attack surface so that subsequent testing can be more targeted.
Installing Gobuster
Gobuster is written in Go, and the official project currently recommends installing it with Go’s package installation mechanism. The project’s current README lists Go 1.24 or newer as a requirement for the current version.
On a Linux system with Go installed:
go install github.com/OJ/gobuster/v3@latestCheck whether the installation succeeded:
gobuster versionYou can also view the available commands with:
gobuster helpFor mode-specific help:
gobuster help diror:
gobuster dir --helpThe official Gobuster documentation provides installation instructions, Docker support, available modes, and command examples.
If you are building your skills from the ground up, combining command-line practice with “https://academy.pentesthint.com/” practical cyber security learning can help turn individual tools into a structured penetration-testing workflow.
Understanding Gobuster Modes
Gobuster uses a mode-based command structure.
The general syntax is:
gobuster [mode] [options]Some of the important modes include:
| Mode | Purpose |
|---|---|
dir | Directory and file enumeration |
dns | DNS subdomain enumeration |
vhost | Virtual host discovery |
fuzz | Basic fuzzing |
s3 | Amazon S3 bucket enumeration |
gcs | Google Cloud Storage enumeration |
tftp | TFTP file enumeration |
The official project documents these modes and their respective options.
For web penetration testing, the dir, dns, vhost, and fuzz modes are particularly useful.
Gobuster Directory Enumeration
The dir mode is probably the command most beginners associate with Gobuster.
Its basic syntax is:
gobuster dir -u https://example.com -w wordlist.txtHere:
dirselects directory enumeration mode.-uspecifies the target URL.-wspecifies the wordlist.
For example:
gobuster dir -u https://example.com -w /usr/share/wordlists/dirb/common.txtGobuster then requests paths based on the entries in the wordlist.
A simplified example might look like:
/admin
/login
/uploads
/api
/backup
The response can contain useful information such as HTTP status codes and response sizes.
Understanding HTTP Status Codes
During enumeration, status codes help determine what happened when Gobuster requested a resource.
Common responses include:
200 OK
The resource exists and returned successfully.
301 / 302
The resource may exist but redirects somewhere else.
403 Forbidden
The server knows about the resource but refuses access.
404 Not Found
The requested resource was not found.
A 403 response should not automatically be ignored. An inaccessible administrative directory may still be valuable information during a penetration test.
Enumerating File Extensions
Many applications use identifiable file extensions.
For example:
gobuster dir -u https://example.com -w wordlist.txt -x php,html,js,txtThis tells Gobuster to test the words with the specified extensions.
For a PHP application, this may help identify files such as:
login.php
config.php
upload.php
admin.php
However, extension selection should be based on information already gathered about the target. Blindly testing dozens of extensions can create unnecessary traffic.
Choosing a Good Wordlist
Gobuster’s results depend heavily on the quality of the wordlist.
A small wordlist is useful for a quick initial scan:
gobuster dir -u https://example.com -w common.txtA larger wordlist can provide broader coverage:
gobuster dir -u https://example.com -w directory-list.txtThe important point is not simply to use the largest wordlist available.
A professional assessment usually starts with a focused list and expands it based on the application’s technology, naming conventions, and information discovered during reconnaissance.
For example, if an application appears to use PHP, words related to PHP administration, uploads, authentication, and backups may be more useful than completely random entries.
Gobuster DNS Enumeration
The dns mode is used to discover subdomains.
Basic syntax:
gobuster dns -do example.com -w subdomains.txtFor example:
gobuster dns -do example.com -w /path/to/subdomains.txtThe tool attempts DNS resolution for candidate names from the wordlist.
A conceptual result might look like:
Found: api.example.com
Found: dev.example.com
Found: staging.example.com
Found: mail.example.com
This can significantly expand the scope of a web application assessment.
Why Subdomain Enumeration Matters
A company might have strong security controls on its primary website while an older development environment has weaker configuration.
For example:
www.example.commight be the production site.
But:
dev.example.comcould host a development application.
Similarly:
api.example.comcould expose APIs that require a completely different testing approach.
OWASP’s testing guidance highlights the importance of identifying applications and entry points across an environment rather than treating a single hostname as the entire attack surface.
Gobuster Virtual Host Enumeration
DNS enumeration and virtual host enumeration are related, but they are not the same thing.
A DNS lookup asks whether a hostname resolves through DNS.
A virtual host test examines how a web server responds when different hostnames are supplied.
Gobuster provides a vhost mode for this purpose.
A basic command is:
gobuster vhost -u https://example.com --append-domain -w wordlist.txtFor example, a tester may discover:
admin.example.com
internal.example.com
dev.example.com
portal.example.com
even when the application’s publicly documented DNS records do not reveal the complete environment.
This distinction is important in environments that host multiple applications behind the same IP address.
Gobuster Fuzzing Mode
Gobuster also includes a fuzz mode.
It replaces the FUZZ keyword with entries from the supplied wordlist.
For example:
gobuster fuzz -u https://example.com?FUZZ=test -w wordlist.txtA parameter-focused example could be:
gobuster fuzz -u "https://example.com?param=FUZZ" -w values.txtGobuster’s current documentation also supports fuzzing locations such as URLs, headers, and request bodies.
Fuzzing is particularly useful when the tester already has a specific hypothesis to investigate.
For example, after discovering:
https://example.com/search?query=testa tester may investigate how the application responds to different parameter values.
Gobuster should not be treated as a replacement for a dedicated web application proxy. Tools such as Burp Suite are often more appropriate when detailed request manipulation, session handling, and response analysis are required.
Useful Gobuster Options
Several options are worth learning early.
Specify File Extensions
-x php,html,js,txtUseful when you know or suspect which technologies the target uses.
Increase Threads
-t 50This increases concurrency.
Higher concurrency can make scans faster, but it also increases the request rate. On authorized assessments, adjust it according to the target’s capacity and rules of engagement.
Follow Redirects
-rRedirect behavior can be important when enumerating web applications.
Include Response Length
-lResponse length can help distinguish interesting results from repetitive responses.
Save Output
-o gobuster-results.txtSaving output makes it easier to review findings later and include evidence in a penetration-testing report.
A professional workflow should preserve useful enumeration results rather than relying on terminal history alone.
Real-World Gobuster Workflow
Consider a fictional penetration test against:
https://target.exampleThe tester begins with basic directory enumeration:
gobuster dir -u https://target.example -w common.txtThe scan identifies:
/admin
/api
/uploads
/login
The tester then investigates the API:
gobuster dir -u https://target.example/api/ -w api-endpoints.txt -x jsonThe DNS phase might follow:
gobuster dns -do target.example -w subdomains.txtSuppose it identifies:
dev.target.example
api.target.example
staging.target.example
Each newly discovered application becomes a separate part of the attack-surface map.
The tester can then use other tools for technology identification, HTTP analysis, authentication testing, vulnerability validation, and manual investigation.
This illustrates an important principle:
Gobuster is an enumeration tool, not the entire penetration test.
Its strongest value comes from combining its findings with careful manual analysis.
Handling False Positives
One of the most important Gobuster skills is learning to recognize false positives.
Some web servers return the same response for almost every unknown path.
For example:
/random-page-123
/random-page-456
/random-page-789
might all return HTTP 200.
A simple status-code filter would then produce many apparently valid results.
Response size can help identify this behavior.
For example:
gobuster dir -u https://target.example -w wordlist.txt -lIf nonexistent pages consistently return the same response length, that becomes a useful baseline.
The tester can then focus on results that behave differently.
This is one reason enumeration requires judgment rather than simply running a command and accepting every result.
Gobuster and API Security Testing
Modern applications increasingly depend on REST APIs and other backend services.
API endpoints can include:
/api/users
/api/login
/api/products
/api/admin
/api/v1
/api/v2
Gobuster can help discover predictable paths when a suitable wordlist is available.
For example:
gobuster dir -u https://api.target.example -w api-wordlist.txt -x jsonOnce endpoints are discovered, the tester should move beyond enumeration and examine:
- Authentication
- Authorization
- Input validation
- Rate limiting
- Error handling
- Sensitive data exposure
- HTTP methods
- Object-level access controls
OWASP recommends identifying application entry points and understanding how requests and parameters flow through an application before conducting deeper security testing.
Gobuster vs Other Enumeration Tools
Gobuster is not the only tool available for content discovery.
Other commonly used tools include:
- FFUF
- Feroxbuster
- Dirsearch
- Nmap
- DNSRecon
- Amass
Each has different strengths.
Gobuster is attractive when you want a fast, straightforward command-line workflow with several enumeration modes in one tool.
FFUF is widely used for flexible web fuzzing.
Nmap is more focused on network and service discovery.
Amass is commonly used for broader attack-surface and subdomain discovery.
A professional penetration tester should understand the problem being solved rather than becoming dependent on one tool.
Common Gobuster Mistakes
Using the Wrong Wordlist
A huge generic wordlist is not always better.
Choose wordlists based on the application and testing objective.
Ignoring 403 Responses
A forbidden resource can still reveal valuable information.
Do not assume that 403 means “nothing interesting here.”
Scanning Too Aggressively
Using excessive threads can overload applications or trigger rate limits.
Start conservatively and increase concurrency only when appropriate.
Ignoring Technology Fingerprinting
If you know an application is built with PHP, ASP.NET, Java, or another framework, tailor enumeration accordingly.
Treating Every Result as a Vulnerability
Finding /admin is not itself a vulnerability.
Finding /backup.zip is not automatically a vulnerability either.
The tester must validate what the resource exposes and determine its actual security impact.
Best Practices for Professional Gobuster Usage
A reliable enumeration process should follow a few principles.
Get Authorization First
Only test systems that are explicitly within your scope.
Start Small
Begin with a focused wordlist and basic scan.
Establish a Baseline
Understand how the server responds to nonexistent resources.
Customize the Wordlist
Use application-specific terminology whenever possible.
Control Request Rate
Avoid unnecessarily aggressive scanning.
Save Results
Keep command output as evidence for later analysis and reporting.
Validate Manually
Interesting findings should be verified manually.
Combine Tools
Use Gobuster as part of a broader methodology rather than relying on it alone.
For hands-on practice, a controlled environment such as “https://vuln.pentesthint.com/” cyber security labs is a safer way to experiment with enumeration techniques and understand how vulnerable applications behave.
Practical Gobuster Command Cheat Sheet
Here are several commands worth keeping as a quick reference.
Basic Directory Scan
gobuster dir -u https://target.example -w wordlist.txtDirectory Scan With Extensions
gobuster dir -u https://target.example -w wordlist.txt -x php,html,js,txtDirectory Scan With Response Length
gobuster dir -u https://target.example -w wordlist.txt -lDNS Enumeration
gobuster dns -do target.example -w subdomains.txtDNS Enumeration With More Threads
gobuster dns -do target.example -w subdomains.txt -t 50Virtual Host Enumeration
gobuster vhost -u https://target.example --append-domain -w wordlist.txtBasic Fuzzing
gobuster fuzz -u "https://target.example?FUZZ=test" -w wordlist.txtSave Results
gobuster dir -u https://target.example -w wordlist.txt -o results.txtAlways adapt commands to the target, scope, application behavior, and rules of engagement.
Learning Gobuster Through Practical Labs
Reading command syntax is useful, but enumeration becomes much easier to understand when you can see how a vulnerable application responds.
A controlled lab allows you to experiment with:
- Hidden directories
- Weakly protected panels
- API endpoints
- Virtual hosts
- Subdomains
- Authentication pages
- Backup files
- Misconfigured web servers
The “https://vuln.pentesthint.com/” hands-on labs provided by PentestHint can be used to build practical experience without scanning systems that you do not own or have permission to test.
You can also explore “https://academy.pentesthint.com/” cyber security training to build Gobuster knowledge alongside reconnaissance, web application testing, and vulnerability assessment skills.
Career Opportunities With Gobuster Skills
Gobuster is a relatively small part of a much larger penetration-testing skill set.
However, understanding enumeration is valuable for roles such as:
- Junior Penetration Tester
- Web Application Security Tester
- Vulnerability Assessment Analyst
- Bug Bounty Hunter
- Security Analyst
- Red Team Operator
Employers generally look for more than the ability to memorize commands.
A strong penetration tester should understand networking, HTTP, DNS, Linux, authentication, web technologies, APIs, vulnerability validation, reporting, and security methodology.
Gobuster becomes much more powerful when you understand what you are looking for and why a particular discovery matters.
Future of Web Enumeration
Web environments continue to become more distributed.
Organizations increasingly use:
- Cloud infrastructure
- Microservices
- APIs
- Containerized applications
- Multiple subdomains
- SaaS platforms
- CDN infrastructure
- Separate development and staging environments
This creates a larger and more dynamic attack surface.
Enumeration tools therefore remain important, but manual validation and attack-surface management are becoming equally important.
Security professionals need to understand not only how to discover an endpoint but also how that endpoint fits into the organization’s architecture.
FAQ
What is Gobuster used for?
Gobuster is used for security-focused enumeration, including web directories and files, DNS subdomains, virtual hosts, cloud storage resources, and fuzzing.
Is Gobuster legal to use?
Gobuster itself is a legitimate security-testing tool. However, using it against systems without authorization can violate laws, contracts, or acceptable-use policies. Use it only against systems you own or have explicit permission to test.
Is Gobuster available on Kali Linux?
Gobuster is commonly used in Linux-based penetration-testing environments. If it is not available in your environment, you can install the current version using the official Go installation method or use the project’s supported release options.
What is the difference between Gobuster dir and dns?
dir is designed to discover directories and files on a web server, while dns attempts to discover subdomains through DNS resolution.
What is the difference between Gobuster DNS and VHost?
DNS enumeration checks whether candidate hostnames resolve through DNS. VHost enumeration tests how the web server responds to different virtual host names. They can reveal different parts of an application’s infrastructure.
What wordlist should I use with Gobuster?
There is no single best wordlist. Start with a smaller, relevant wordlist and expand it based on the application’s technology and the objective of the assessment.
Can Gobuster find vulnerabilities?
Gobuster primarily discovers resources and attack-surface components. Finding a directory, file, or subdomain does not automatically mean that a vulnerability exists. The discovered resource must be manually investigated and validated.
Is Gobuster better than FFUF?
Neither tool is universally better. Gobuster provides multiple enumeration modes and a straightforward workflow, while FFUF is particularly flexible for fuzzing. Professional testers often choose based on the specific assessment requirement.
Conclusion
Gobuster is a practical enumeration tool that can help penetration testers uncover web directories, files, subdomains, virtual hosts, and other resources that may not be visible through normal browsing.
The most important lesson is that Gobuster should not be treated as a magic vulnerability scanner. Its real value comes from helping testers build a better picture of the target’s attack surface.
A strong workflow starts with authorization, performs controlled enumeration, analyzes HTTP and DNS behavior, validates interesting findings, and then moves into deeper security testing.
If you are building a career in penetration testing, practice Gobuster alongside networking, Linux, HTTP, DNS, API security, and manual web application testing. PentestHint can help you continue that journey through practical “https://academy.pentesthint.com/” online cyber security courses, “https://vuln.pentesthint.com/” vulnerability labs, and security-focused resources.
For organizations that need professional assessment support, “https://pentesthint.com/” VAPT services can provide a structured approach to identifying and validating security weaknesses across applications and infrastructure.
The goal is not to run the most aggressive scan. The goal is to understand the target, discover meaningful attack-surface components, validate them carefully, and turn technical findings into actionable security improvements.