How to Define Rules of Engagement for a Penetration Test
Penetration testing helps organizations identify security weaknesses before attackers can exploit them. However, even a well-planned security assessment can create operational problems...
Discovering an organization's internet-facing assets is one of the first steps in a professional security assessment. Before testing a website for vulnerabilities,...
Subdomain discovery is an important part of web application security testing. Before testing an application for vulnerabilities, a penetration tester needs to...
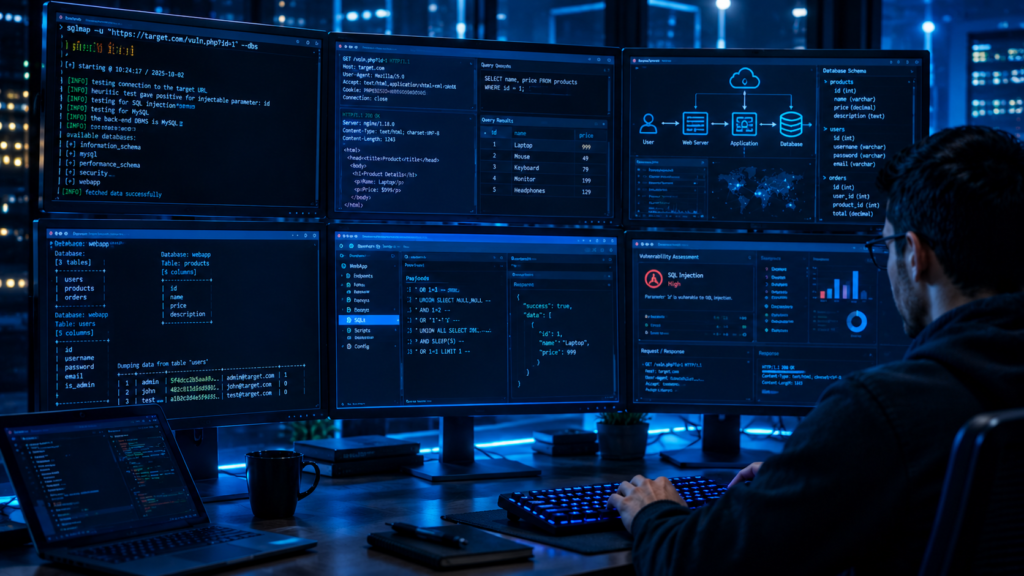
SQLMap Tutorial guides are useful for security professionals because SQL injection remains one of the most important web application vulnerabilities to understand....
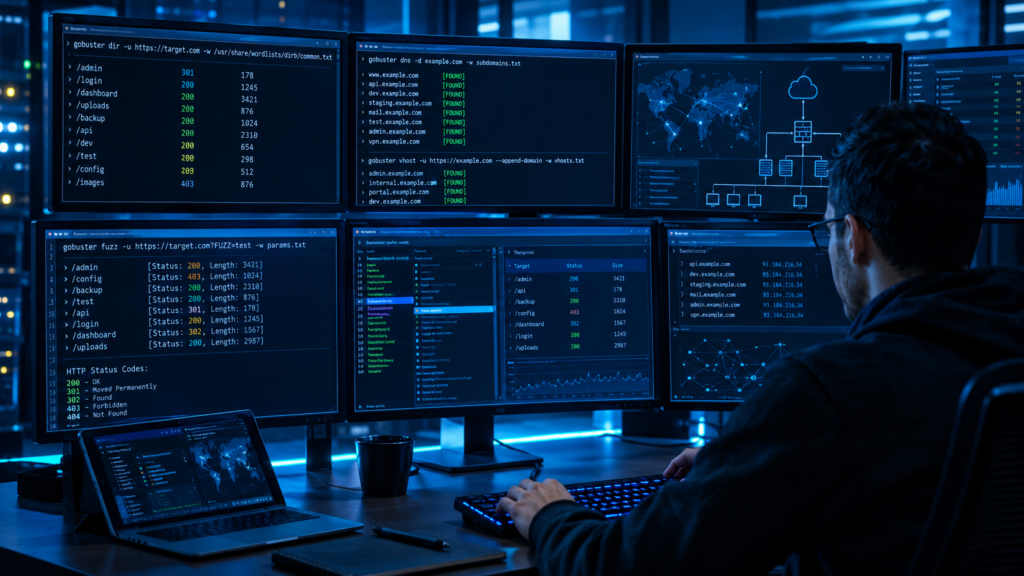
Gobuster is a popular command-line tool used by penetration testers and security researchers to discover hidden directories, files, DNS subdomains, virtual hosts,...
Finding a vulnerability is often less about exploiting a known endpoint and more about discovering the endpoint in the first place. Modern...
Wireshark is one of the most widely used tools for network traffic analysis and packet inspection. It allows security professionals, network administrators,...
The Metasploit Framework is one of the most widely used penetration testing platforms in cybersecurity. Security professionals use it to validate vulnerabilities,...
Burp Suite Complete Beginner Guide is designed for anyone who wants to understand how professional web application security testing works. Burp Suite...
Nmap, short for Network Mapper, is one of the most widely used tools for network discovery and security auditing. A beginner can...