

Cyber Security
XML External Entity (XXE) Attacks Explained: Risks & Prevention
XML External Entity (XXE) is a web application security vulnerability that occurs when an application processes untrusted XML using an insecurely configured...
XML External Entity (XXE) is a web application security vulnerability that occurs when an application processes untrusted XML using an insecurely configured...

Server-Side Request Forgery (SSRF) is a web application security vulnerability that allows an attacker to influence requests made by a server. Instead...
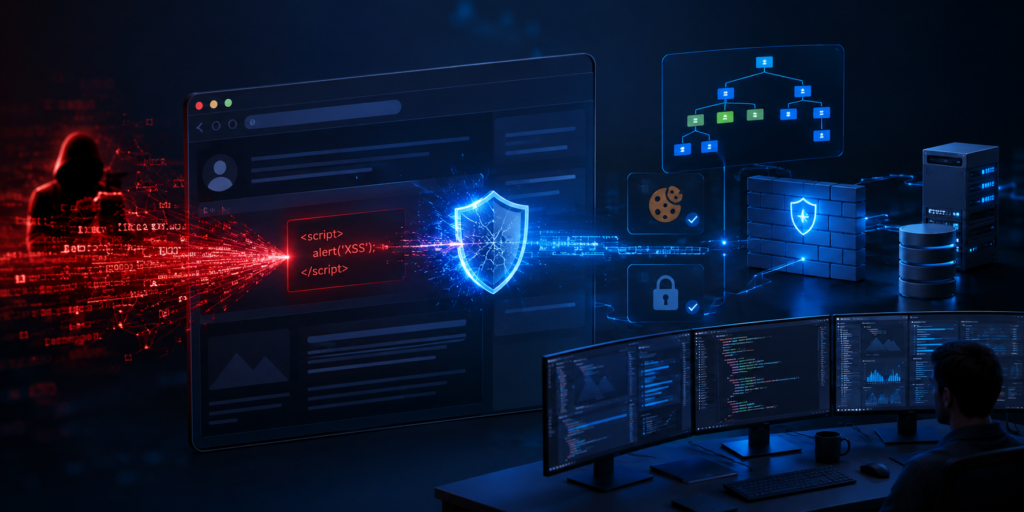
Cross-Site Scripting (XSS) is one of the most common web application security vulnerabilities. It occurs when an application allows untrusted data to...

SQL injection remains one of the most important web application security issues for developers, penetration testers, and security teams. SQL injection prevention...
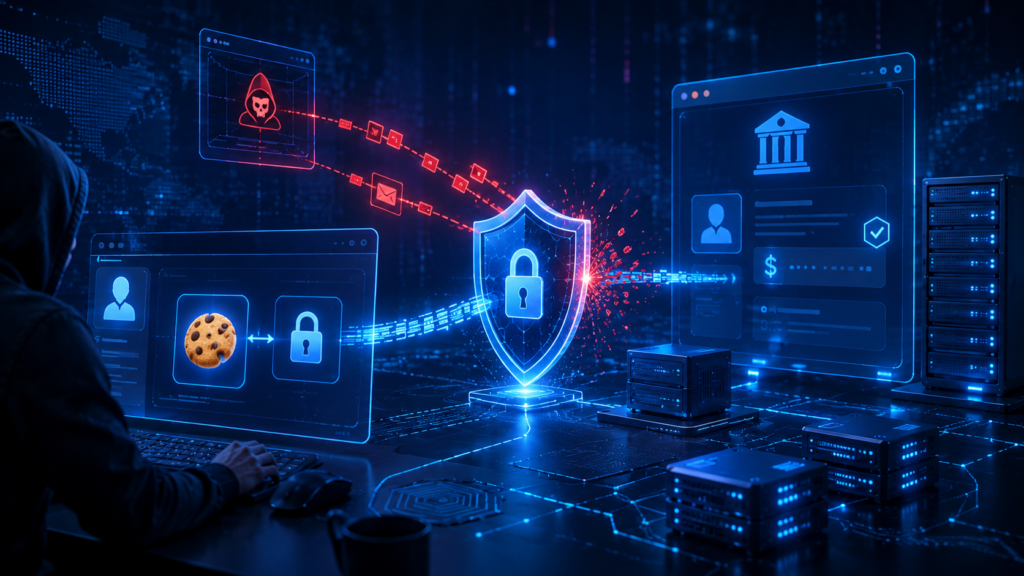
Web applications often rely on browser sessions and cookies to identify authenticated users. Once a user logs in, the browser automatically sends...

Modern web applications do much more than display information. They process payments, manage accounts, apply discounts, transfer money, approve orders, assign permissions,...

Uploading a file to a website looks simple. A user selects a document, image, PDF, or profile picture, and the application stores...
Modern web applications power everything from healthcare portals and digital banking to cloud management platforms. As applications grow more complex, they also...
Modern organizations continuously add new applications, APIs, cloud resources, servers, containers, and third-party services to their environments. Every new asset can introduce...

Modern cyber threats grow more complex every day. Security teams no longer rely on simple defense perimeters to stop dedicated threat actors....