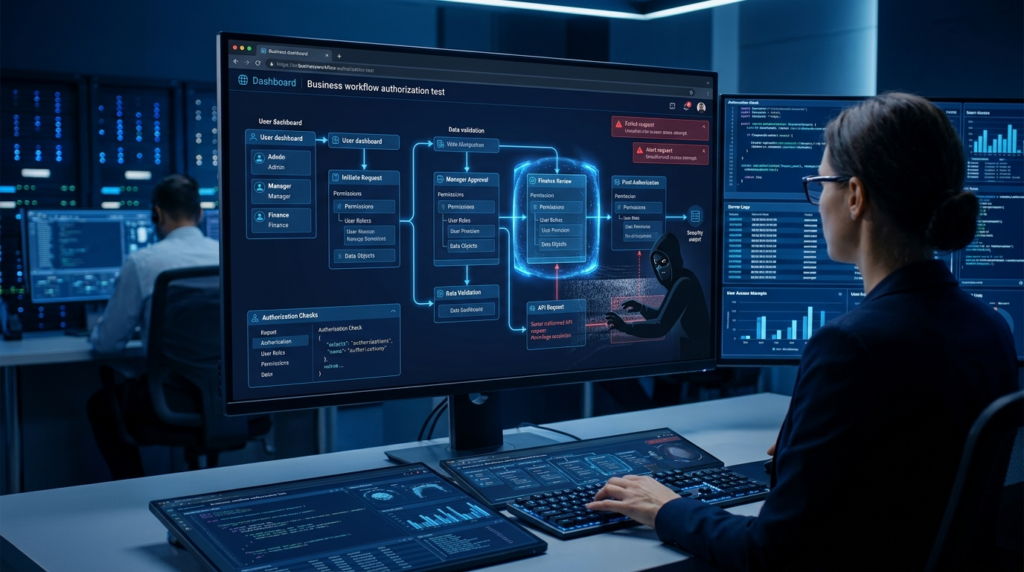
Modern web applications rarely perform important business operations through a single request. Actions such as transferring money, approving invoices, processing refunds, changing account ownership, publishing content, or completing customer onboarding usually involve several steps. Each step may require a different permission, approval, or verification.
Multi-Step Business Workflow Authorization Testing examines whether an application correctly enforces access controls throughout these processes. It helps penetration testers identify weaknesses that allow users to skip required steps, perform actions out of order, manipulate workflow states, or complete operations without the necessary permissions.
These issues are especially important in applications that rely on APIs, microservices, and distributed business processes. A workflow may appear secure in the frontend while individual backend endpoints fail to verify the user’s permissions or the current state of a transaction.
For example, an employee may be allowed to create a purchase request but not approve it. If the backend accepts an approval request from the same employee without checking their role, the application has an authorization weakness.
This guide explains how multi-step workflows operate, why authorization testing matters, common attack scenarios, practical testing techniques, and security controls that help prevent workflow abuse.
What Is Multi-Step Business Workflow Authorization Testing?
Multi-step business workflow authorization testing is a security assessment technique used to verify that an application enforces the correct permissions at every stage of a business process.
A workflow is a sequence of actions that moves a task or transaction from one state to another. Each stage may have different access requirements.
Consider an invoice approval process:
- An employee creates an invoice.
- A department manager reviews it.
- A finance officer approves the payment.
- The system processes the payment.
- The transaction is marked as completed.
Each stage should have clearly defined permissions. A user who can create an invoice should not automatically be able to approve or pay it.
The purpose of testing is to determine whether an attacker can manipulate requests, change workflow states, or use unauthorized endpoints to bypass these restrictions.
How Is It Different From Traditional Authorization Testing?
Traditional authorization testing often checks whether a user can access a particular page, API endpoint, or resource.
Workflow authorization testing goes further. It examines how permissions behave across a sequence of related actions.
For example, an application may correctly prevent a normal user from opening an administrator page. However, the same user might still be able to call an approval API directly or submit a transaction using an unexpected workflow state.
This means an application can pass basic access-control checks and still contain serious business logic vulnerabilities.
Why Multi-Step Workflow Authorization Testing Is Important
Business applications frequently handle financial transactions, customer information, employee records, and sensitive operational data. Unauthorized workflow transitions can lead to financial loss, data exposure, compliance problems, and operational disruption.
A workflow may contain several security checks, but a weakness in just one stage can undermine the entire process.
Important reasons to test these workflows include:
1. Prevent Unauthorized Approvals
An application should ensure that only authorized users can approve requests. Testers need to verify whether the backend checks the user’s role and permission before accepting an approval action.
2. Protect Financial Transactions
Payment processing, refunds, invoice approvals, and fund transfers often involve multiple verification stages. Weak authorization may allow users to bypass approval requirements or manipulate transaction states.
3. Prevent Privilege Escalation
A user may be authorized to perform one action but not another. If the application fails to distinguish these permissions, a lower-privileged user may gain access to sensitive functionality.
4. Protect Sensitive Business Data
Workflow APIs may expose information about customers, employees, suppliers, and internal operations. Proper authorization ensures that users can access only the records and actions permitted by their roles.
5. Maintain Business Process Integrity
Authorization is not only about accessing data. It also protects the order and validity of business operations.
For example, an order should not move to the shipping stage before payment has been confirmed.
Understanding Business Workflow States
Before testing a workflow, understand how the application represents its different stages.
Many applications use a state-based model. Each transaction has a current status, and specific actions move it to another status.
Example: Purchase Request Workflow
A purchase request might use the following states:
| Workflow state | Permitted action | Typical role |
|---|---|---|
| Draft | Create or edit request | Employee |
| Submitted | Submit for review | Employee |
| Under Review | Review request | Manager |
| Approved | Approve request | Authorized manager |
| Payment Pending | Initiate payment | Finance officer |
| Completed | Confirm completion | Finance system or authorized finance user |
The application should validate both the requested action and the current state.
For example, a payment should not be initiated while the request remains in the Draft state.
Role-Based Access Control in Workflows
Role-Based Access Control (RBAC) assigns permissions based on user roles.
A business application may define roles such as:
- Employee
- Department Manager
- Finance Officer
- Administrator
- Auditor
Each role should have a defined set of permitted actions.
However, role checks alone may not be sufficient. The application may also need to verify ownership, department, transaction status, approval limits, and separation-of-duty requirements.
For example, a manager may approve requests only for their own department. A finance officer may process approved invoices but should not be able to approve the same invoice independently.
Common Vulnerabilities in Multi-Step Business Workflows
Several authorization weaknesses can affect applications that rely on multi-stage processes.
1. Workflow Step Bypass
Workflow step bypass occurs when an application allows a user to skip a required stage.
Imagine an employee submitting a purchase request that requires manager approval. The frontend displays the approval stage only after submission.
A tester discovers that the backend accepts a direct request to the payment endpoint, even when the request has not been approved.
This indicates that the backend does not properly validate the workflow state.
Testing approach:
- Identify the normal sequence of workflow actions.
- Capture requests at each stage.
- Determine the required state before each action.
- Attempt to invoke later-stage actions using an earlier-stage transaction.
- Verify whether the backend rejects invalid transitions.
A secure application should not rely on the frontend to enforce the sequence.
2. Out-of-Order Workflow Execution
Some applications verify user permissions but fail to check whether an action is valid at the current stage.
For example, a user may have permission to submit a payment, but the invoice has not yet received the required approval.
The application should check both conditions:
- Does the user have permission to perform the action?
- Is the transaction in a state that permits the action?
If either condition fails, the operation should be rejected.
3. Unauthorized Approval
Unauthorized approval occurs when a user can approve a request without having the required role or authority.
Consider a workflow where employees create expense claims and managers approve them.
If the backend accepts an approval request from the employee who created the claim, the application may allow self-approval.
Testing approach:
- Create a test request using a low-privileged account.
- Capture the approval request from an authorized test account.
- Repeat the request using the creator’s session.
- Compare the responses.
- Verify whether the server checks the approver’s permissions and relationship to the request.
4. Parameter Tampering
Applications often send workflow details through API parameters or request bodies.
For example:
POST /api/requests/451/approve HTTP/1.1
Host: example.com
Authorization: Bearer <access_token>
Content-Type: application/json

{
  "status": "approved",
  "comment": "Approved"
}
A tester should determine whether the backend trusts user-controlled values such as status, approved_by, role, or approval_level.
Changing a parameter should not allow a user to grant themselves approval privileges or move a transaction into an unauthorized state.
The server should determine the valid next state based on trusted business rules, not blindly accept a status supplied by the client.
5. Insecure Direct Object References (IDOR)
IDOR occurs when an application fails to verify whether a user is authorized to access a specific object.
In a workflow, this could allow one employee to approve, edit, or view another employee’s request by changing an identifier.
For example:
GET /api/requests/451A tester may compare access to another request:
GET /api/requests/452If the second request belongs to another user and the application returns it without a proper authorization check, the endpoint may contain an IDOR vulnerability.
The same issue can affect approval, cancellation, deletion, and payment endpoints.
6. Race Conditions in Approval Processes
A race condition can occur when two or more requests interact with the same workflow state at nearly the same time.
For example, two managers may attempt to approve the same invoice simultaneously. If the application does not handle concurrent updates correctly, it may process duplicate approvals or payments.
Testing should examine whether the backend uses appropriate transaction handling, concurrency controls, and state validation.
7. Replay of Previous Workflow Requests
An attacker may capture a previously valid request and attempt to replay it.
For example, a payment confirmation request might be submitted more than once if the backend does not track whether the operation has already been completed.
Testers should check whether sensitive operations are protected against duplicate execution.
Applications can use transaction identifiers, idempotency keys, state checks, and appropriate replay protections to reduce this risk.
How to Perform Multi-Step Business Workflow Authorization Testing
A structured approach makes it easier to understand application behavior and identify authorization weaknesses.
Step 1: Identify Important Business Workflows
Start by exploring the application and listing processes that involve multiple stages.
Common examples include:
- Invoice creation and approval.
- Refund requests.
- Employee onboarding.
- Customer verification.
- Purchase orders.
- Loan applications.
- Account ownership changes.
- Content publishing.
- Payment processing.
- User access requests.
Focus first on workflows that involve money, sensitive data, privileged actions, or irreversible operations.
Step 2: Create a Workflow Diagram
Map each process from beginning to end.
Record the actions, roles, API endpoints, and expected states.
For example:
Create Request
      |
      v
Submit Request
      |
      v
Manager Review
      |
      v
Approval Decision
      |
      v
Finance Processing
      |
      v
Transaction Completed
A workflow diagram helps identify where authorization checks should occur.
It also makes it easier to recognize actions that should never be available before a specific stage.
Step 3: Identify User Roles and Permissions
Create test accounts with different levels of access.
For example:
| Test account | Expected permissions |
|---|---|
| Employee A | Create and view own requests |
| Employee B | Create and view own requests |
| Manager A | Review requests for assigned team |
| Finance User | Process approved payments |
| Administrator | Manage authorized application settings |
Document which actions each account should be allowed to perform.
Do not assume that two users with the same role have identical access to every resource. Department membership, ownership, and assigned responsibilities may affect authorization.
Step 4: Capture API Requests
Use an intercepting proxy such as Burp Suite to capture requests generated during each workflow stage.
Record:
- HTTP method.
- API endpoint.
- Authentication token or session context.
- Request parameters.
- Request body.
- Response status.
- Workflow state before and after the request.
This information helps identify which backend operations correspond to specific business actions.
Step 5: Test Each Workflow Transition
For every stage, verify whether the application allows only valid transitions.
For example:
| Current state | Requested action | Expected result |
|---|---|---|
| Draft | Submit | Allowed for creator |
| Draft | Approve | Rejected |
| Submitted | Approve | Allowed for authorized approver |
| Submitted | Process payment | Rejected |
| Approved | Process payment | Allowed for finance role |
| Completed | Process payment again | Rejected or safely handled |
The expected result depends on the application’s business requirements, but every transition should follow an explicit rule.
Step 6: Test with Different User Accounts
Repeat important requests using accounts with different privileges.
Check whether:
- A creator can approve their own request.
- One employee can modify another employee’s request.
- A manager can approve requests outside their assigned scope.
- A finance user can process unapproved transactions.
- A regular user can call administrator-only endpoints.
This process helps uncover both role-based and object-level authorization weaknesses.
Step 7: Test State Manipulation
Inspect request bodies and query parameters for fields that may influence workflow state.
Examples include:
{
  "status": "pending"
}
{
"approval_level": 2
}{
"approved_by": 1001
}Determine whether these values are genuinely intended to be user-controlled.
If changing them affects a sensitive operation, verify whether the backend independently validates the requested transition and the user’s authority.
Step 8: Test Duplicate and Concurrent Requests
For workflows involving payments, approvals, refunds, or other sensitive operations, check how the application handles repeated requests.
Within an authorized test environment:
- Submit the same action more than once.
- Replay a captured request after the transaction changes state.
- Test simultaneous requests where safe and permitted.
- Verify whether duplicate operations are prevented.
- Check whether the application records the final transaction state accurately.
Avoid tests that could trigger real payments, duplicate customer notifications, or irreversible production changes.
Step 9: Document and Validate Findings
For each confirmed issue, record the affected workflow, required privileges, vulnerable transition, and business impact.
A useful report should include:
- Vulnerability title.
- Affected endpoint and workflow stage.
- User role used during testing.
- Expected behavior.
- Actual behavior.
- Reproduction steps.
- Evidence from relevant requests and responses.
- Business impact.
- Recommended remediation.
Where possible, include a clear explanation of how the issue could affect the organization without accessing real customer information.
Practical Example: Bypassing an Invoice Approval Workflow
Consider a finance application that allows employees to create invoices and managers to approve them.
The intended process is:
- Employee creates an invoice.
- Employee submits it for approval.
- Manager reviews the invoice.
- Manager approves or rejects it.
- Finance processes approved invoices.
During testing, a penetration tester creates an invoice using an employee test account.
The tester captures the request used by a manager to approve an invoice:
POST /api/invoices/781/approve HTTP/1.1
Host: example.com
Authorization: Bearer <access_token>
Content-Type: application/json

{
  "comment": "Reviewed and approved"
}
The tester then repeats the request using the employee’s session.
If the backend accepts the request and changes the invoice status to Approved, the application has an authorization weakness.
The issue becomes more serious if the finance endpoint also accepts the invoice before checking the approval history.
Security impact:
- Employees may approve their own invoices.
- Unauthorized payments may be initiated.
- Financial approval controls may be bypassed.
- Audit records may become unreliable.
Recommended remediation:
The backend should verify the user’s approval permissions, confirm that the invoice is in the correct state, enforce separation of duties, and record the identity of the authenticated approver.
It should also reject duplicate or invalid transitions.
Tools Used for Business Workflow Authorization Testing
Several tools can help penetration testers inspect application requests and validate workflow behavior.
Burp Suite
Burp Suite is useful for intercepting and modifying HTTP requests.
Testers can use it to:
- Capture workflow API calls.
- Change object identifiers.
- Replay approval requests.
- Compare responses across user roles.
- Inspect authentication and session behavior.
- Test parameter manipulation.
OWASP ZAP
OWASP ZAP can help identify common web application vulnerabilities and inspect HTTP traffic.
It is useful during initial assessments, but complex workflow authorization issues often require manual testing.
Postman
Postman helps testers organize API requests and reproduce specific workflow actions.
It can be useful for creating collections that represent different stages of a business process and testing them with authorized accounts.
Browser Developer Tools
Browser developer tools help identify the requests generated by frontend actions.
The Network tab is particularly useful for mapping workflow operations, reviewing request payloads, and understanding how the frontend communicates with backend APIs.
OWASP Web Security Testing Guide
The OWASP Web Security Testing Guide provides guidance for assessing authentication, authorization, business logic, and other web application security areas.
For additional background, review the OWASP Broken Access Control guidance.
Best Practices to Prevent Workflow Authorization Vulnerabilities
Developers should enforce workflow rules on the backend and ensure that every state transition follows the application’s business requirements.
1. Enforce Authorization at Every Stage
Do not assume that permission to access the first stage grants permission to complete the entire process.
Check the user’s authorization whenever a sensitive action is requested.
2. Validate the Current Workflow State
The backend should confirm that the requested action is valid for the transaction’s current state.
For example, a payment should not be processed while the invoice is still awaiting approval.
3. Apply Server-Side State Management
Avoid trusting client-controlled status values.
The backend should determine the next valid state after checking the user’s permissions and the existing transaction state.
4. Implement Separation of Duties
For sensitive operations, require different users to perform different stages.
For example, the person who creates a financial request should not be able to approve it when organizational policy requires independent approval.
5. Verify Resource Ownership
Check whether the authenticated user has permission to access or modify the specific record.
A valid session alone should not provide access to every object in the application.
6. Protect Against Duplicate Requests
Use transaction controls and idempotency mechanisms where appropriate.
Sensitive operations should not execute multiple times simply because a request is replayed or submitted concurrently.
7. Maintain Audit Logs
Record important workflow actions, including:
- User identity.
- Action performed.
- Transaction identifier.
- Previous and new state.
- Timestamp.
- Approval or rejection details.
Audit records should be protected against unauthorized modification.
8. Test Business Logic During Development
Include authorization and workflow tests in the development lifecycle.
Test different roles, invalid transitions, object ownership, and duplicate requests before deploying major workflow changes.
Common Mistakes During Workflow Authorization Testing
Testers may overlook important weaknesses when they focus only on individual API endpoints.
Common mistakes include:
- Testing endpoints without understanding the complete business process.
- Checking user roles but ignoring transaction ownership.
- Assuming frontend restrictions enforce backend permissions.
- Testing only successful workflow paths.
- Ignoring invalid or unexpected state transitions.
- Failing to test with multiple accounts.
- Overlooking duplicate requests and race conditions.
- Treating an unusual response as a confirmed vulnerability without validating its impact.
- Performing tests against real financial or operational records without authorization.
A good assessment evaluates the complete workflow, not just isolated requests.
Career Opportunities in Business Logic and Authorization Testing
Business workflow authorization testing is a valuable skill for professionals working in web application security and penetration testing.
Relevant roles include:
- Web Application Penetration Tester.
- Junior Penetration Tester.
- API Security Tester.
- Application Security Analyst.
- Business Logic Security Tester.
- Security Consultant.
- Bug Bounty Researcher.
To develop these skills, learn HTTP fundamentals, REST APIs, authentication, RBAC, session management, business logic testing, and common access-control vulnerabilities.
Structured “https://academy.pentesthint.com/” cyber security training can help build the necessary foundation. You can also improve practical skills through authorized “https://vuln.pentesthint.com/” hands-on labs that provide opportunities to investigate vulnerable application behavior.
Professionals should also study the OWASP API Security Top 10 because workflow operations frequently depend on API authorization and object-level access controls.
Future Scope of Workflow Authorization Testing
Business applications are becoming more interconnected. Organizations increasingly use cloud platforms, microservices, workflow automation, payment gateways, and third-party integrations.
These changes create new authorization challenges.
Microservices and Distributed Workflows
A single business process may involve several backend services. Each service must validate the user’s permissions and the transaction’s current state rather than assuming that another service has already performed every necessary check.
API-Driven Business Processes
As more workflows are exposed through APIs, attackers may interact with operations directly rather than through the intended user interface.
This makes API discovery, object-level authorization, and state-transition testing important skills.
Automated Approvals
Automated systems can approve or reject requests based on business rules. Organizations must ensure that automation cannot be manipulated through unauthorized inputs, weak service permissions, or incorrect workflow conditions.
Stronger Audit and Compliance Requirements
Financial, healthcare, and enterprise applications often need reliable records of who performed each action and when.
Secure workflow design should include traceable approvals, appropriate access restrictions, and protected audit logs.
Security professionals who understand both technical access controls and business processes will be better equipped to assess these systems.
Conclusion
Multi-step business workflow authorization testing helps identify security weaknesses that traditional endpoint testing may miss. It examines whether users can perform only the actions permitted by their roles, whether transactions follow the correct sequence, and whether the backend validates every state transition.
Key testing areas include workflow step bypass, unauthorized approval, parameter tampering, IDOR, replay attacks, and race conditions.
The most important principle is that authorization must be enforced at every sensitive workflow transition. Applications should never trust frontend restrictions or client-controlled status values to protect important business operations.
For penetration testers, understanding the business process is just as important as understanding the API. A thorough assessment combines workflow mapping, role-based testing, request manipulation, and careful validation of business impact.
For more cybersecurity learning resources and professional security guidance, visit “https://pentesthint.com/” PentestHint.