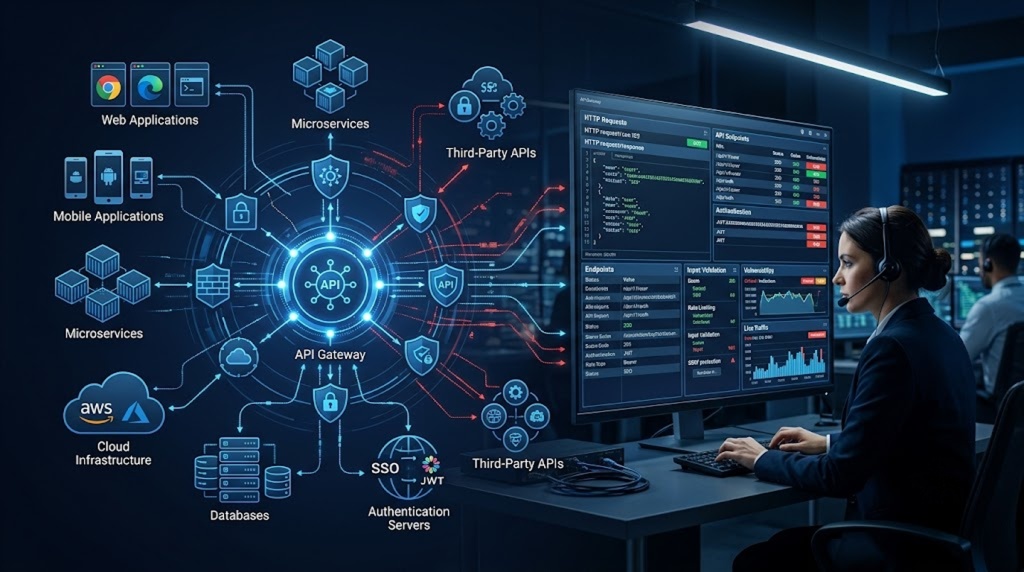
Modern applications depend heavily on APIs. Mobile applications, SaaS platforms, payment systems, cloud services, microservices, and third-party integrations may generate thousands or millions of API requests every day.
That makes API rate limiting an important part of both performance management and security.
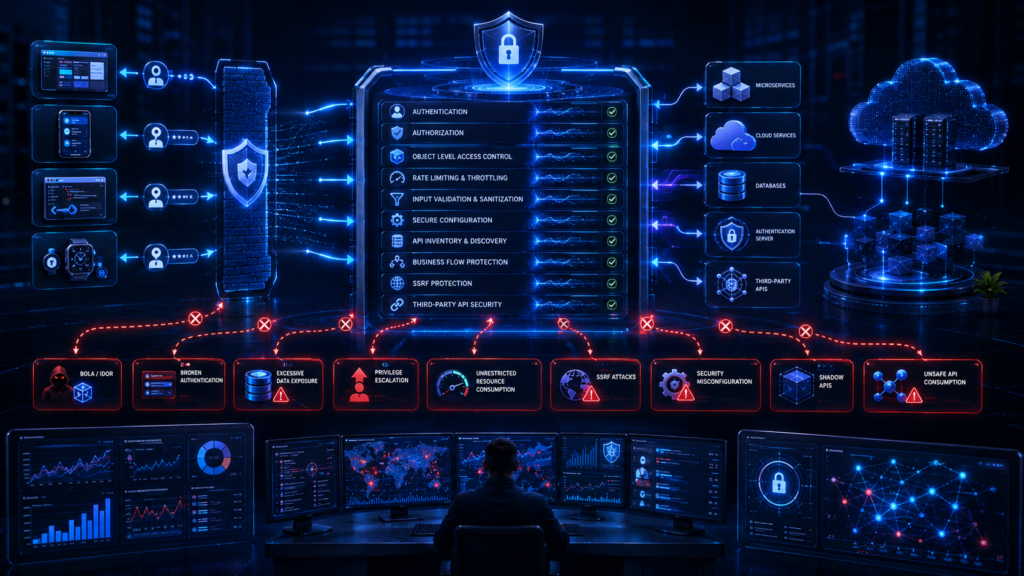
Without appropriate limits, an attacker can repeatedly call an endpoint to perform brute-force attacks, consume expensive backend resources, scrape data, abuse business functionality, or contribute to denial-of-service conditions. OWASP’s API Security guidance places unrestricted resource consumption among the major API security risks.
Rate limiting is not simply about blocking users after they send “too many requests.” A good implementation considers who is making the request, which endpoint they are accessing, how expensive the operation is, how much traffic the infrastructure can handle, and whether the behavior looks legitimate.
NIST’s current API protection guidance also treats rate limits as one of several runtime controls alongside quotas, concurrent connection limits, request-size limits, response limits, and role-based limits.
This guide explains how API rate limiting works, the algorithms behind it, common implementation mistakes, bypass techniques, and practical security best practices.
What Is API Rate Limiting?
API rate limiting is a mechanism that restricts how many requests a client can make to an API during a specific period.
For example, an API might enforce:
100 requests per minute per API keyIf a client exceeds the configured limit, the API can temporarily reject additional requests.
A typical response is:
HTTP/1.1 429 Too Many Requests
Content-Type: application/json
Retry-After: 30
The HTTP 429 Too Many Requests status code is specifically defined for situations where a client has sent too many requests within a given period. RFC 6585 also describes the optional Retry-After header, which can tell the client how long to wait before trying again.
A rate limiter can operate at several levels:
- IP address
- User account
- API key
- OAuth client
- Session
- Device
- Endpoint
- Tenant
- Geographic region
- Application role
The correct choice depends on the application and threat model.
Why Is API Rate Limiting Important?
Rate limiting protects more than just server bandwidth.
An API endpoint might trigger expensive operations such as database searches, file processing, password verification, report generation, or calls to another external service.
Imagine an endpoint like:
POST /api/generate-reportOne request might consume several seconds of CPU time and perform multiple database queries.
If an attacker sends thousands of requests, the backend can become overloaded even if each individual request is technically valid.
Protecting Against Resource Exhaustion
OWASP classifies unrestricted resource consumption as an API security problem because APIs may allow clients to consume excessive amounts of CPU, memory, bandwidth, storage, or other resources.
Rate limiting helps establish a boundary around that consumption.
Reducing Brute-Force Attacks
Consider:
POST /api/loginWithout appropriate controls, an attacker could continuously submit passwords.
A limit such as:
5 failed attempts / minute / accountcan significantly slow automated password guessing.
However, login protection should not rely on IP-based limiting alone because attackers can distribute requests across multiple addresses.
Controlling API Abuse
Legitimate users can also unintentionally overload an API.
For example, a badly designed mobile application might send the same request repeatedly because of a retry loop.
Rate limiting provides a safety mechanism before that behavior consumes excessive backend resources.
Protecting Third-Party Integrations
APIs frequently serve multiple customers or applications.
One customer consuming most of the available capacity can affect everyone else.
Per-client limits help maintain predictable service for different consumers.
How Does API Rate Limiting Work?
At a basic level, a rate limiter performs four steps:
Incoming Request
       ↓
Identify Client
       ↓
Check Current Usage
       ↓
Allow or Reject
       ↓
Update Counter
For example:
Client: API-Key-123
Limit: 100 requests/minute
Current usage: 98

New request → Allowed
Usage becomes: 99
The next request may still be allowed:
99 → 100But the following request may receive:
429 Too Many RequestsThe difficult part is deciding how requests should be counted.
That is where rate-limiting algorithms become important.
Common API Rate-Limiting Algorithms
Fixed Window
The fixed-window algorithm divides time into predefined intervals.
For example:
12:00:00 – 12:00:59
Maximum: 100 requests
At 12:01:00, the counter resets.
This approach is simple and inexpensive.
The Boundary Problem
Suppose an attacker sends:
100 requests at 12:00:59
100 requests at 12:01:00
The system may process 200 requests within approximately two seconds even though the configured limit is 100 per minute.
This is sometimes called a boundary burst.
Fixed windows are easy to implement but may provide weaker control around window boundaries.
Sliding Window
A sliding-window algorithm evaluates requests over a continuously moving period.
For example:
Maximum:
100 requests during the previous 60 seconds
Instead of resetting the counter at a specific clock boundary, the system continuously evaluates recent traffic.
This provides more consistent enforcement but can require more memory or processing depending on the implementation.
Token Bucket
The token bucket algorithm is widely useful when APIs need to support legitimate short bursts.
Imagine a bucket containing tokens:
Bucket capacity: 100
Refill rate: 10 tokens/second
Each API request consumes one token.
If the bucket contains tokens:
Request → Token available → AllowWhen the bucket becomes empty:
Request → No token → Rate limitedThe advantage is that the system can tolerate short bursts while still controlling sustained traffic.
Leaky Bucket
The leaky bucket model focuses on controlling the rate at which requests leave the queue.
Incoming requests may enter a queue, while processing occurs at a controlled rate.
This can help create a smoother traffic pattern.
It is useful when the goal is not only to restrict volume but also to regulate how requests reach backend systems.
Rate Limiting vs Throttling vs Quotas
These terms are related but not identical.
Rate Limiting
Controls how frequently requests can be made.
Example:
100 requests/minuteThrottling
Usually refers to slowing or restricting traffic when usage reaches a threshold.
The API might delay processing instead of immediately rejecting every request.
Quota
Controls total usage over a longer period.
For example:
1,000,000 API requests/monthNIST’s API protection guidance distinguishes rate limits from quotas, concurrent connection limits, request-size limits, response-size/time limits, and other controls.
A mature API may use all of them.
Where Should Rate Limiting Be Implemented?
There is no single location that works for every architecture.
API Gateway
An API gateway is often a good place for centralized rate limiting.
Internet
   ↓
API Gateway
   ↓
Rate Limiter
   ↓
Microservices
   ↓
Database
This allows multiple backend services to follow common policies.
Web Application Firewall
A WAF can help identify and block abusive traffic before it reaches application servers.
It can be especially useful for:
- Bot traffic
- Volumetric attacks
- Suspicious request patterns
- Known malicious sources
- HTTP abuse
Application Layer
Sensitive business operations may require rate limiting inside the application itself.
For example:
POST /api/password-reset
POST /api/send-otp
POST /api/payment
POST /api/login
These endpoints often need limits based on business logic rather than simple request counts.
Distributed Rate Limiting
Microservice environments create another challenge.
Imagine four API servers:
Client
  ↓
Load Balancer
  ├── Server A
  ├── Server B
  ├── Server C
  └── Server D
If each server maintains its own in-memory counter, an attacker may effectively receive four separate limits.
A centralized or distributed rate-limiting mechanism can provide consistent enforcement.
A recent NVD vulnerability illustrates why this matters: CVE-2025-57816 involved ineffective IP-based rate limiting in a deployment using CDNs, proxies, or load balancers, along with counters stored in memory rather than a shared store.
How Should an API Identify Clients?
Using only IP addresses is often insufficient.
Consider an office network:
100 employees
      ↓
One corporate NAT IP
      ↓
API
If the API limits that IP to 100 requests per minute, all 100 users may share the same limit.
The opposite problem occurs with attackers using distributed infrastructure.
A better strategy can combine several signals:
- API key
- Authenticated user
- OAuth client
- Tenant
- IP address
- Device identity
- Endpoint
- User role
- Request cost
For example:
Per IP:       500 requests/minute
Per API key:  1,000 requests/minute
Per user:     300 requests/minute
Sensitive API: 20 requests/minute
NIST also identifies role-based and IP/geographical limits as possible API protection controls.
Do Not Apply the Same Limit to Every Endpoint
One of the most common design mistakes is creating one global limit.
Consider these endpoints:
GET /api/profile
POST /api/login
POST /api/payment
POST /api/generate-report
GET /api/products
They do not have the same security or resource requirements.
A better design might look like:
| Endpoint | Example Limit |
|---|---|
| Product listing | 300/min |
| User profile | 120/min |
| Login | 10/min |
| OTP verification | 5/min |
| Password reset | 5/min |
| Payment | 20/min |
| Report generation | 10/min |
These values are only examples. Real limits should come from application capacity, expected user behavior, business requirements, and threat modeling.
Real-World Example: Login API
Suppose an application exposes:
POST /api/loginThe request contains:
{
  "username": "admin",
  "password": "..."
}
An attacker could automate thousands of requests.
A basic IP limit might be:
10 requests/minute/IPBut the attacker could distribute requests across multiple IP addresses.
A stronger design can combine:
Per IP
+
Per account
+
Per device/session
+
Progressive delay
+
Bot detection
For example:
Failed attempt 1 → normal response
Failed attempt 2 → normal response
Failed attempt 3 → short delay
Repeated failures → increasing delay
Excessive activity → temporary restriction
The goal is to make automated abuse expensive without locking legitimate users out unnecessarily.
Common API Rate-Limit Bypass Techniques
Rate limiting itself can become a penetration-testing target.
Changing the Client IP
Attackers may attempt to manipulate headers such as:
X-Forwarded-For
X-Real-IP
Forwarded
If the application blindly trusts client-supplied headers, the attacker may be able to appear to come from a different IP address.
The correct handling of proxy headers depends on the trusted network architecture.
Distributed Requests
An attacker can distribute requests across:
- Cloud servers
- Proxies
- Botnets
- Multiple accounts
- Multiple API keys
IP-based protection alone may therefore be insufficient.
Endpoint Variations
Poorly implemented limiters may treat:
/api/user
/api/user/
/api//user
as different resources.
Normalization should happen consistently before applying security policies.
HTTP Method Changes
A weak implementation might limit:
GET /api/accountbut fail to apply the same policy to an equivalent:
POST /api/accountwhen both routes expose the same underlying operation.
Parameter Manipulation
A single request may trigger expensive processing.
For example:
GET /api/products?limit=100000A request-count limit alone does not prevent this type of resource abuse.
This is why rate limiting should be combined with request-size, pagination, query complexity, and resource-cost controls.
API Rate Limiting Best Practices
1. Rate Limit Sensitive Endpoints
Pay special attention to:
- Authentication
- Password reset
- OTP
- Payment
- Search
- File uploads
- Report generation
- Export functionality
- Expensive database queries
2. Use Multiple Dimensions
Avoid relying exclusively on IP addresses.
Consider:
IP + user + API key + endpoint + tenantdepending on your architecture.
3. Use Different Limits for Different Operations
An inexpensive read operation should not necessarily have the same limit as a CPU-intensive report-generation endpoint.
4. Return HTTP 429
When requests exceed the configured limit, 429 Too Many Requests is the standard HTTP response for rate limiting. RFC 6585 also permits a Retry-After header to communicate when the client should retry.
Example:
HTTP/1.1 429 Too Many Requests
Retry-After: 30
5. Avoid Leaking Sensitive Information
Rate-limit responses should not reveal unnecessary internal information.
Avoid responses such as:
You have exceeded the Redis counter for node API-03.Keep implementation details private.
6. Centralize Counters in Distributed Systems
If several application instances enforce the same limit, they need a consistent view of usage.
A shared datastore or infrastructure-level rate limiter can help maintain that consistency.
7. Monitor Rate-Limit Events
Track:
- Number of 429 responses
- Top offending clients
- Endpoint-specific spikes
- Authentication failures
- API-key usage
- Geographic anomalies
- Sudden traffic increases
Monitoring can reveal attacks that individual requests would not expose.
8. Build Client-Friendly Limits
Legitimate clients need to understand what happened.
Where appropriate, provide:
Retry-Afterand documented usage limits.
NIST’s own public APIs demonstrate why rate limits matter operationally: NIST documents request limits for its APIs and recommends clients pace automated requests rather than continuously sending traffic.
API Rate Limiting for Expensive Operations
Request count is not always a good measurement of resource consumption.
Consider:
GET /api/search?q=adminversus:
GET /api/search?q=*The second request might cause substantially more database work.
Similarly:
GET /api/report?records=100may be cheap compared with:
GET /api/report?records=1,000,000For expensive operations, consider cost-based rate limiting.
For example:
Simple request = 1 point
Database-heavy query = 5 points
Large export = 20 points
Then limit clients by points rather than raw request count.
This approach is especially useful for GraphQL APIs, search platforms, analytics systems, and APIs that expose variable-cost operations.
API Rate Limiting and OWASP
OWASP’s API Security guidance identifies API4:2023 – Unrestricted Resource Consumption as a major API security risk.
The problem is broader than simply missing request counters.
An API can become vulnerable when clients can consume excessive:
- CPU
- Memory
- Network bandwidth
- Storage
- Database resources
- Third-party service capacity
OWASP’s API Security Testing Framework includes a test case for API4:2023 that specifically checks for missing rate limiting through burst-request testing.
This makes rate limiting an important area during API penetration testing.
For practical testing, “https://vuln.pentesthint.com/” hands-on labs can provide controlled environments for understanding rate-limit behavior and API abuse scenarios.
How to Test API Rate Limiting During a VAPT
A penetration tester should first identify endpoints where abuse could have a meaningful impact.
Look for:
/api/login
/api/register
/api/reset-password
/api/otp
/api/search
/api/export
/api/upload
/api/payment
/api/generate
Then determine whether limits exist.
A basic test might send a controlled burst of requests and observe:
Request 1 → 200
Request 2 → 200
...
Request 100 → 200
Request 101 → 429
Record:
- Limit threshold
- Time window
- Response code
Retry-After- Whether the limit is per IP
- Whether it is per user
- Whether it is per API key
- Whether different endpoints have different limits
- Whether limits persist across servers
Test for Bypass
With authorization, test whether the limit can be bypassed by changing:
- IP address
- API key
- User account
- Authentication state
- HTTP method
- Path normalization
- Host configuration
- Request parameters
The goal is not simply to prove that a 429 exists.
The real question is:
Can an attacker still consume excessive resources despite the rate-limiting policy?
Tools for API Rate-Limit Testing
Common tools used during authorized API security assessments include:
- Burp Suite
- OWASP ZAP
- curl
- Postman
- Python HTTP clients
- API gateway logs
- SIEM platforms
- Load-testing tools
Burp Suite is particularly useful for manually examining request behavior and identifying how the application responds as request volume increases.
For people building practical application-security skills, <a href=”https://academy.pentesthint.com/”>cyber security training</a> can help develop a stronger understanding of API testing, authentication, and vulnerability assessment.
Rate Limiting Is Not DDoS Protection by Itself
This distinction is important.
A rate limiter running inside an application may already consume CPU, memory, network connections, or other resources before it can reject the request.
RFC 6585 notes that even generating 429 responses under heavy attack can consume resources, and servers may use other mechanisms such as dropping connections when appropriate.
For large-scale attacks, organizations may need multiple defensive layers:
Internet
   ↓
CDN / DDoS Protection
   ↓
WAF
   ↓
API Gateway
   ↓
Rate Limiter
   ↓
Application
   ↓
Database
Each layer has a different purpose.
Rate limiting is one component of a broader API protection strategy.
API Rate Limiting Checklist
Before deploying an API, review the following:
- Sensitive endpoints have appropriate limits.
- Authentication endpoints have brute-force protection.
- Limits are not based exclusively on IP addresses.
- API keys or authenticated identities are considered.
- Different endpoints have appropriate thresholds.
- Expensive operations have stricter controls.
- Request size is limited.
- Pagination limits are enforced.
- Concurrent connections are controlled where appropriate.
- Distributed servers share rate-limit state when necessary.
429 Too Many Requestsis returned appropriately.Retry-Afteris used where useful.- Rate-limit events are monitored.
- Proxy and client-IP handling is configured correctly.
- Rate-limit bypass testing is included in VAPT.
- API gateway and WAF controls complement application-level limits.
- Limits are tested under realistic traffic.
- Legitimate clients are not unnecessarily blocked.
- Resource-cost limits supplement request-count limits.
FAQs
What is API rate limiting?
API rate limiting is a security and performance mechanism that restricts how many requests a client can make during a defined period. It helps protect APIs from abuse, excessive resource consumption, brute-force attacks, and accidental traffic spikes.
What HTTP status code is used for rate limiting?
The standard response is HTTP 429 Too Many Requests. RFC 6585 defines the status code for cases where a client sends too many requests within a given period. A server may also provide a Retry-After header.
What is the best API rate-limiting algorithm?
There is no universal best algorithm. Fixed windows are simple, sliding windows provide more consistent enforcement, and token buckets are useful when legitimate bursts need to be supported. The correct choice depends on traffic patterns and application requirements.
Should API rate limiting be based on IP address?
IP-based rate limiting can be useful, but it should rarely be the only control. Shared networks, proxies, mobile networks, NAT, and distributed attacks can make IP addresses an imperfect identifier.
Can API rate limiting prevent DDoS attacks?
Rate limiting can reduce certain forms of application-layer abuse, but it is not a complete DDoS solution. Large-scale attacks generally require additional controls such as CDN-based protection, WAFs, traffic filtering, and upstream DDoS mitigation.
How do penetration testers test API rate limiting?
Authorized testers typically identify sensitive and expensive endpoints, send controlled bursts of requests, observe response thresholds, and test whether limits can be bypassed through different identities, IP addresses, API keys, endpoints, or request patterns.
What is the difference between rate limiting and API quotas?
Rate limiting generally controls request frequency over a short period, such as 100 requests per minute. A quota usually controls total consumption over a longer period, such as one million requests per month.
Why is distributed rate limiting important?
In a load-balanced environment, multiple servers may process requests from the same client. If each server maintains an independent in-memory counter, an attacker may receive a higher effective limit. Shared or centralized state can provide more consistent enforcement.
Conclusion
API rate limiting is one of the most practical controls for protecting modern APIs.
A well-designed implementation does more than count requests. It considers identity, endpoint sensitivity, resource cost, traffic patterns, distributed infrastructure, and abuse behavior.
The strongest approach combines multiple controls: per-user or per-key limits, endpoint-specific policies, request-size restrictions, concurrency controls, authentication protection, monitoring, API gateways, and WAF or DDoS protection.
It is also important to remember that a 429 response does not automatically mean an API is secure. A penetration tester should investigate whether the limiter can be bypassed, whether expensive operations have separate controls, and whether distributed deployments enforce limits consistently.
NIST’s current API protection guidance reinforces this layered approach by treating rate limits alongside quotas, concurrent connection limits, request-size controls, response limits, and other runtime protections.
For organizations building or testing APIs, rate limiting should be treated as part of the overall security architecture rather than an optional performance feature.
For more practical application-security resources, explore PentestHint and its security learning resources and “https://vuln.pentesthint.com/” cyber security labs to practice API security concepts in controlled environments.