
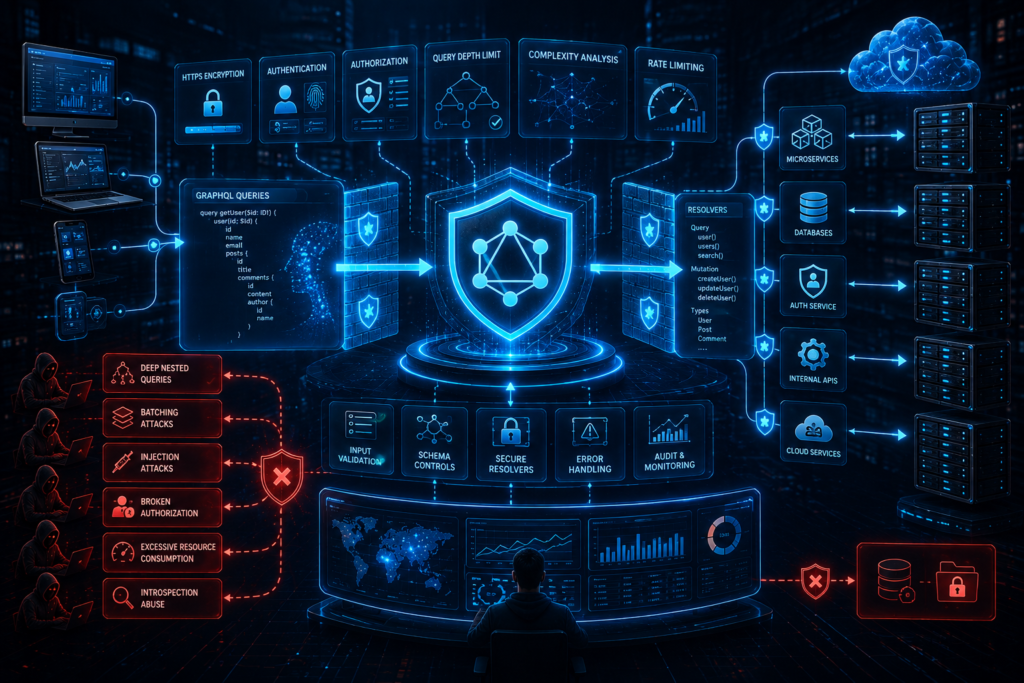
GraphQL has changed how modern applications communicate with backend services. Instead of exposing many fixed endpoints like a traditional REST API, GraphQL allows clients to request exactly the fields and relationships they need through a single API interface.
That flexibility is one of GraphQL’s biggest strengths, but it also introduces unique GraphQL security risks. A poorly configured GraphQL API can allow attackers to discover sensitive schema information, abuse deeply nested queries, bypass authorization controls, perform injection attacks, or consume excessive server resources.
GraphQL security requires more than simply adding authentication to the /graphql endpoint. Developers need to secure queries, mutations, resolvers, schema exposure, resource consumption, authorization, error handling, and the underlying services that GraphQL communicates with.
OWASP’s GraphQL Security Cheat Sheet specifically highlights risks including injection, denial of service, broken authorization, batching attacks, excessive errors, and insecure configurations.
This guide explains the most important GraphQL security risks and practical prevention techniques that developers, security engineers, and penetration testers can apply.
What Is GraphQL?
GraphQL is an API query language and runtime that allows clients to request specific data from a server.
A simple query might look like this:
query { user(id: "123") { name email }}
Instead of requesting multiple REST endpoints, the client can retrieve related information through one GraphQL operation.
For example:
query { user(id: "123") { name orders { id total products { name price } } }}
This flexibility makes GraphQL particularly useful for applications with complex data relationships.
However, the server now has to process queries whose structure and complexity can be controlled by the client.
That changes the security model.
A GraphQL server must determine not only whether the user is authenticated, but also:
- Which objects can they access?
- Which fields can they read?
- Which mutations can they execute?
- How complex can their query be?
- How much data can they request?
- How many operations can they send in one request?
- Which schema information should be exposed?
Why GraphQL Security Is Important
GraphQL often exposes a large application data model through a relatively small number of endpoints.
A typical deployment may have:
Client ↓GraphQL Endpoint ↓Resolvers ↓Business Logic ↓Databases / Microservices / External APIs
The GraphQL endpoint becomes an important gateway to multiple backend systems.
If authorization is implemented incorrectly at the resolver level, an attacker might access data that the frontend never displays.
Similarly, if query depth and complexity are not controlled, a single malicious request could force the server to execute an expensive chain of database queries.
OWASP recommends controlling query depth, query amount, pagination, timeouts, query cost, and request rates to reduce GraphQL denial-of-service risks.
For organizations building application security skills, <a href=”https://academy.pentesthint.com/”>cyber security training</a> can help developers and security professionals understand these risks through practical security concepts.
Major GraphQL Security Risks
1. Broken Authorization
One of the most serious GraphQL security problems is incorrect authorization.
Authentication answers:
Who is the user?
Authorization answers:
What is the user allowed to access?
A valid account should not automatically provide access to every object and field exposed through the GraphQL schema.
Consider:
query { user(id: "1001") { name email }}
An attacker might simply replace the ID:
query { user(id: "1002") { name email }}
If the server does not verify whether the authenticated user can access user 1002, the application may expose another user’s information.
This is closely related to IDOR and Broken Object Level Authorization.
How to Prevent It
Authorization should be enforced on the server.
Resolvers should verify:
Authenticated user ↓Requested object ↓Ownership / permission check ↓Requested field ↓Allow or deny
Do not rely on the frontend to hide unauthorized objects.
OWASP recommends authorization checks for both data access and mutations, including checking access at appropriate nodes and relationships within the GraphQL schema.
2. Excessive Data Exposure
GraphQL allows clients to request individual fields.
That is useful, but it can also become dangerous if sensitive fields are exposed in the schema.
For example:
query { user(id: "123") { name email phone passwordHash internalNotes isAdmin }}
The application may not display these fields in its normal interface, but if the schema exposes them and authorization is weak, attackers may request them directly.
Prevention
Use field-level authorization for sensitive information.
Separate public and privileged data where appropriate.
For example:
Public User ├── name ├── profileImage └── bioPrivate User ├── email ├── phone └── accountSettingsAdministrative User ├── internalNotes └── securityFlags
The API should return only fields the requesting identity is allowed to access.
3. GraphQL Injection Attacks
GraphQL itself does not automatically prevent backend injection.
Resolvers frequently pass user-controlled values to:
- SQL databases
- NoSQL databases
- Operating system commands
- External HTTP services
- LDAP services
- Search engines
- Template engines
For example:
query { searchUsers(query: "attacker-input") { name }}
If the resolver constructs an unsafe database query, the GraphQL layer does not magically make the backend safe.
Potential injection categories include:
- SQL injection
- NoSQL injection
- OS command injection
- LDAP injection
- SSRF
- Template injection
OWASP recommends strict input validation and safe APIs such as parameterized database queries when GraphQL input reaches other interpreters or backend systems.
Prevention
Use:
- Parameterized queries
- Safe ORM methods
- Allowlisted input
- Strong GraphQL scalar types
- Custom validation where required
- Proper output handling
- Safe libraries for downstream services
Never assume that GraphQL’s type system replaces application-level validation.
4. GraphQL Denial-of-Service Through Deep Queries
Deeply nested GraphQL queries are one of the most recognizable GraphQL-specific security concerns.
Consider:
query { user { posts { author { posts { author { posts { author { posts { title } } } } } } } }}
The query may look valid from a GraphQL perspective.
However, resolving every nested relationship could consume significant:
- CPU
- Memory
- Database connections
- Network bandwidth
- Application threads
- Downstream API calls
An attacker may intentionally construct expensive queries to degrade availability.
Prevention
Implement query depth limits.
For example:
Maximum query depth = 8
The exact value should depend on the application’s schema and legitimate use cases.
OWASP recommends depth limiting as one of the primary defenses against deeply nested GraphQL queries.
5. Query Complexity Attacks
Depth is not the only measure of an expensive query.
A shallow query could still request a huge amount of data.
For example:
query { users(first: 100000) { name }}
Even though the query may not be deeply nested, processing 100,000 records can put significant pressure on the backend.
This is why security teams should consider query complexity analysis in addition to depth limits.
Prevention
Assign costs to fields or operations.
For example:
user = 1posts = 5comments = 10search = 20
A query exceeding the maximum allowed cost can be rejected before execution.
OWASP describes query cost analysis as a way to assign resource costs to fields or types and reject queries that exceed an acceptable threshold.
6. Missing Pagination
GraphQL APIs can return large collections.
A query such as:
query { users { id name }}
could become expensive if the application contains millions of users.
Pagination limits how much data can be returned at once.
For example:
query { users(first: 50) { edges { node { id name } } }}
The server should enforce a maximum regardless of what the client requests.
For example, if the client attempts:
first: 1000000
the server should reject it or cap the value.
Pagination is also useful for protecting database and downstream service resources.
7. GraphQL Batching Attacks
GraphQL supports batching, which allows multiple operations or object requests to be processed through a single network request.
This can be useful for performance.
It can also create a security problem.
Imagine an authentication-related operation where an attacker submits many attempts inside a single batched request.
A traditional rate limiter might see:
1 HTTP request
while the GraphQL server actually processes:
1000 operations
This can weaken network-level rate limiting.
OWASP identifies batching attacks as a GraphQL-specific brute-force and resource-abuse technique.
Prevention
Consider:
- Limiting operations per request
- Applying rate limits inside the GraphQL layer
- Limiting object requests
- Restricting batching for sensitive operations
- Monitoring repeated object enumeration
- Applying stricter controls to authentication and OTP operations
Network-level rate limiting alone may not be enough.
8. Introspection Abuse
GraphQL has an introspection feature that allows clients to discover information about the schema.
For legitimate developers, this is extremely useful.
For attackers, an exposed schema can provide valuable reconnaissance information.
An attacker may learn:
QueriesMutationsTypesFieldsArgumentsDeprecated fieldsRelationships
If a production API exposes unrestricted introspection, it may make schema discovery easier.
OWASP recommends disabling or restricting introspection according to the application’s requirements, particularly for internal or sensitive production APIs.
Should Introspection Always Be Disabled?
Not necessarily.
A public GraphQL API may intentionally provide schema discovery to developers.
The security decision should depend on the API’s purpose.
For private APIs, consider:
Development → Introspection enabledTesting → Controlled accessProduction → Restricted or disabled
Disabling introspection is not a replacement for authorization. Attackers may still discover fields through other means.
9. GraphiQL and Development Tools Exposed in Production
GraphiQL and similar GraphQL exploration tools are useful during development.
Leaving them publicly accessible in production can provide attackers with an interactive interface for exploring the API.
A production environment should not expose development functionality unnecessarily.
Prevention
Disable GraphiQL and similar tools in production or restrict them to authorized users and trusted environments.
OWASP specifically recommends disabling GraphiQL and other schema exploration interfaces in production or publicly accessible environments when they are not required.
10. Excessive Error Messages
Detailed errors can reveal valuable information about the application’s internal architecture.
For example:
Database connection failed:postgresql://internal-db-01:5432/customerdb
or:
TypeError: Cannot read property 'id' of undefinedat UserResolver.js:142
Such information can help attackers understand:
- Database technology
- Internal hostnames
- File paths
- Frameworks
- Resolver names
- Application logic
Prevention
Return controlled errors to clients.
Log detailed diagnostic information internally.
Do not expose stack traces or debug information through production GraphQL responses.
OWASP recommends avoiding excessive errors and disabling debug-style output in production.
11. Missing Rate Limiting
GraphQL applications need rate limiting just like REST APIs.
However, counting HTTP requests alone may not provide enough protection because one GraphQL request can represent a large amount of work.
Consider rate limiting based on:
- IP address
- User identity
- API key
- Query complexity
- Query depth
- Operation count
- Resource consumption
- Sensitive object access
For authentication and other high-value operations, use stricter limits.
OWASP recommends rate limiting GraphQL requests and notes that controls can be applied through infrastructure such as WAFs and API gateways as well as application-level mechanisms.
12. SSRF Through GraphQL Resolvers
GraphQL resolvers sometimes fetch external resources.
For example:
query { fetchPreview(url: "https://example.com")}
If the backend makes an HTTP request to a user-controlled URL without proper validation, the resolver could become an SSRF vulnerability.
An attacker may attempt to make the server access internal resources.
Prevention
Avoid making server-side requests to arbitrary user-controlled destinations.
When external requests are necessary:
- Allowlist destinations
- Validate URLs
- Restrict protocols
- Block internal address ranges where appropriate
- Restrict redirects
- Use network egress controls
- Apply request timeouts
OWASP specifically warns against allowing user input to directly control HTTP or resource destinations without a strong business requirement and appropriate controls.
13. Mutation Authorization Problems
GraphQL mutations can modify application data.
For example:
mutation { updateUser( id: "123", role: "admin" ) { id role }}
Even if a user is authenticated, they should not automatically be allowed to modify privileged fields.
The application should verify:
Who is requesting the mutation? ↓Which object are they modifying? ↓Which fields can they modify? ↓Is this operation permitted? ↓Execute mutation
This is particularly important for:
- Account roles
- Passwords
- Email addresses
- Payment details
- Permissions
- Organization membership
- Security settings
Authorization should be enforced on the server, not merely through UI controls.
GraphQL Security Best Practices
Use HTTPS
Protect GraphQL traffic with properly configured TLS.
Sensitive authentication credentials, tokens, and application data should not travel over unencrypted connections. OWASP recommends properly configured TLS for sensitive web service communications.
Implement Strong Authentication
Use an established authentication mechanism appropriate to the application.
Authentication should establish the identity of the caller, while authorization determines what that identity can access.
Enforce Authorization at Resolver Level
Every sensitive query and mutation should perform appropriate authorization checks.
Do not assume that authenticating the /graphql endpoint automatically protects every object exposed through the schema.
Validate Input
Use GraphQL’s type system together with application-level validation.
Custom scalars and enums can help constrain expected values.
Limit Query Depth
Prevent excessively nested queries from consuming server resources.
Analyze Query Complexity
Consider assigning costs to expensive fields and rejecting queries that exceed acceptable limits.
Implement Pagination
Limit collection sizes and enforce server-side maximum values.
Control Batching
Limit operations and object requests within individual GraphQL requests.
Restrict Introspection
Disable or restrict introspection when the API’s security model requires it.
Disable GraphiQL in Production
Do not expose development tooling unnecessarily.
Use Rate Limiting
Combine network-level and application-level controls where necessary.
Protect Against Injection
Use parameterized queries and safe APIs for database and downstream operations.
Control Error Messages
Return useful but non-sensitive errors to clients.
Monitor GraphQL Activity
Log security-relevant events such as:
- Authentication failures
- Authorization failures
- Expensive queries
- Excessive query depth
- Repeated object enumeration
- Suspicious batching
- High request rates
- Mutation failures
For practical application security experience, <a href=”https://vuln.pentesthint.com/”>cyber security labs</a> can be useful for practicing API and web security testing in controlled environments.
GraphQL Security Testing Checklist
Security testing should cover both the GraphQL layer and the underlying application.
A practical assessment can include:
Schema Discovery
Check whether introspection is enabled and determine what information is exposed.
Authentication Testing
Test:
- Missing authentication
- Invalid tokens
- Expired tokens
- Session handling
- Authentication bypass scenarios
Authorization Testing
Test access to:
- Other users’ objects
- Administrative fields
- Restricted mutations
- Sensitive fields
- Internal resources
Query Abuse Testing
Test:
- Deep nesting
- Large collection requests
- Expensive relationships
- Excessive aliases
- Multiple operations
- Batching
- Repeated queries
Input Testing
Check GraphQL arguments for:
- SQL injection
- NoSQL injection
- Command injection
- SSRF
- Unexpected data types
- Oversized input
Configuration Testing
Review:
- Introspection
- GraphiQL
- Debug mode
- Error messages
- CORS
- TLS
- Rate limiting
- Logging
Authorized testers can use tools such as Burp Suite, GraphQL-specific scanners, browser developer tools, and custom scripts to assess GraphQL behavior.
The OWASP GraphQL guidance also lists security-oriented tooling and recommends considering both query behavior and configuration during assessments.
GraphQL Security vs REST API Security
GraphQL and REST share many fundamental security requirements.
Both need:
- HTTPS
- Authentication
- Authorization
- Input validation
- Rate limiting
- Secure error handling
- Logging
- Monitoring
- Secure dependency management
The difference is in how requests are structured.
REST usually exposes multiple endpoints:
GET /users/123GET /users/123/ordersGET /orders/456
GraphQL commonly exposes a single endpoint:
POST /graphql
but allows the client to control the structure of the requested data.
That flexibility creates additional concerns around:
- Query depth
- Query complexity
- Batching
- Schema exposure
- Resolver authorization
- Field-level access control
GraphQL security therefore requires thinking about both the request and the work that request causes the backend to perform.
GraphQL Security Checklist for Developers
Before deploying a GraphQL API, review this checklist:
- HTTPS enforced
- Strong authentication implemented
- Resolver-level authorization implemented
- Object ownership verified
- Sensitive fields protected
- Mutations properly authorized
- Input validation enabled
- Parameterized database queries used
- Query depth limits configured
- Query complexity limits considered
- Pagination enforced
- Query batching controlled
- Rate limiting implemented
- Introspection reviewed
- GraphiQL restricted or disabled in production
- Debug mode disabled
- Stack traces hidden from clients
- SSRF protections implemented
- API activity monitored
- Sensitive events logged
- Dependencies regularly updated
- Security testing performed
- Unnecessary schema fields removed
Common GraphQL Security Mistakes
Treating GraphQL as Secure by Default
GraphQL provides a query language and execution model. It does not automatically implement your application’s authorization policy.
Relying Only on Introspection Controls
Disabling introspection may reduce information disclosure, but it does not fix broken authorization or insecure resolvers.
Using Only IP-Based Rate Limiting
One GraphQL request can contain substantial work. Application-level controls may be necessary.
Forgetting Field-Level Authorization
Protecting an object while leaving sensitive fields unrestricted can still result in data exposure.
Allowing Unlimited Query Depth
Deep queries can consume significant backend resources.
Exposing Debug Tools
GraphiQL and detailed errors should not be unnecessarily available to unauthenticated production users.
Trusting Resolver Input
GraphQL input still reaches databases, APIs, and other interpreters. The downstream component must be protected.
Ignoring Business Logic
A technically valid GraphQL query can still perform an unauthorized business operation.
Future of GraphQL Security
GraphQL will continue to be useful for applications that need flexible access to complex data.
As schemas become larger and applications depend on more microservices, the security challenge will increasingly move beyond the GraphQL endpoint itself.
Security teams will need visibility into:
GraphQL Client ↓Authentication ↓GraphQL Gateway ↓Authorization ↓Resolvers ↓Business Logic ↓Databases / APIs / Services
Security controls should therefore be applied throughout the request lifecycle.
Query complexity analysis, resolver-level authorization, API monitoring, automated testing, schema governance, and strong identity controls will become increasingly important for larger GraphQL deployments.
The objective is not to eliminate GraphQL’s flexibility.
The objective is to make sure that flexibility cannot be abused to access unauthorized information or consume unreasonable amounts of infrastructure.
Frequently Asked Questions
What are the main GraphQL security risks?
The major risks include broken authorization, injection attacks, denial of service through expensive queries, batching attacks, excessive data exposure, SSRF, introspection abuse, insecure configuration, and excessive error disclosure.
Is GraphQL more secure than REST?
Neither GraphQL nor REST is automatically more secure. Security depends on implementation. GraphQL introduces additional concerns such as query depth, complexity, batching, schema exposure, and resolver-level authorization.
Should GraphQL introspection be disabled?
It depends on the API. Internal or sensitive production APIs may benefit from disabling or restricting introspection. Public developer-facing APIs may intentionally require it. Introspection controls should not replace proper authorization.
How can I prevent GraphQL DoS attacks?
Use query depth limits, query complexity analysis, pagination, rate limiting, timeouts, resource limits, and controls on batching. The appropriate combination depends on the schema and workload.
What is a GraphQL batching attack?
A batching attack abuses GraphQL’s ability to process multiple operations or object requests within one network request. Attackers can use this behavior for enumeration, brute-force attempts, or resource exhaustion.
Can GraphQL be vulnerable to SQL injection?
Yes. GraphQL does not automatically prevent SQL injection. If resolver input is incorporated into unsafe database queries, the underlying application can still be vulnerable. Parameterized queries and safe database APIs should be used.
Does authentication protect a GraphQL API?
Authentication only identifies the requester. The API still needs authorization controls to determine which objects, fields, and mutations that requester can access.
Is disabling GraphiQL enough to secure GraphQL?
No. Disabling GraphiQL removes one interface for exploring the API, but it does not fix authorization, injection, DoS, batching, or other GraphQL security problems.
Conclusion
GraphQL provides developers with a flexible way to build APIs, but that flexibility needs strong security controls.
The most important GraphQL security risks are not limited to authentication. Developers need to think about authorization, field-level access, query depth, query complexity, batching, input validation, injection, resource consumption, introspection, SSRF, and error handling.
A secure implementation should verify authorization for every sensitive object and mutation, limit expensive queries, control batching, validate input, protect downstream services, and monitor suspicious behavior.
Security testing should also go beyond checking whether /graphql requires authentication. A proper assessment should examine the schema, resolvers, authorization model, query behavior, business logic, resource consumption, and production configuration.
Following established guidance such as the OWASP GraphQL Security Cheat Sheet provides a strong foundation for securing GraphQL applications.
For organizations that need “https://pentesthint.com/” VAPT services, application security testing, and practical cybersecurity resources, PentestHint can help teams build a stronger approach to API security.
GraphQL is powerful because clients can ask for exactly what they need. The security challenge is making sure they can only ask for what they are authorized to access—and cannot turn that flexibility into an attack path.



