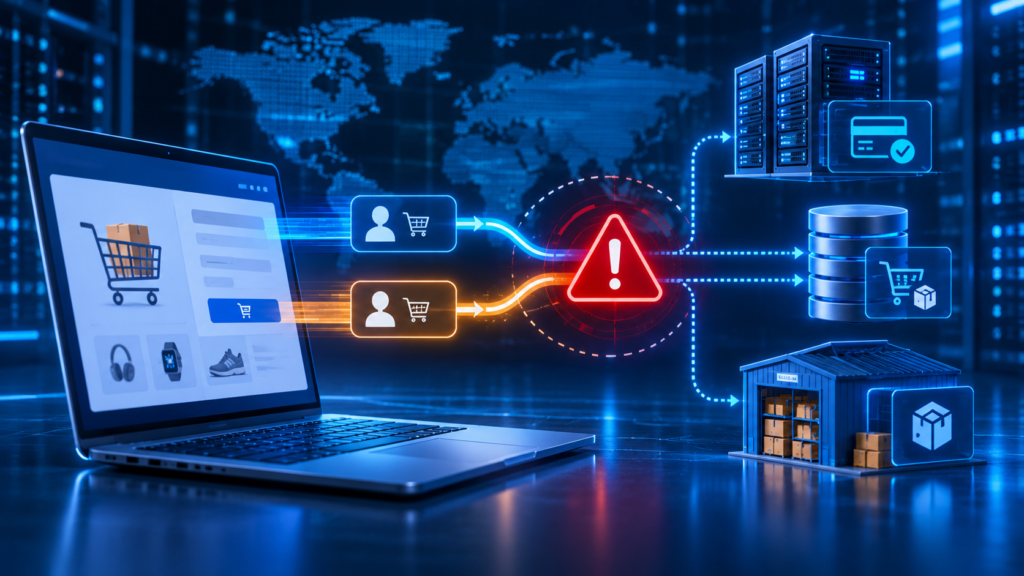
Online shopping and digital payment systems process thousands of transactions every minute. Customers expect checkout operations to be fast, reliable, and secure. Behind every successful purchase, however, several application components work together to validate orders, calculate prices, apply discounts, check inventory, process payments, and update transaction records.
When two or more requests access and modify the same data at nearly the same time, the application may produce an unexpected result. This is where race condition vulnerabilities become a serious security concern. A flaw in transaction synchronization can allow an operation that should happen only once to execute multiple times.
Consider an online store that offers a one-time discount coupon. A customer submits the coupon request twice almost simultaneously. If the application checks whether the coupon has already been used before recording its usage, both requests might pass the check. The customer could receive the same discount more than once.
Similar problems can affect payment confirmations, account balances, product inventory, gift cards, loyalty points, and limited-availability bookings.
As e-commerce platforms increasingly depend on APIs, distributed services, and asynchronous payment processing, controlling concurrent operations has become an important part of application security. Developers and penetration testers must understand how these workflows behave under simultaneous requests rather than testing only the normal checkout process.
What Are Race Condition Vulnerabilities?
A race condition occurs when the result of an operation depends on the timing or order of multiple concurrent processes.
In a web application, this often happens when multiple HTTP requests access the same resource without sufficient synchronization. If the application does not protect a critical operation, two requests may read the same initial value and then make conflicting updates.
MITRE classifies this weakness as CWE-362: Concurrent Execution using Shared Resource with Improper Synchronization.
In checkout and transaction workflows, shared resources commonly include:
- Customer account balances
- Product inventory counts
- Shopping cart records
- Discount and coupon usage records
- Payment transaction statuses
- Gift card balances
- Order confirmation records
- Loyalty points and reward balances
A race condition does not always require a complex attack. Sometimes, sending two requests close together is enough to expose a weakness in the application’s business logic.
A Simple Example
Imagine an online store has one remaining unit of a product.
The application checks inventory before confirming an order:
- Customer A requests the product.
- Customer B requests the same product almost simultaneously.
- Both requests read the inventory value as
1. - Both requests pass the availability check.
- Both requests attempt to complete the purchase.
If the inventory check and update are not handled atomically, the application may confirm two orders even though only one item exists.
The problem is not necessarily the inventory value itself. The issue is that the application allows multiple operations to make decisions using the same outdated state.
Why Race Condition Vulnerabilities Are Important in Checkout Systems
Checkout systems are especially sensitive to timing issues because they involve several operations that depend on one another.
A typical checkout process may include:
- Validating the shopping cart
- Calculating the final price
- Checking available inventory
- Applying promotional discounts
- Creating an order
- Initiating payment
- Receiving payment confirmation
- Updating order status
- Triggering product delivery
If these operations are not properly coordinated, an attacker may cause the application to enter an unexpected state.
Financial Loss
A race condition may allow a customer to apply a discount more than once, spend the same account balance repeatedly, or trigger duplicate refunds.
Even a small flaw can become expensive when automated requests are used against a high-volume application.
Inventory Manipulation
Online stores often sell products with limited stock. If inventory updates are not atomic, concurrent purchases may exceed the available quantity.
This can create overselling, incorrect stock records, and fulfillment problems.
Duplicate Transactions
Payment systems must handle retries, network interruptions, and repeated callbacks. Without proper transaction controls, the same payment event may trigger more than one business operation.
For example, a repeated payment notification could create multiple order fulfillment events if the application does not recognize that the transaction has already been processed.
Account Balance Manipulation
Wallets, prepaid accounts, and gift cards depend on accurate balance calculations. A race condition may allow multiple spending requests to use the same available balance.
This can result in negative balances or unauthorized value transfers.
Common Types of Race Conditions in Checkout and Transaction Workflows
Race conditions can appear in different parts of an application. Understanding these scenarios helps security testers identify the most sensitive operations.
1. Coupon and Discount Race Conditions
Many e-commerce platforms restrict how often a customer can use a discount code.
For example, a promotional code might be valid only once per account. The application checks whether the customer has already used the code before applying the discount.
If two requests reach the server before the usage record is updated, both may pass the validation.
Potential impact:
- Multiple discount applications
- Repeated promotional benefits
- Unauthorized price reductions
- Financial loss for the business
A tester should examine whether coupon validation and redemption happen as one atomic operation.
2. Payment Confirmation Race Conditions
Payment gateways communicate with merchant applications through redirects, APIs, and server-to-server notifications.
A payment provider may send a notification indicating that a transaction has succeeded. The application must verify the notification and update the associated order.
Problems arise when the same event is processed multiple times without checking the existing transaction state.
For example:
- A customer completes a payment.
- The payment provider sends a successful payment notification.
- The application starts processing the order.
- The notification is delivered again because of a retry.
- The application processes the same order a second time.
If the backend does not implement idempotent processing, this may cause duplicate fulfillment or repeated account credits.
3. Inventory Race Conditions
Inventory management systems must prevent customers from purchasing more items than are available.
Suppose a limited-edition product has only two units remaining. Several customers attempt to purchase it at the same time.
If every request reads the stock count before any request updates it, multiple orders may be accepted using the same inventory.
Potential impact:
- Overselling
- Incorrect stock availability
- Duplicate reservations
- Order cancellation and refund issues
Inventory updates should use atomic database operations or suitable locking mechanisms.
4. Account Balance and Wallet Race Conditions
Digital wallets and prepaid accounts are common targets for transaction logic testing.
Suppose an account contains ₹1,000. A customer initiates two separate payments of ₹800 at nearly the same time.
If both requests read the original balance before either debit is committed, both may pass the balance check.
The resulting balance could become negative, even though the customer initially had enough money for only one transaction.
This type of flaw can affect:
- Digital wallets
- Gift cards
- Prepaid accounts
- Loyalty point systems
- Internal credit systems
5. Duplicate Order Creation
An application may create an order when a customer clicks the checkout button.
However, users sometimes click the button repeatedly because the page appears unresponsive. Browsers, mobile applications, and network libraries may also retry requests.
If the backend treats every request as a new order, the customer may receive multiple orders for one purchase attempt.
This is particularly dangerous when order creation triggers payment processing or product fulfillment.
6. Refund and Cancellation Race Conditions
Refund workflows also contain sensitive state transitions.
Consider an order that has already been refunded. If two refund requests are processed concurrently, both might check that the order is eligible for a refund before either request updates its status.
The system may issue duplicate refunds.
A similar problem can occur when a customer attempts to cancel an order while the payment or fulfillment process is updating the same record.
The application must ensure that refund, cancellation, and fulfillment operations cannot conflict with one another.
How Race Condition Attacks Work
Most transaction-related race conditions follow a similar pattern: an application checks a condition, performs an operation, and updates the relevant record. The vulnerability appears when another request can interfere between those steps.
Understanding the Check-Then-Act Pattern
Consider a simplified coupon redemption process:
def apply_coupon(user_id, coupon_code):
    if not coupon_already_used(user_id, coupon_code):
        apply_discount(user_id, coupon_code)
        mark_coupon_as_used(user_id, coupon_code)
At first glance, this logic looks reasonable.
However, the application performs three separate operations:
- Check whether the coupon has been used.
- Apply the discount.
- Record the coupon as used.
Two requests can execute the first step before either reaches the third step.
Both requests may therefore believe the coupon is available.
This is an example of a Time-of-Check to Time-of-Use (TOCTOU) problem. The state may change between the time the application checks a condition and the time it uses that condition.
Understanding the Race Window
A race window is the period during which another request can interfere with an operation.
For example:
Request A                 Request B
---------                 ---------

Check coupon
                          Check coupon
Coupon available
                          Coupon available

Apply discount
                          Apply discount

Mark as used
                          Mark as used
The exact timing depends on application architecture, database behavior, network latency, and server load.
A race window can be extremely short. However, concurrent requests, retries, and carefully controlled testing can expose it.
Real-World Scenarios and Practical Examples
The following examples illustrate how race conditions may affect real application workflows. They are representative security-testing scenarios, not claims about a particular company’s production system.
Example 1: Applying a Discount More Than Once
An online shopping platform provides a 20% discount coupon that can be used once per account.
The application checks the coupon usage table and finds no existing record. Before it inserts the redemption record, another request performs the same check.
Both requests may receive a successful response.
Expected behavior: The coupon should be redeemed once.
Vulnerable behavior: Multiple requests receive the discount because the redemption check and update are not atomic.
This scenario can lead to unauthorized discounts and revenue loss.
Example 2: Purchasing More Items Than Available
An online store has one remaining unit of a product.
Two customers submit purchase requests at almost the same time. Both requests read the stock count before either transaction updates the database.
If the application does not use an atomic stock update, it may accept both orders.
Expected behavior: Only one purchase should be confirmed.
Vulnerable behavior: Both customers receive confirmation for the same inventory unit.
Example 3: Duplicate Payment Processing
A merchant receives a successful payment notification from its payment provider.
The application starts updating the order and triggering fulfillment. Before the first process finishes, the same notification is delivered again.
If the application does not check whether the event has already been processed, it may trigger fulfillment twice.
Expected behavior: Repeated delivery of the same payment event should not repeat the business operation.
Vulnerable behavior: The same payment event causes duplicate order processing.
Example 4: Spending the Same Wallet Balance Twice
A digital wallet contains ₹2,000. A user initiates two transactions of ₹1,500 almost simultaneously.
Both requests read the available balance as ₹2,000. If the application checks the balance separately from the debit operation, both requests may succeed.
Expected behavior: Only one transaction should be approved.
Vulnerable behavior: Both transactions are accepted, potentially creating a negative balance.
How to Test Race Condition Vulnerabilities
Testing race conditions requires more than sending individual requests and checking their responses. A penetration tester must understand the application’s business rules, identify shared resources, and observe the final state after concurrent operations.
Testing should only be performed on systems for which you have explicit authorization. Use a staging environment or controlled test accounts whenever possible, particularly when working with payments, refunds, and inventory.
Step 1: Understand the Checkout Workflow
Start by mapping the complete checkout process.
Identify the endpoints responsible for:
- Adding products to the cart
- Updating product quantities
- Applying discount codes
- Creating orders
- Initiating payments
- Confirming transactions
- Processing refunds
- Cancelling orders
Use browser developer tools or an intercepting proxy to understand how the frontend communicates with the backend.
Do not focus only on the visible checkout page. Some important operations may happen through background API requests.
Step 2: Identify Sensitive Operations
Look for operations that should happen only once or must follow a specific business rule.
Examples include:
- Redeeming a single-use coupon
- Deducting an account balance
- Confirming a payment
- Creating an order
- Issuing a refund
- Reserving the last available product
Pay special attention to endpoints that follow a check-then-act pattern.
For each operation, document the expected behavior and the conditions under which it should be rejected.
Step 3: Capture and Understand HTTP Requests
Use an intercepting proxy such as Burp Suite or OWASP ZAP to capture the relevant requests.
Review:
- HTTP method and endpoint
- Request body and parameters
- Session cookies and authorization headers
- Order and transaction identifiers
- Response status and message
- Any state-changing fields
Determine whether multiple requests operate on the same user, order, coupon, or transaction.
Step 4: Send Controlled Concurrent Requests
In an authorized test environment, use a request repeater or a controlled test script to submit multiple requests concurrently.
For example, a tester might examine whether two requests attempting to redeem the same test coupon can both succeed.
The purpose is not simply to generate a large number of requests. It is to determine whether the application preserves the expected business rule when operations overlap.
Start with a small number of requests and increase the concurrency gradually if the environment permits it.
Step 5: Examine the Final Application State
HTTP responses alone do not prove that a race condition exists.
A response may indicate success even if the backend later rolls back the operation. Similarly, multiple successful responses do not always mean multiple financial transactions were committed.
Check the actual application state, including:
- Number of orders created
- Final inventory count
- Coupon redemption records
- Account balance
- Payment transaction status
- Refund records
- Fulfillment events
For example, if a coupon is supposed to be redeemed once, verify that the database contains only one successful redemption and that the customer received only one discount.
Step 6: Repeat the Test
Race conditions can be inconsistent because their outcome depends on timing and execution order.
Repeat the test under controlled conditions. Record the number of attempts, successful responses, final database state, and any duplicate side effects.
A single unexpected response is not enough to establish a confirmed vulnerability.
Step 7: Document the Security Finding
A professional penetration testing report should include:
- Vulnerable endpoint and affected workflow
- Required user permissions
- Preconditions for triggering the issue
- Steps performed in the authorized environment
- Expected and actual results
- Evidence of duplicate or inconsistent state
- Business impact
- Recommended remediation
Clearly distinguish between a confirmed security issue and a potential race condition that requires further validation.
Tools Used for Race Condition Testing
Several application security tools can help identify concurrency-related weaknesses. However, no tool can automatically understand every business rule in a checkout workflow.
1. Burp Suite
Burp Suite is widely used for web application penetration testing.
Its Repeater and request grouping capabilities help testers examine how an application responds to repeated and concurrent requests.
The Burp Suite Professional race condition features can also help synchronize requests and investigate timing-related behavior.
2. OWASP ZAP
OWASP ZAP is an open-source web application security testing tool.
It can help intercept, inspect, and modify HTTP requests. Testers can also use scripts and automation to examine application behavior under controlled request patterns.
3. Custom Python Scripts
Python is useful when a test requires precise control over concurrent requests.
A tester can use libraries such as asyncio and aiohttp to create controlled concurrency in an authorized environment.
For example, a test script can submit a small number of requests against a staging endpoint and compare the resulting transaction records.
4. Database Monitoring Tools
Database logs and monitoring tools can help identify transaction conflicts, duplicate updates, and unexpected balance changes.
Depending on the environment, useful options include:
- PostgreSQL logs and monitoring views
- MySQL performance and transaction monitoring
- Application-level transaction logs
- Distributed tracing platforms
Database-level evidence is especially important when validating whether a race condition caused a persistent state change.
5. Static Analysis and Code Review
Source code review can reveal unsafe check-then-act logic, missing synchronization, and incorrect transaction boundaries.
Static analysis may identify some concurrency weaknesses, but reviewers must also understand how the application handles business operations across services and databases.
How to Prevent Race Condition Vulnerabilities
Preventing race conditions requires controls at the application, database, and transaction-processing layers.
A simple frontend restriction is not sufficient. The backend must enforce business rules even when multiple requests arrive at the same time.
1. Use Database Transactions
Database transactions help group related operations into a single logical unit.
For example, a wallet debit should validate the available balance and update it within a properly controlled transaction.
A transaction should either complete successfully or roll back when an operation fails.
However, using BEGIN and COMMIT alone does not automatically prevent every race condition. The application must also select appropriate isolation and locking behavior for the operation.
2. Use Row-Level Locking
Row-level locking prevents conflicting transactions from modifying the same database record at the same time.
For example, PostgreSQL supports SELECT ... FOR UPDATE, which can lock a selected row until the transaction completes.
A simplified example:
BEGIN;

SELECT balance
FROM wallets
WHERE user_id = 101
FOR UPDATE;

-- Validate the available balance in application logic.

UPDATE wallets
SET balance = balance - 500
WHERE user_id = 101
  AND balance >= 500;

COMMIT;
In production code, the application should check the affected row count, handle errors, and roll back when necessary.
This approach helps prevent concurrent requests from spending the same balance, provided the relevant operations use the same locking strategy.
3. Use Atomic Database Updates
An atomic update combines a condition and a change into one database operation.
For example:
UPDATE inventory
SET quantity = quantity - 1
WHERE product_id = 501
  AND quantity > 0;
The application should check the affected row count.
If one row is updated, the reservation succeeded. If no rows are updated, the product was unavailable or the condition was not satisfied.
This is generally safer than reading the stock value into application memory, checking it separately, and updating it later.
4. Implement Idempotency Keys
Idempotency helps ensure that repeating the same request does not repeat its business effect.
For example, a payment initiation endpoint can require a unique idempotency key for each intended payment operation.
If the same request is retried with the same key, the application should return the previously recorded result instead of creating another payment.
A reliable implementation should:
- Associate the key with the authenticated customer and operation.
- Store the key with a unique database constraint.
- Associate it with the request parameters or a request hash.
- Handle simultaneous requests using the same key safely.
- Return the existing result for a completed request.
- Define how failed and incomplete requests are handled.
Idempotency is particularly important for payment retries and repeated provider notifications.
5. Enforce Unique Constraints
Database constraints provide an additional layer of protection against duplicate records.
For example, if a payment provider’s event ID must be processed only once, the application can store it in a table with a unique constraint.
A simplified example:
CREATE TABLE processed_payment_events (
    event_id VARCHAR(255) PRIMARY KEY,
    processed_at TIMESTAMP
);
The application should attempt to insert the event ID as part of a safe processing workflow. If the ID already exists, the event should not trigger the business operation again.
A unique constraint is more reliable than checking for an existing record in application code and inserting it later without database-level protection.
6. Validate Transaction States on the Server
Checkout workflows should use explicit server-side states.
For example:
CREATED
   |
   v
PAYMENT_PENDING
   |
   v
PAID
   |
   v
FULFILLMENT_PENDING
   |
   v
COMPLETED
The application should reject invalid transitions.
An order that is already marked as PAID should not be processed as a new payment simply because another confirmation request arrives.
State transitions should be protected through conditional updates, locking, or another concurrency-safe mechanism.
7. Handle Payment Callbacks Securely
Payment providers may retry notifications when they do not receive a successful response. Merchant applications must be designed to handle repeated delivery.
Important controls include:
- Verify the authenticity of payment notifications.
- Validate the provider’s transaction identifier.
- Match the payment with the correct order and amount.
- Check the current order state.
- Prevent duplicate event processing.
- Ensure fulfillment is triggered only once.
- Record processing outcomes for investigation.
Never rely only on a customer’s browser redirect to decide whether a payment succeeded. The application should verify the transaction through the payment provider’s trusted server-side process.
8. Use Distributed Locking Carefully
Large applications may use multiple servers or microservices. In these environments, an in-memory lock on one server cannot protect a resource shared across all instances.
Distributed locking can help coordinate access to shared resources, but it introduces additional concerns such as lock expiration, network failures, and ownership verification.
Where possible, prefer database constraints, atomic updates, and transaction-level controls for persistent business data. Use distributed locks when the architecture genuinely requires them and implement them with appropriate failure handling.
Best Practices for Securing Checkout and Transaction Workflows
Organizations should treat concurrency as part of their normal application threat model.
The following practices help reduce the risk of race conditions:
- Identify critical operations: Review every workflow that changes money, inventory, permissions, or transaction status.
- Keep validation server-side: Never rely on frontend restrictions to enforce payment or order rules.
- Use atomic operations: Combine checks and updates wherever possible.
- Apply suitable transaction isolation: Choose isolation levels based on the consistency requirements of each operation.
- Use database constraints: Prevent duplicate records and enforce important business rules at the persistence layer.
- Implement idempotency: Make retries safe for payment requests and provider notifications.
- Validate state transitions: Reject repeated or out-of-order operations.
- Test concurrent requests: Include concurrency tests in application security testing and development pipelines.
- Monitor transaction anomalies: Look for duplicate payments, negative balances, repeated coupon use, and unexpected inventory changes.
- Review third-party integrations: Check how payment gateways, order services, and inventory systems handle retries and repeated events.
Teams should also maintain clear transaction logs. These records make it easier to investigate whether an unexpected result came from a race condition, a payment provider retry, or an application integration issue.
Common Mistakes During Race Condition Testing
Race condition testing can produce misleading results when testers focus only on the number of requests or response codes.
Testing Only the Frontend
The user interface may prevent a customer from clicking a button twice. However, an attacker can send requests directly to the backend.
Test the server-side endpoints and verify that the business rules remain enforced.
Treating Every Duplicate Response as a Vulnerability
Two successful HTTP responses do not automatically prove that two payments or orders were committed.
Always inspect the final application state and any external side effects.
Ignoring Asynchronous Processing
Payment systems may use queues, background workers, and event-driven services.
An operation may appear complete in the HTTP response while the actual business processing happens later. Testers should account for these asynchronous steps.
Testing Without Understanding Business Rules
A system may legitimately allow multiple requests for certain operations.
Before reporting a finding, understand the expected limits, transaction states, and business requirements.
Using Excessive Concurrency
Sending a large number of requests without understanding the target can disrupt a service or create unintended financial activity.
Use controlled test accounts, agreed request limits, and a suitable test environment.
How Pentesters Should Report Race Condition Findings
A race condition report should explain the business impact, not just describe the timing issue.
For example, a report about duplicate coupon redemption should include:
Finding: Race condition in single-use coupon redemption.
Affected component: Coupon redemption API.
Expected behavior: Each account can redeem the coupon once.
Observed behavior: Concurrent requests caused the application to record more than one successful redemption for the same account.
Business impact: Unauthorized discounts and potential financial loss.
Evidence: Relevant request and response records, coupon usage history, order totals, and database state from the authorized test environment.
Recommendation: Perform coupon validation and redemption atomically. Enforce a unique database constraint for the account and coupon combination, and handle repeated requests safely.
The report should also mention any conditions that affect reproducibility, such as the number of requests, test environment, and required account state.
Career Opportunities in Application Security Testing
Race condition testing is a useful skill for professionals working in web application penetration testing, API security, and application security engineering.
Many traditional vulnerability scanners focus on recognizable technical patterns. Business logic vulnerabilities often require a deeper understanding of how an application is expected to behave.
Security professionals who can analyze checkout workflows, identify shared resources, test concurrent operations, and explain business impact bring valuable skills to VAPT engagements.
Beginners can build their understanding through structured “https://academy.pentesthint.com/” cyber security training and authorized “https://vuln.pentesthint.com/” hands-on labs.
Practical experience with HTTP requests, databases, APIs, transaction states, and tools such as Burp Suite helps develop the skills needed to assess these issues professionally.
Future Scope of Race Condition Security Testing
Modern applications increasingly rely on distributed architectures, cloud services, event queues, and third-party payment providers.
These systems introduce more points where concurrent operations can interact.
For example, a checkout operation may involve an API gateway, an order service, an inventory service, a payment provider, and a background fulfillment worker. Each component may maintain its own state and retry failed operations.
As a result, application security testing must consider more than individual HTTP endpoints.
Future security assessments will increasingly focus on:
- Concurrency across microservices
- Duplicate event processing
- Distributed transaction consistency
- Payment retry behavior
- Inventory synchronization
- Idempotency across APIs
- Event-driven application security
- Automated concurrency testing
Organizations that include these scenarios in their development and security testing processes will be better prepared to prevent transaction abuse.
Frequently Asked Questions (FAQs)
What is a race condition vulnerability in a web application?
A race condition vulnerability occurs when multiple requests or processes access shared application data concurrently without proper synchronization. The resulting behavior may violate business rules, such as allowing duplicate payments, repeated coupon redemption, or unauthorized balance changes.
How do race conditions affect online checkout systems?
Race conditions can affect several checkout operations, including order creation, inventory reservation, discount redemption, payment confirmation, and refunds. Depending on the weakness, an application may process an operation more than once or accept conflicting updates.
What is a TOCTOU vulnerability?
TOCTOU stands for Time-of-Check to Time-of-Use. It describes a situation where an application checks a condition and then uses the result later, while the underlying state can change between those two steps. It is a common pattern associated with race conditions.
How can penetration testers identify race conditions?
Penetration testers can map sensitive workflows, capture relevant API requests, and send controlled concurrent requests in an authorized environment. They should then inspect the final database and application state to confirm whether the expected business rules were violated.
Can Burp Suite detect race condition vulnerabilities?
Burp Suite provides features that help testers send and synchronize multiple requests. These capabilities can assist with identifying timing-related issues. However, testers still need to understand the application’s business logic and verify the actual impact.
How can developers prevent race conditions in payment systems?
Developers should use atomic database operations, appropriate transaction isolation, row-level locking where necessary, unique constraints, and idempotency controls. Payment notifications should also be authenticated, validated, and processed safely when providers retry delivery.
Are race conditions the same as business logic vulnerabilities?
They are closely related, but they are not identical. A race condition is a concurrency weakness that can cause unexpected behavior. A business logic vulnerability occurs when an application fails to enforce its intended business rules. A race condition can create or expose a business logic vulnerability.
Why are race conditions difficult to detect?
Race conditions depend on timing, request execution order, database behavior, and application architecture. They may not occur during normal testing, and a successful HTTP response does not always reveal whether the backend entered an inconsistent state. Repeated controlled testing and state verification are often necessary.
Conclusion
Race condition vulnerabilities can create serious security and business risks in checkout and transaction workflows. A small timing gap between validation and execution may allow duplicate coupon redemption, overselling, repeated payment processing, unauthorized refunds, or incorrect account balances.
Preventing these issues requires more than frontend validation or basic request filtering. Applications must protect critical operations through atomic database updates, appropriate locking, unique constraints, idempotency, and secure transaction state management.
For penetration testers, the key is to understand the application’s business rules, identify operations that should happen only once, test them under controlled concurrency, and verify the final application state before reporting a vulnerability.
For organizations building or securing payment-driven applications, regular application security assessments can help uncover weaknesses before they lead to financial loss or customer impact.
Explore “https://pentesthint.com/” PentestHint for cybersecurity resources and professional security assessment support. A well-tested transaction workflow is not just a reliability requirement; it is an essential part of application security.