Multi-tenant SaaS penetration testing is an important part of securing cloud-based applications that serve multiple customers through a shared platform. A single SaaS application may host thousands of organizations, each storing sensitive business information, managing its own users, and configuring its own permissions. If the application fails to separate these customers correctly, one tenant may gain unauthorized access to another tenant’s data.
Tenant isolation is therefore more than a cloud configuration requirement. It is an application security control that must work consistently across APIs, databases, background jobs, file storage, search services, and administrative functions.
As SaaS platforms adopt shared infrastructure, microservices, and increasingly complex API integrations, testing only the login page or individual user roles is not enough. Security teams must verify that the application enforces tenant boundaries throughout the entire request and data-processing lifecycle.
This guide explains how to test tenant isolation, identify cross-tenant vulnerabilities, validate authorization controls, and recommend practical fixes. It is intended for penetration testers, application security engineers, SaaS developers, and organizations conducting authorized security assessments.
What Is a Multi-Tenant SaaS Application?
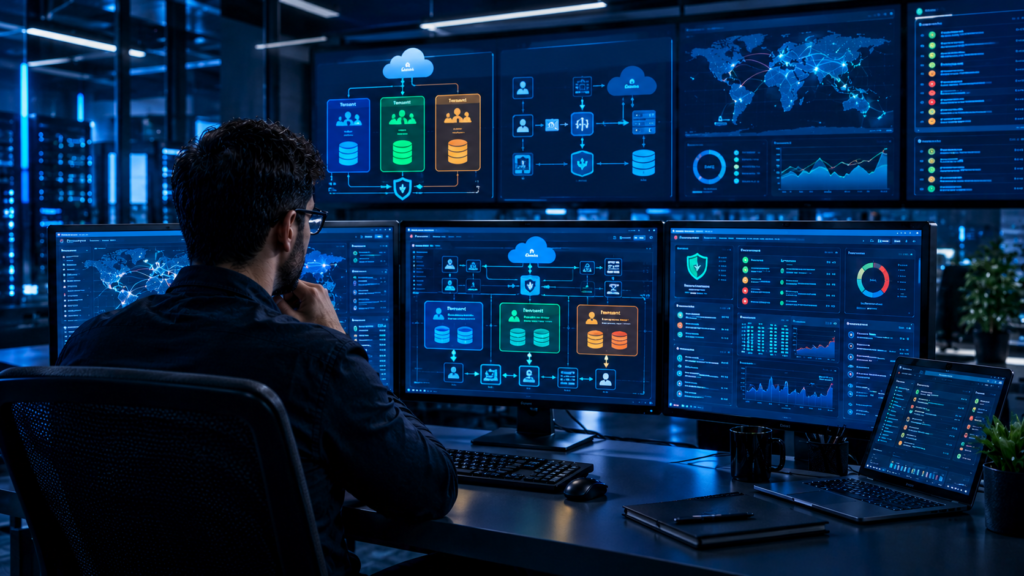
A multi-tenant Software as a Service (SaaS) application allows multiple customers, known as tenants, to use the same application or service while keeping their data and permissions logically separated.
For example, a project management platform might serve Company A, Company B, and Company C through the same web application. Each company has its own users, projects, documents, billing information, and administrative settings.
The application may use shared application servers and databases to reduce operating costs. However, shared infrastructure must not mean shared access to customer information.
How tenant isolation works
A typical SaaS application identifies the tenant associated with a user and enforces that tenant’s permissions whenever the user requests a resource.
A simplified request flow looks like this:
1. User authentication
Verify identity and establish a trusted session.
2. Tenant context
Resolve the user’s authorized tenant from trusted identity and membership data.
3. Authorization checks
Verify tenant membership, role, and permission for the requested resource.
4. Scoped data access
Return or modify only the resources the user is authorized to access.
Every stage matters. Authentication confirms who the user is, but it does not automatically establish which tenant’s resources the user may access.
For example, a legitimate user from Company A may change a project ID in an API request. If the application retrieves the project without checking its tenant ownership, the user could access a project belonging to Company B.
That is an authorization failure, even though the user authenticated successfully.
Common multi-tenant architectures
Tenant isolation can be implemented in different ways.
- Shared database and shared tables: Multiple tenants use the same tables, with a tenant identifier separating their records.
- Shared database with separate schemas: Each tenant’s records are stored in a separate database schema.
- Separate database per tenant: Each tenant has its own database, providing a stronger structural boundary when configured correctly.
- Hybrid architecture: Different services or data types use different isolation approaches.
No architecture automatically guarantees security. Shared tables require reliable tenant-scoped queries, while separate databases still require correct connection routing, authorization, and administrative controls.
Why Is Tenant Isolation Testing Important?
A tenant isolation failure can affect multiple customers through a single application vulnerability. The impact may include unauthorized disclosure, data modification, account takeover, or access to confidential business operations.
1. Preventing cross-tenant data exposure
Customer records, invoices, employee details, uploaded documents, and API responses must remain accessible only to authorized users.
A missing tenant check can expose these resources even when the application’s login and password controls work correctly.
2. Protecting customer trust
SaaS customers expect their information to remain separate from that of other organizations. A cross-tenant incident can damage customer relationships, trigger contractual obligations, and create substantial incident response costs.
3. Meeting security and compliance requirements
Depending on the application and its customers, tenant isolation may support privacy obligations, contractual commitments, and security assurance programs.
Relevant frameworks and guidance include the OWASP Application Security Verification Standard (ASVS), the OWASP API Security Top 10, and applicable cloud security requirements.
4. Finding authorization flaws that scanners may miss
Automated vulnerability scanners can identify some common weaknesses, but they may not understand tenant membership, business relationships, or application-specific permissions.
Testing with multiple controlled tenant accounts allows security professionals to check whether the application enforces the intended access boundaries.
Common Tenant Isolation Vulnerabilities
The first step in a SaaS penetration test is understanding where tenant boundaries may fail.
1. Insecure Direct Object Reference (IDOR)
IDOR occurs when an application exposes an object identifier but fails to verify that the current user is authorized to access the referenced object.
For example, an invoice API may accept a request such as:
GET /api/invoices/4821
Authorization: Bearer <tenant-a-test-token>
The application returns the invoice based on its identifier alone. If invoice 4821 belongs to another tenant and the API does not enforce ownership, the request may disclose another customer’s information.
Identifiers can be sequential integers, UUIDs, filenames, or other values. Using unpredictable identifiers can reduce discoverability, but it does not replace authorization checks.
What to test: Using explicitly authorized test accounts, verify that a user cannot retrieve another tenant’s invoices, projects, documents, or other resources by changing object identifiers.
2. Broken Object-Level Authorization (BOLA)
Broken Object-Level Authorization is a common API security weakness in which the application does not correctly authorize access to a particular object.
It overlaps with IDOR, but BOLA is especially useful when examining APIs that accept resource IDs in paths, query parameters, or request bodies.
Consider a SaaS CRM platform where users can retrieve customer records through an API. The API authenticates the user but fails to check whether the requested customer record belongs to the user’s tenant.
The endpoint may work as designed from a technical perspective while exposing a serious security flaw.
The OWASP API Security Top 10 provides useful guidance for understanding this class of vulnerability.
3. Broken Function-Level Authorization
A user may belong to the correct tenant but still lack permission to perform a particular action.
For example, a regular employee may be allowed to view company projects but not delete them, manage billing, or invite new administrators.
If the backend checks tenant membership but ignores the user’s role, the application may allow unauthorized administrative operations.
Test both dimensions independently:
- Is the user authorized for the tenant?
- Is the user authorized to perform the requested action?
Both checks must succeed where required.
4. Tenant context manipulation
Some applications accept a tenant identifier through a URL parameter, request header, subdomain, or JSON field.
For example:
GET /api/projects
X-Tenant-ID: tenant-a
Authorization: Bearer <test-token>
The header itself is not inherently insecure. The risk appears when the server trusts a client-supplied tenant identifier without verifying that the authenticated user has permission to act within that tenant.
An attacker may attempt to substitute another tenant’s identifier and observe whether the application returns unauthorized data.
What to test: Change the tenant context only within the approved test environment and verify that the server rejects tenant identifiers for which the current account has no membership or permission.
5. Cross-tenant privilege escalation
Privilege escalation occurs when a user gains permissions beyond those intended for their account.
In a multi-tenant environment, the problem may cross tenant boundaries. A user who is an administrator of Tenant A must not automatically become an administrator of Tenant B.
Common weaknesses include:
- Incorrect role mapping.
- Shared administrative permissions.
- Missing membership checks.
- Improperly scoped invitation or role-management APIs.
- Authorization decisions based on untrusted request fields.
Test role changes, membership management, and administrative functions using controlled accounts with known permissions.
6. Cross-tenant file and object storage access
SaaS applications frequently store uploads, reports, exports, backups, and generated documents in object storage.
Even if the main API enforces tenant isolation, a file may be exposed through a publicly accessible storage object or a signed URL that remains valid longer than intended.
Check whether:
- Files are stored under appropriately controlled tenant-specific namespaces.
- Download endpoints verify authorization.
- Signed URLs have appropriate permissions and expiry times.
- File metadata does not reveal another tenant’s information.
- Export jobs preserve the correct tenant context.
- Deleted or revoked resources become inaccessible as intended.
A successful test should establish whether the file can be accessed outside the intended authorization boundary, without unnecessarily downloading sensitive content.
7. Cross-tenant leakage through background jobs and caches
Not every tenant isolation issue occurs during a direct web request.
Background jobs may process exports, reports, notifications, or scheduled tasks. If a worker uses an incorrect tenant context, it could associate one customer’s data with another customer’s account.
Shared caches can also leak data if the cache key does not include the tenant or another appropriate authorization context.
For example, a dashboard endpoint might cache a report using only the report type rather than the tenant identifier. A second tenant could then receive the first tenant’s cached response.
Testing should therefore include asynchronous workflows, cached responses, search indexes, and generated reports where these features exist.
How to Perform Multi-Tenant SaaS Penetration Testing
A reliable assessment should test the application’s tenant boundaries systematically. The following workflow assumes you have written authorization, approved test accounts, and access to a test environment or explicitly approved production targets.
Step 1: Review the architecture and scope
Start by understanding how the application separates tenants.
Identify:
- Tenant registration and membership workflows.
- Authentication and session management.
- User roles and permissions.
- API endpoints that access tenant-owned resources.
- Database and storage architecture.
- Background workers, caching layers, and search services.
- Administrative functions and support access.
Review architecture diagrams and API documentation when available. Ask the development team how tenant context is established and which components enforce authorization.
Document which assets and test accounts are approved. Do not probe other customers’ accounts or production data without explicit authorization.
Step 2: Prepare two or more test tenants
Create at least two controlled tenants with separate test users and clearly distinguishable synthetic data.
For example:
Tenant A
User: user-a
Project: PROJECT-A-TEST
Invoice: INVOICE-A-TEST
Tenant B
User: user-b
Project: PROJECT-B-TEST
Invoice: INVOICE-B-TEST
Use synthetic records that cannot be confused with real customer data.
Create different roles where appropriate, such as a tenant administrator and a regular user. Record which resources each account should be able to access.
This creates a reliable baseline against which you can compare application behavior.
Step 3: Map the application endpoints
Use browser developer tools, API documentation, and an authorized intercepting proxy to identify endpoints that read or modify tenant-owned resources.
Pay particular attention to operations involving:
- Projects and customer records.
- Invoices and subscriptions.
- User invitations and membership.
- File uploads and downloads.
- Reports and exports.
- Search and filtering.
- Administrative actions.
- API keys and integration settings.
Classify each endpoint by HTTP method, resource type, required role, and expected tenant boundary.
An endpoint inventory helps identify gaps that may not be visible from the user interface.
Step 4: Test horizontal access control
Horizontal access control testing checks whether one user can access resources belonging to another user or tenant without the required permission.
With Tenant A’s authorized test session, request a known test resource belonging to Tenant B. Repeat the test for relevant read and write operations.
For example, if Tenant B owns a synthetic project, test whether Tenant A can:
- View its details.
- Retrieve its associated files.
- Modify its description.
- Add members.
- Delete it.
Use harmless test records and stop if the application exposes real customer data or causes unexpected side effects.
A correct implementation should enforce the authorization policy on the server, regardless of whether the client interface hides the resource.
Step 5: Test vertical access control
Vertical access control testing evaluates whether a user can perform actions reserved for a more privileged role.
Within the same tenant, compare the permissions of a regular user and an administrator. Then check whether administrative permissions remain confined to that tenant.
For example, a regular user might be able to read a project but should not be allowed to change billing settings or assign administrative roles.
The expected response depends on the application’s authorization policy. A request may receive an HTTP 403 Forbidden, an appropriate 404 Not Found, or another documented response. The important requirement is that unauthorized access or modification does not occur.
Step 6: Verify tenant context across API requests
Test how the backend establishes the active tenant and whether the tenant context remains consistent throughout a request.
Review tenant identifiers supplied through:
- Request paths and query parameters.
- Custom headers.
- JSON request bodies.
- Subdomains.
- Session data and access tokens.
A client-provided tenant identifier can be a legitimate part of an API design, but the server must validate it against the authenticated user’s authorized memberships.
Also inspect token claims and tenant-switching workflows. A token containing a tenant identifier should not be treated as sufficient authorization for every resource or action within that tenant.
Step 7: Test write operations and indirect access
Read-only testing is not enough. Some authorization failures appear only when a user modifies a resource or triggers a workflow.
Within the approved test environment, check whether one tenant can change another tenant’s records, alter memberships, generate exports, or trigger actions that expose cross-tenant information.
Use reversible changes where possible. Avoid destructive operations against production resources unless they are explicitly authorized and controlled.
Step 8: Test supporting services
Follow the data beyond the main application API.
Check how tenant context is enforced in:
- Cached API responses.
- Search results and autocomplete.
- Object storage and download links.
- Scheduled reports and exports.
- Webhooks and event processing.
- Background jobs.
- Notifications and email attachments.
- Support and administrative tooling.
For asynchronous workflows, verify that the tenant context is explicitly associated with the job and revalidated when necessary. Do not assume that the identity of the user who originally triggered the job will automatically remain available or valid.
Step 9: Document evidence and verify remediation
For each finding, record the affected endpoint, the test accounts used, the expected access policy, the observed behavior, and the security impact.
Use synthetic records to demonstrate unauthorized access whenever possible. Redact tokens, credentials, and sensitive information from screenshots and request logs.
After remediation, repeat the original test and run regression tests against related endpoints. A fix to one API route does not prove that every route accessing the same resource enforces tenant isolation.
Real-World Example: Broken Tenant Isolation in a SaaS CRM
Consider a cloud-based customer relationship management platform used by multiple businesses.
Each tenant has its own contacts, sales opportunities, and reports. Users authenticate successfully and can access the application dashboard.
During an authorized penetration test, the tester creates a contact in Tenant B and records its test identifier. The tester then uses Tenant A’s test session to request that contact through the documented API.
The API returns the contact details because the backend checks that the user is authenticated but does not verify that the contact belongs to the user’s tenant.
Security impact
An attacker who exploits the same weakness might access confidential contact information belonging to another customer. If the issue also affects write operations, the attacker might modify or delete records.
The severity depends on the sensitivity of the exposed data, the scope of access, the affected roles, and whether additional controls limit exploitation.
Root cause
The application retrieves the contact using its resource ID without enforcing tenant ownership or an equivalent authorization policy.
Recommended remediation
The development team should enforce authorization at the server-side data access layer, ensuring that every resource operation checks the authenticated user’s tenant membership and permissions.
A tenant-scoped query might conceptually follow this pattern:
SELECT *
FROM contacts
WHERE contact_id = :contact_id
  AND tenant_id = :authorized_tenant_id;
Here, :authorized_tenant_id must come from trusted, validated server-side authorization context, not blindly from a client-controlled value.
The application should apply the same principle to updates, deletions, exports, and related resources. Depending on the architecture, centralized authorization policies, database row-level security, or separate tenant databases may provide additional protection.
Retesting the fix
The tester repeats the cross-tenant request using the same controlled accounts and confirms that Tenant A can no longer retrieve or modify Tenant B’s contact.
The team then checks related endpoints to ensure that the correction applies consistently across the application.
Tools Used for Tenant Isolation Testing
Tools can help identify and validate authorization flaws, but effective tenant isolation testing also requires knowledge of the application’s intended access policies.
Burp Suite
Burp Suite can help intercept HTTP requests, compare authenticated sessions, inspect API responses, and replay authorized test requests. It is particularly useful for examining object identifiers, request parameters, and role-based behavior.
Official resource: PortSwigger Web Security Academy.
OWASP ZAP
OWASP ZAP supports web application testing, request inspection, and automated scanning. It can assist with discovery, but tenant-specific authorization failures may require manual test cases and multiple controlled accounts.
Official resource: OWASP ZAP.
Postman
Postman can organize API requests for different test users and environments. Separate environments and carefully managed test credentials make it easier to compare responses across tenant contexts.
Official resource: Postman Learning Center.
Browser developer tools
Browser developer tools help testers inspect application requests, responses, cookies, local storage, and frontend behavior. They are useful for understanding how the application passes tenant context to its APIs.
However, hiding a tenant’s data in the frontend is not a security boundary. The server must independently enforce access control.
Automated API tests
Custom integration tests can verify that users from one tenant cannot read or modify resources owned by another tenant. These tests are especially useful in CI/CD pipelines because they can catch authorization regressions before deployment.
Best Practices for Preventing Cross-Tenant Vulnerabilities
Tenant isolation should be designed into the application rather than added after a penetration test identifies a problem.
Enforce authorization on the server
Every operation involving tenant-owned data should validate the authenticated user’s identity, tenant membership, role, and permissions. Do not rely on frontend checks or hidden interface elements.
Derive tenant context from trusted sources
Validate any tenant identifier supplied by a client against the user’s authorized memberships. Use a consistent mechanism to establish tenant context for each request.
Scope database queries correctly
Apply tenant constraints to reads and writes. Consider database-level protections, such as row-level security, where suitable for the architecture.
Ensure that background jobs and administrative functions follow the same authorization model.
Use deny-by-default access controls
When the application cannot establish that access is permitted, it should not grant access by default. Explicitly define which roles can perform which operations on which resources.
Test all resource operations
Do not test only GET endpoints. Review creation, update, deletion, export, search, bulk operations, and asynchronous workflows where applicable.
Isolate caches and storage
Include tenant and relevant authorization context in cache keys where required. Restrict file access through server-side authorization and appropriately scoped, short-lived signed URLs.
Build tenant isolation into automated testing
Maintain tests that cover multiple tenants and roles. Run them after changes to authentication, authorization, database access, and API behavior.
Monitor suspicious cross-tenant access attempts
Log relevant authorization failures and unusual access patterns while avoiding unnecessary collection of sensitive data. Monitoring can help detect repeated attempts to access resources outside the user’s tenant.
For further application security guidance, the OWASP Cheat Sheet Series provides practical recommendations for access control, authorization, and secure development.
Common Mistakes to Avoid During Tenant Isolation Testing
Even experienced testers can miss important weaknesses if they focus only on obvious IDOR issues.
- Testing only one tenant: A single account cannot demonstrate whether cross-tenant boundaries work. Use at least two controlled tenants.
- Testing only the user interface: Frontend restrictions may hide features without preventing direct API access.
- Ignoring write operations: Unauthorized modifications can be more damaging than read-only exposure.
- Assuming UUIDs guarantee security: Unpredictable identifiers do not replace authorization checks.
- Ignoring asynchronous processing: Background jobs, scheduled reports, and event handlers may lose or misapply tenant context.
- Overlooking administrative features: Support dashboards, tenant switching, and customer management tools can have broader access than ordinary user interfaces.
- Failing to retest related endpoints: A fix to one route may leave the same weakness in another API or export function.
- Collecting excessive evidence: Demonstrate the issue using synthetic data and the minimum evidence necessary.
A thorough assessment examines the application’s authorization model across its complete data lifecycle rather than relying on a few successful or unsuccessful requests.
Career Opportunities in SaaS Security Testing
Tenant isolation testing is a useful specialization for professionals pursuing roles in application security, API penetration testing, cloud security, and vulnerability assessment.
Important skills include:
- HTTP and REST API fundamentals.
- Authentication and authorization testing.
- IDOR and BOLA vulnerability identification.
- JWT and session security.
- SQL and database access controls.
- Cloud storage and identity security.
- Secure coding and access-control design.
- Technical reporting and remediation validation.
Beginners can develop these skills through the PentestHint cyber security academy and authorized cyber security labs. Practice with deliberately vulnerable applications and synthetic accounts before applying testing techniques to real systems.
For organizations that need an independent assessment, PentestHint provides a starting point for exploring professional security assessment and VAPT services.
Future of Multi-Tenant SaaS Security
As SaaS platforms grow, tenant isolation will remain a central application security concern. More services, distributed architectures, shared data platforms, and automated workflows create additional places where authorization context can be lost or incorrectly applied.
Several practices will become increasingly important:
- Continuous authorization testing: Run tenant-boundary regression tests whenever relevant application code changes.
- Policy-driven access control: Centralize authorization rules where practical to reduce inconsistent checks across services.
- Cloud-native isolation: Use suitable database, identity, and storage controls to reinforce application-level boundaries.
- Automated security testing: Include cross-tenant access scenarios in development and deployment pipelines.
- Improved monitoring: Detect repeated unauthorized access attempts and unexpected patterns in resource access.
- Security by design: Include tenant isolation requirements during architecture reviews and feature development, not only before release.
Automation can improve consistency, but it cannot fully replace an understanding of business logic. Security teams must still determine which users should access which resources and validate that the implemented controls match those requirements.
FAQs About Multi-Tenant SaaS Penetration Testing
1. What is tenant isolation in SaaS security?
Tenant isolation ensures that one SaaS customer cannot access another customer’s data, resources, or administrative functions without explicit authorization. It applies across application APIs, databases, storage, caches, and background processing.
2. What is multi-tenant SaaS penetration testing?
It is an authorized security assessment that evaluates whether a SaaS application correctly separates tenants. Testers examine authentication, authorization, API endpoints, tenant context, data access, and supporting services for cross-tenant vulnerabilities.
3. What is the difference between IDOR and BOLA?
IDOR describes a vulnerability in which an application exposes a resource reference without properly checking access permissions. BOLA, a term commonly used in API security, describes broken authorization at the object level. The concepts overlap substantially, and both can lead to cross-tenant data exposure.
4. How can penetration testers test tenant isolation safely?
Use written authorization, at least two controlled tenant accounts, and synthetic records. Test cross-tenant read and write operations, compare expected and actual permissions, avoid real customer data, and stop if testing produces unexpected exposure or operational impact.
5. Does using separate databases guarantee tenant isolation?
No. Separate databases can strengthen structural separation, but incorrect connection routing, overly privileged service accounts, administrative access, or flawed authorization logic can still expose data across tenants.
6. Which tools are useful for SaaS tenant isolation testing?
Burp Suite and OWASP ZAP can help inspect and test web requests, while Postman can organize API tests across different user accounts. Custom automated integration tests are also valuable for detecting authorization regressions.
7. How can developers prevent cross-tenant data leakage?
Developers should enforce server-side authorization, validate tenant membership, scope database operations correctly, protect caches and file storage, restrict privileged functions, and automate cross-tenant regression tests.
8. How often should tenant isolation be tested?
Test tenant isolation before major releases, after changes to authentication or authorization, when introducing new APIs or data-processing services, and as part of recurring security assessments. Automated regression tests should run regularly throughout development.
Conclusion
Multi-tenant SaaS penetration testing helps organizations verify that customer boundaries remain intact across applications, APIs, databases, and supporting services. A single missing authorization check can expose another tenant’s records, while weaknesses in background jobs, caches, or file storage can bypass protections implemented in the main application.
A strong assessment starts with a clear understanding of the architecture, uses multiple controlled tenant accounts, and tests both read and write operations across different roles. Findings should include reproducible evidence, a clear explanation of business impact, and practical remediation guidance.
For SaaS developers, tenant isolation must be enforced consistently on the server and supported by database controls, secure storage, and automated regression testing. For penetration testers, the goal is not simply to find a vulnerable endpoint but to establish whether the application’s tenant boundaries actually protect customer information.
Strengthen your SaaS security testing skills with PentestHint. Explore cybersecurity learning resources and VAPT services to build a more effective approach to identifying and preventing cross-tenant vulnerabilities.