JWT Security Best Practices: Secure JSON Web Token Implementation
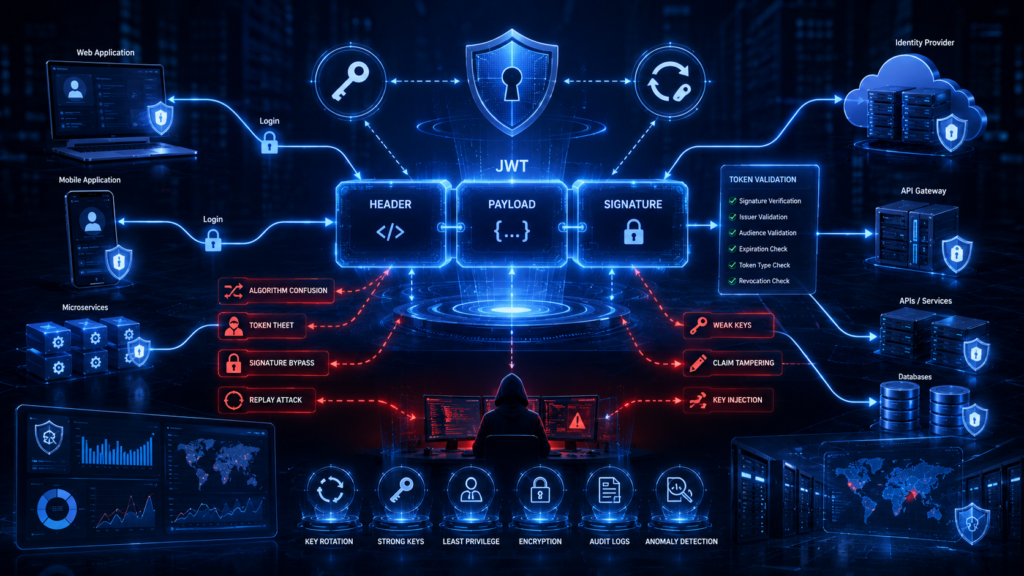
JSON Web Tokens are widely used to carry authentication and authorization information between applications, APIs, identity providers, and microservices. Because JWTs can...
OAuth 2.0 has become one of the most widely used authorization frameworks for modern web applications, APIs, mobile applications, and cloud services....
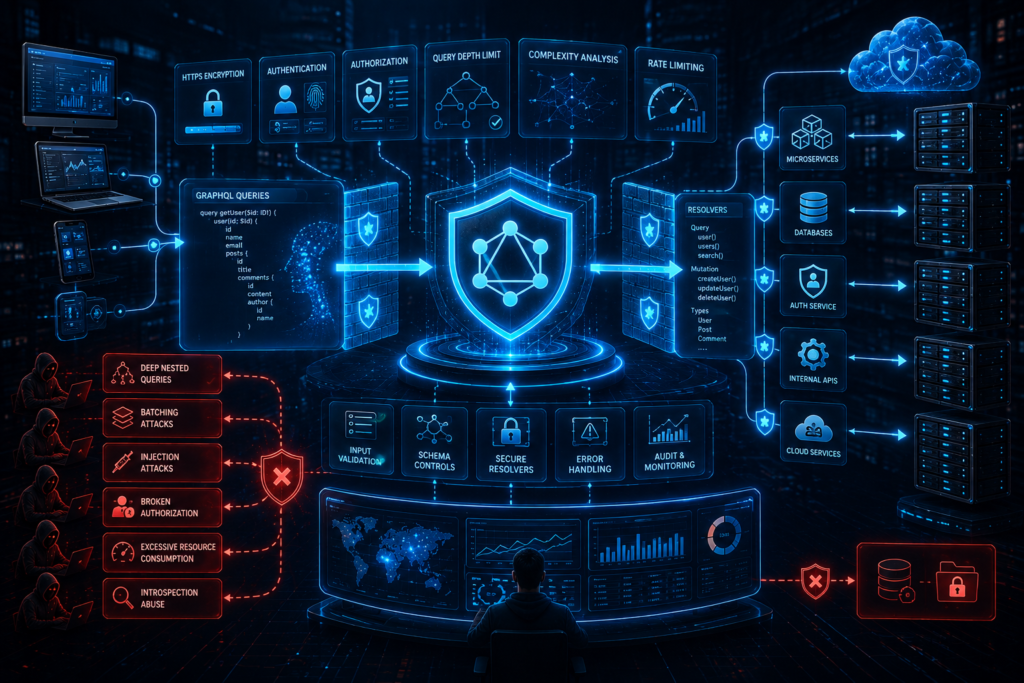
GraphQL has changed how modern applications communicate with backend services. Instead of exposing many fixed endpoints like a traditional REST API, GraphQL...
REST APIs are now a core part of modern software. Web applications, mobile applications, cloud platforms, SaaS products, payment systems, and microservices...
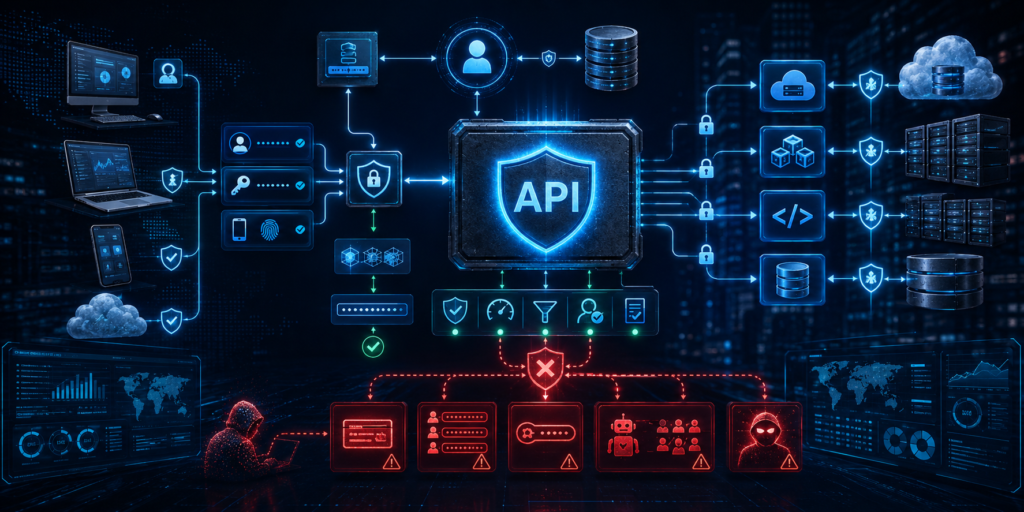
APIs have become the backbone of modern applications. Mobile apps, SaaS platforms, payment systems, cloud services, microservices, and third-party integrations all depend...
Server-Side Request Forgery (SSRF) is a web application security vulnerability that allows an attacker to influence requests made by a server. Instead...
Cross-Site Scripting (XSS) is one of the most common web application security vulnerabilities. It occurs when an application allows untrusted data to...
Web applications often rely on browser sessions and cookies to identify authenticated users. Once a user logs in, the browser automatically sends...
Uploading a file to a website looks simple. A user selects a document, image, PDF, or profile picture, and the application stores...
Authentication acts as the primary gateway protecting sensitive data, user accounts, and administrative features in modern web applications. When these mechanisms fail...