
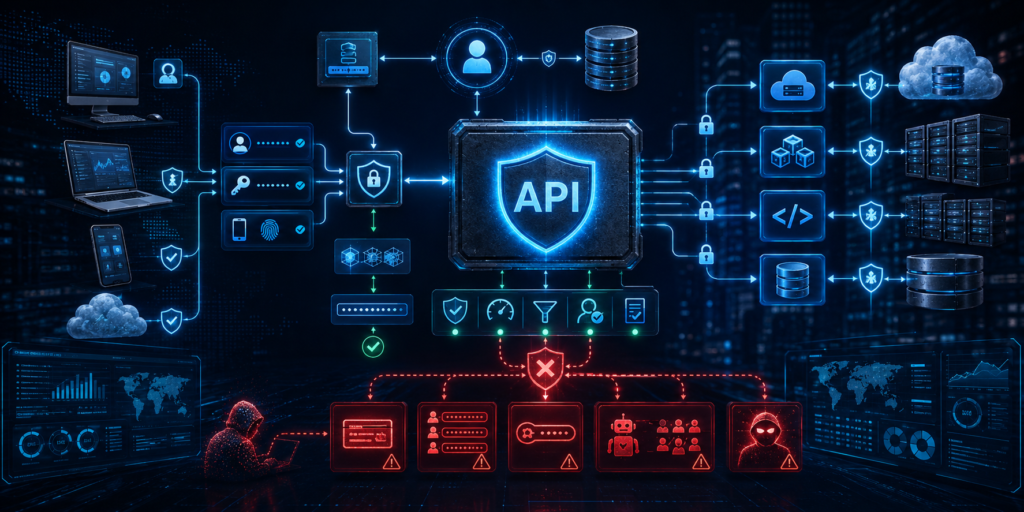
APIs have become the backbone of modern applications. Mobile apps, SaaS platforms, payment systems, cloud services, microservices, and third-party integrations all depend on APIs to exchange data. That also makes APIs an attractive target for attackers.
API authentication best practices are therefore not limited to choosing between API keys and JWTs. A secure authentication design must protect credentials, validate tokens correctly, restrict privileges, prevent replay attacks, monitor suspicious activity, and make sure authentication is followed by proper authorization.
This matters because authentication failures remain a major API security problem. OWASP’s API Security Top 10 includes Broken Authentication as API2:2023, alongside authorization failures, unrestricted resource consumption, and security misconfiguration.
Modern API environments also introduce additional challenges. Applications increasingly use distributed microservices, OAuth-based identity providers, short-lived access tokens, mobile clients, machine-to-machine authentication, and cloud infrastructure. A weakness in any one authentication component can expose sensitive resources.
For developers, security engineers, and penetration testers, understanding how these mechanisms work is essential.
What Is API Authentication?
API authentication is the process of verifying the identity of a user, application, device, or service before allowing it to access a protected API.
In simple terms, authentication answers:
“Who are you?”
Authorization answers a different question:
“What are you allowed to do?”
For example, suppose an e-commerce API contains:
GET /api/orders/12345The API may first authenticate the requester using an access token.
After authentication, the application should determine whether that authenticated user actually owns order 12345.
This distinction is extremely important. A valid token does not automatically mean that the requester should have access to every object or endpoint.
OWASP specifically identifies Broken Object Level Authorization and Broken Function Level Authorization among the major API security risks.
For additional practical security resources, organizations can also explore “https://pentesthint.com/” PentestHint for cybersecurity and VAPT-related content.
Why API Authentication Is Important
A poorly protected API can expose much more than a login page.
Attackers may target APIs to:
- Steal customer information
- Access private user accounts
- Modify application data
- Abuse payment functionality
- Enumerate user accounts
- Perform credential stuffing
- Replay stolen tokens
- Extract sensitive business information
- Consume expensive cloud resources
- Abuse administrative functionality
Consider a mobile banking application.
The mobile application might communicate with endpoints such as:
POST /api/login
GET /api/profile
GET /api/accounts
POST /api/transfer
If the authentication system protects /api/login but fails to properly protect /api/transfer, an attacker may be able to perform unauthorized transactions.
This is why authentication should be considered part of a broader API security architecture rather than a single login mechanism.
API Authentication Best Practices
There is no single authentication method that works perfectly for every API. The right design depends on the type of client, sensitivity of the data, trust boundaries, and threat model.
The following practices provide a strong baseline.
1. Always Use HTTPS
Authentication credentials and tokens should never travel over unencrypted HTTP.
Use HTTPS for:
- Login requests
- Token requests
- API requests
- Password reset flows
- OAuth redirects
- Administrative endpoints
Without TLS, an attacker positioned between the client and server may capture credentials or bearer tokens.
For example, this is unsafe:
http://api.example.com/loginA secure API should use:
https://api.example.com/loginHTTPS protects data while it travels across the network, but it does not fix authentication logic vulnerabilities. An application can still have broken authorization, weak tokens, or insecure session management while using HTTPS.
2. Choose the Authentication Mechanism Based on the Client
Different clients require different authentication approaches.
Browser-Based Applications
Modern web applications commonly use session-based authentication or OAuth/OIDC-based identity systems.
Mobile Applications
Mobile applications commonly use OAuth 2.0 or OpenID Connect flows with appropriately protected tokens.
Machine-to-Machine APIs
Backend services may use:
- OAuth 2.0 client credentials
- Mutual TLS
- Private-key-based client authentication
- Other service identity mechanisms
Public APIs
API keys may be appropriate for identifying clients or controlling usage, but they should not automatically be treated as sufficient protection for sensitive resources.
OWASP notes that API keys can help control API access and abuse, but they are relatively easy to compromise when issued to third-party clients and should not be relied on exclusively for sensitive or high-value resources.
3. Avoid Sending Passwords to Every API Endpoint
A common architectural mistake is allowing every API endpoint to accept a username and password.
For example:
GET /api/profile
Authorization: Basic username:password
This increases the exposure of the user’s primary credential.
A better approach is to authenticate the user through a dedicated authentication system and then use an appropriate session or access token for subsequent requests.
OAuth 2.0 is widely used for delegated API access, while OpenID Connect adds an identity layer on top of OAuth 2.0. OWASP recommends avoiding the Resource Owner Password Credentials grant because it exposes the user’s credentials to the client.
4. Use Short-Lived Access Tokens
Access tokens should generally have a limited lifetime.
Suppose an attacker steals an access token that remains valid for 30 days.
The attacker potentially has a large window in which to abuse it.
Now consider a token that expires after a short period.
The impact of token theft is reduced because the stolen credential eventually becomes invalid.
A common architecture looks like this:
User
  |
  v
Identity Provider
  |
  v
Access Token
  |
  v
API Gateway
  |
  v
API Service
The API should validate the token before processing the protected request.
Short token lifetimes do not eliminate the need for secure storage and revocation strategies. They simply reduce the useful lifetime of a stolen token.
5. Validate JWTs Correctly
JSON Web Tokens, or JWTs, are widely used for API authentication.
A JWT typically contains:
Header.Payload.SignatureThe payload may contain claims such as:
{
  "sub": "user-123",
  "iss": "https://identity.example.com",
  "aud": "payments-api",
  "exp": 1780000000,
  "scope": "payments:read"
}
A common mistake is assuming that decoding a JWT is equivalent to validating it.
It is not.
The API should properly validate relevant security properties, including:
- Signature
- Signing algorithm
- Issuer (
iss) - Audience (
aud) - Expiration (
exp) - Not-before (
nbf) where applicable - Required scopes or permissions
Do not blindly trust claims supplied by the client.
For example, an API should not simply decode:
{
  "role": "admin"
}
and assume that the requester is an administrator.
The server must establish trust in the token and its issuer before using security-sensitive claims.
6. Do Not Put Sensitive Information Inside Tokens
JWT payloads are normally encoded rather than encrypted.
That means anyone who obtains the token may be able to decode its payload.
Avoid placing sensitive information such as:
- Passwords
- API secrets
- Private keys
- Authentication recovery information
- Highly sensitive personal data
inside a normal JWT payload.
Keep tokens focused on the information required for authentication and authorization.
7. Protect API Keys Properly
API keys are still useful, particularly for service identification, usage controls, and lower-risk integrations.
However, developers frequently make the mistake of treating an API key like a password and then exposing it accidentally.
Never hardcode production secrets in:
- Public GitHub repositories
- Mobile application source code
- JavaScript bundles
- Documentation examples
- Client-side configuration
- Public Docker images
For example, this is a bad practice:
const API_KEY = "sk-production-secret";Use a secure secrets-management solution on the server side instead.
API keys should also have:
- Limited privileges
- Appropriate expiration or rotation
- Monitoring
- Revocation capability
- Environment separation
- Restricted scope where supported
8. Implement Multi-Factor Authentication for Sensitive Accounts
Authentication based only on a password creates a single point of failure.
If an attacker obtains the password through phishing, credential stuffing, malware, or a data breach, the account may be compromised.
MFA adds another authentication factor.
For high-value accounts, prioritize phishing-resistant methods where practical.
CISA recommends phishing-resistant MFA for high-risk accounts, particularly privileged administrator accounts. FIDO-based authenticators and PKI-based methods are examples of phishing-resistant approaches.
NIST’s current SP 800-63B-4 guidance, published in July 2025, provides updated requirements for authentication and authenticator management.
For teams building security expertise, “https://academy.pentesthint.com/” cyber security training can provide a practical foundation for understanding authentication, authorization, and API security.
9. Apply Rate Limiting to Authentication Endpoints
Authentication endpoints are common targets for automated attacks.
An attacker may send thousands of requests against:
POST /api/loginto perform:
- Brute-force attacks
- Credential stuffing
- Password spraying
- Username enumeration
Rate limiting can reduce the effectiveness of these attacks.
For example:
5 failed attempts
        |
        v
Temporary delay
        |
        v
Additional verification
        |
        v
Security monitoring
Rate limits should be designed carefully.
Blocking only by IP address may not be enough because attackers can distribute requests across many IP addresses.
Depending on the application, rate limiting can consider:
- Account
- IP address
- Device
- API key
- Client ID
- Endpoint
- Authentication method
OWASP also recommends returning HTTP 429 Too Many Requests when API requests exceed defined limits.
10. Prevent Credential Stuffing
Credential stuffing occurs when attackers use username and password combinations leaked from another service.
For example:
user@example.com : Password123may have been exposed in an unrelated breach.
If the same credentials are reused on your application, an attacker can try them automatically.
Strong defenses include:
- MFA
- Password breach detection
- Login rate limiting
- Bot detection
- Suspicious-login monitoring
- Device and session analysis
- Password reuse prevention
Never rely on a password alone for high-risk accounts.
11. Separate Authentication From Authorization
This is one of the most important API security principles.
Imagine a user successfully authenticates and receives:
access_token = valid-tokenThe following request should not automatically succeed:
GET /api/admin/users
Authorization: Bearer valid-token
The API must also check whether the user has the required permission.
A useful mental model is:
Authentication
      |
      v
Who is the requester?
      |
      v
Authorization
      |
      v
What is the requester allowed to access?
      |
      v
Resource
This becomes especially important in multi-tenant applications.
A customer from Organization A should never be able to access Organization B’s data simply by changing an object ID.
12. Use Least Privilege and Narrow Scopes
Access tokens should provide only the permissions required for the task.
For example:
profile:readis preferable to granting:
admin:*when the application only needs to read a user’s profile.
OAuth scopes can help define these boundaries.
A payment application might use:
payments:read
payments:create
payments:refund
Different clients can receive different scopes based on their actual requirements.
This reduces the impact of compromised credentials.
13. Rotate Secrets and Credentials
Long-lived secrets increase risk.
Rotate:
- API keys
- Client secrets
- Signing keys
- Service credentials
- Certificates
- Encryption keys where appropriate
A good rotation process should allow the application to introduce a new credential before removing the old one.
For example:
Old Key
   |
   |  New Key introduced
   v
Both temporarily valid
   |
   |  Clients migrated
   v
Old Key revoked
This approach reduces downtime during credential rotation.
14. Protect Refresh Tokens
Refresh tokens can be particularly valuable because they may allow an application to obtain new access tokens.
Treat them as high-value credentials.
Good practices include:
- Store them securely
- Limit their lifetime where appropriate
- Rotate refresh tokens
- Detect reuse
- Revoke them when necessary
- Avoid exposing them unnecessarily to client-side code
For high-security environments, sender-constrained token mechanisms can provide additional protection against token theft.
For example, OAuth DPoP binds tokens to a public/private key pair, allowing the server to verify proof of possession rather than accepting possession of a bearer token alone. RFC 9449 describes this mechanism and its role in reducing token replay risk.
15. Consider Sender-Constrained Tokens for High-Risk APIs
Traditional bearer tokens work on a simple principle:
Whoever possesses the token
        =
Potentially able to use the token
This creates a problem if the token is stolen.
Sender-constrained tokens attempt to reduce this risk by requiring the client to prove possession of a cryptographic key.
DPoP is one standardized approach.
It binds an access token to a public key and requires a corresponding proof when the token is used.
This can be valuable for high-risk environments where token theft is a significant concern.
16. Never Log Passwords or Authentication Tokens
Logs are extremely valuable during incident response.
They can also become a security problem.
Avoid logging:
Authorization: Bearer eyJ...or:
password=SuperSecretPasswordAttackers who gain access to application logs may otherwise obtain valid credentials.
Instead, log security-relevant metadata such as:
User ID
Timestamp
Endpoint
Request ID
Result
Source information
Authentication failure reason
Sensitive values should be masked or excluded.
17. Return Generic Authentication Errors
Detailed authentication errors can help attackers enumerate accounts.
For example, these responses reveal useful information:
User does not existversus:
Incorrect passwordAn attacker can use the difference to determine which accounts exist.
A safer response is something like:
Invalid username or password.Internally, the application can maintain detailed security logs without exposing unnecessary information to the requester.
18. Protect Authentication Against Session Fixation and Replay
Authentication systems should generate fresh session identifiers after successful authentication.
Applications should also consider replay risks for authentication requests, tokens, and sensitive operations.
Depending on the architecture, protections may include:
- Short-lived tokens
- Nonces
- Request timestamps
- Token rotation
- TLS
- Sender-constrained tokens
- Replay detection
- Secure session management
The appropriate controls depend on the protocol and threat model.
Common API Authentication Mistakes
Even experienced developers can introduce authentication vulnerabilities through small implementation mistakes.
Common examples include:
Hardcoded API Keys
Secrets are embedded directly into source code.
Missing Token Expiration
Tokens remain valid indefinitely.
Weak JWT Validation
The application decodes JWTs without properly validating their signature and claims.
Overly Broad Permissions
A token intended for one operation receives administrative privileges.
Missing Authorization Checks
The API verifies identity but does not verify resource ownership.
No Rate Limiting
Attackers can make unlimited authentication attempts.
Sensitive Logging
Tokens, passwords, or session identifiers appear in application logs.
Insecure Client Storage
Tokens are stored where malicious scripts or applications can easily access them.
Long-Lived Credentials
Compromised credentials remain useful for an unnecessarily long period.
API Authentication From a Penetration Testing Perspective
Authentication is one of the first areas a penetration tester should examine during an API assessment.
A structured test may include:
Authentication
      |
      +-- Login controls
      |
      +-- Password policy
      |
      +-- MFA
      |
      +-- Token generation
      |
      +-- JWT validation
      |
      +-- Session management
      |
      +-- API key security
      |
      +-- Rate limiting
      |
      +-- Authorization
      |
      +-- Privilege escalation
      |
      +-- Token replay
A tester should verify whether authentication can be bypassed rather than simply checking whether a login form exists.
For example, test cases may include:
- Missing authentication headers
- Invalid tokens
- Expired tokens
- Modified JWT claims
- Incorrect signatures
- Wrong token audience
- Wrong token issuer
- Token reuse
- Weak API keys
- Excessive login attempts
- Horizontal privilege escalation
- Vertical privilege escalation
- Cross-tenant access
For controlled practice, “https://vuln.pentesthint.com/” cyber security labs can help security learners test API and web vulnerabilities in environments designed for hands-on learning.
Example of a Secure API Request
A protected API request might look like:
GET /api/v1/profile HTTP/1.1
Host: api.example.com
Authorization: Bearer ACCESS_TOKEN
Accept: application/json
The server should then perform multiple checks:
1. Is HTTPS being used?
2. Is the token present?
3. Is the token structurally valid?
4. Is the signature valid?
5. Is the token expired?
6. Is the issuer trusted?
7. Is the audience correct?
8. Does the scope allow this operation?
9. Is the requested resource accessible to this user?
10. Has the request exceeded security limits?
Only after these checks should the application return sensitive information.
API Authentication Security Checklist
Before deploying an API, review the following:
- Enforce HTTPS
- Use an authentication mechanism appropriate for the client
- Avoid sending passwords to ordinary API endpoints
- Use short-lived access tokens where appropriate
- Validate JWT signatures and security claims
- Protect API keys and secrets
- Rotate credentials
- Use MFA for sensitive accounts
- Prefer phishing-resistant MFA for high-risk users
- Apply rate limiting
- Implement brute-force and credential-stuffing defenses
- Separate authentication from authorization
- Apply least privilege
- Restrict OAuth scopes
- Protect refresh tokens
- Consider sender-constrained tokens for high-risk systems
- Avoid logging credentials and tokens
- Use generic authentication error messages
- Monitor authentication failures
- Test authentication and authorization regularly
Tools and Standards for API Security
Security teams do not need to build every control from scratch.
Useful references include the OWASP API Security Top 10, which provides a practical overview of major API security risks.
The OWASP REST Security Cheat Sheet also covers API keys, HTTP methods, rate limiting, and other REST security controls.
For identity assurance and authentication requirements, NIST’s SP 800-63B-4 is an important current reference. It was published in July 2025 and supersedes the previous SP 800-63B revision.
For OAuth implementations, the OWASP OAuth 2.0 Cheat Sheet provides practical security guidance, including token handling and client authentication.
The Future of API Authentication
API authentication is moving toward stronger identity-based and cryptographically bound mechanisms.
Traditional API keys and bearer tokens remain common, but organizations increasingly need stronger controls around machine identities, cloud workloads, service-to-service communication, and stolen-token protection.
Phishing-resistant authentication is becoming more important for human users, while mechanisms such as DPoP and mutual TLS can provide stronger protection for selected machine and API use cases.
The key trend is not simply replacing one authentication technology with another.
It is moving toward risk-based authentication, least privilege, strong identity verification, short-lived credentials, continuous monitoring, and reduced reliance on reusable secrets.
Frequently Asked Questions
What is API authentication?
API authentication is the process of verifying the identity of a user, application, device, or service before allowing access to protected API resources.
What is the most secure API authentication method?
There is no single best method for every API. OAuth 2.0/OIDC, mutual TLS, private-key-based authentication, strong MFA, and sender-constrained tokens can provide strong security when implemented correctly.
The appropriate method depends on the API architecture, client type, data sensitivity, and threat model.
Are API keys secure?
API keys can be useful for identifying clients and controlling API usage, but they should not normally be the only protection for sensitive resources. OWASP specifically recommends not relying exclusively on API keys for critical or high-value resources.
Should JWT tokens expire?
Yes. Access tokens should generally have an appropriate lifetime based on the application’s risk profile. Short-lived tokens reduce the period during which a stolen token can potentially be abused.
Is JWT authentication secure?
JWT can be secure when implemented correctly. The server must properly validate the signature, algorithm, issuer, audience, expiration, and relevant claims. Simply decoding a JWT does not establish trust.
What is the difference between authentication and authorization?
Authentication determines who the requester is.
Authorization determines what that requester is allowed to access or perform.
Both are required for a secure API.
How can APIs prevent brute-force attacks?
Use rate limiting, MFA, strong credential policies, bot detection, suspicious-login monitoring, and appropriate account protections. Rate limits should be designed so attackers cannot easily bypass them by distributing requests across multiple IP addresses.
How do penetration testers test API authentication?
Penetration testers can examine login controls, token validation, JWT implementation, API keys, session management, rate limiting, MFA, authentication bypasses, privilege escalation, token replay, and authorization boundaries.
Testing should always be performed with explicit authorization and within the agreed assessment scope.
Conclusion
Strong API authentication is more than adding an Authorization header to a request.
A secure API needs multiple layers of protection: HTTPS, strong authentication, correctly validated tokens, short-lived credentials, MFA, rate limiting, least privilege, secure secret management, proper authorization, monitoring, and regular security testing.
Developers should also remember that authentication and authorization are different controls. A valid token proves very little if the API does not verify whether the authenticated identity is actually allowed to access the requested resource.
For security teams, API authentication should be tested continuously rather than treated as a one-time development task.
Following established guidance from OWASP, NIST, CISA, and relevant OAuth standards provides a strong foundation. Teams can then adapt those controls to their own threat model and architecture.
For practical cybersecurity education, VAPT resources, and security-focused learning, “https://pentesthint.com/” PentestHint can be a useful starting point.
A secure API is not defined by one authentication technology. It is defined by how well identity, authorization, credentials, tokens, monitoring, and application logic work together.



