
Cyber Security
Remote Code Execution (RCE): How It Works & How to Prevent It
Remote Code Execution (RCE) is one of the most serious vulnerability classes in cybersecurity because it can allow an attacker to execute...
Cyber Security covers a wide range of topics related to protecting systems, applications, networks, and digital assets against cyber threats and security vulnerabilities. This category includes penetration testing, ethical hacking, vulnerability assessments, malware analysis, security awareness, incident response, and defensive security practices. Readers can explore attack methodologies, security tools, cybersecurity frameworks, exploitation techniques, and practical guidance for improving organizational security posture. The blog also shares technical tutorials, real-world case studies, security research, beginner-friendly learning content, and advanced cybersecurity concepts. Whether you are a student, IT professional, pentester, SOC analyst, or security researcher, this category provides practical and up-to-date cybersecurity knowledge.
Remote Code Execution (RCE) is one of the most serious vulnerability classes in cybersecurity because it can allow an attacker to execute...

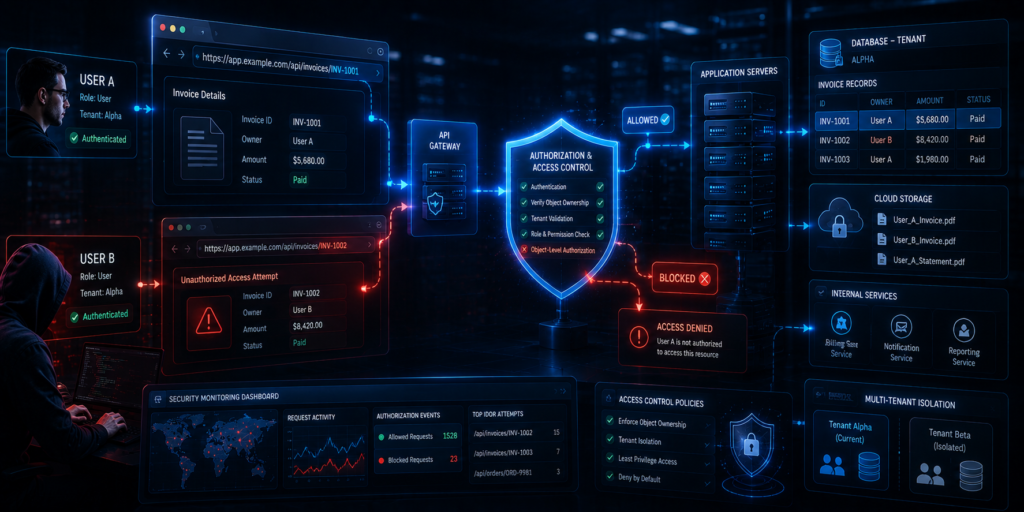
Modern web applications constantly work with objects: user profiles, invoices, documents, support tickets, orders, messages, images, and API records. These objects are...

XML External Entity (XXE) is a web application security vulnerability that occurs when an application processes untrusted XML using an insecurely configured...

Server-Side Request Forgery (SSRF) is a web application security vulnerability that allows an attacker to influence requests made by a server. Instead...
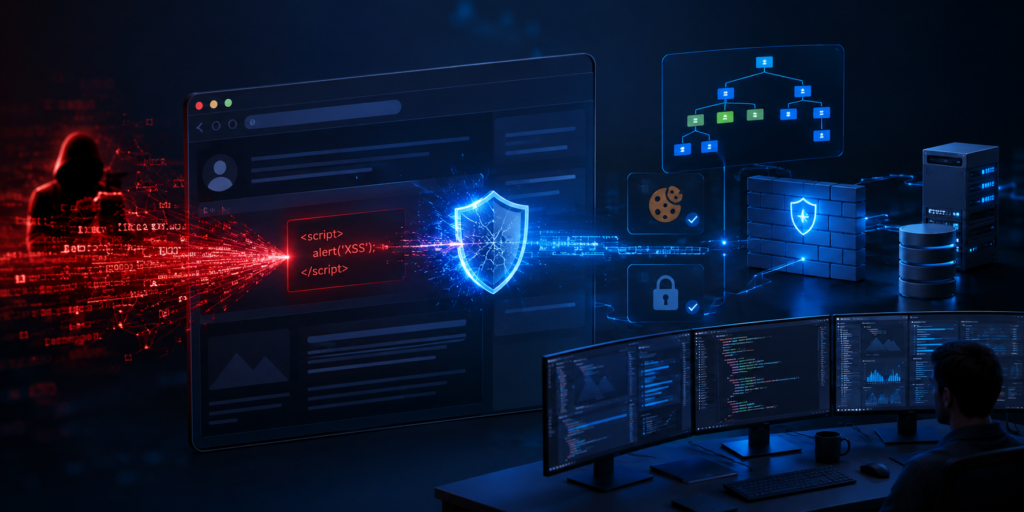
Cross-Site Scripting (XSS) is one of the most common web application security vulnerabilities. It occurs when an application allows untrusted data to...

SQL injection remains one of the most important web application security issues for developers, penetration testers, and security teams. SQL injection prevention...
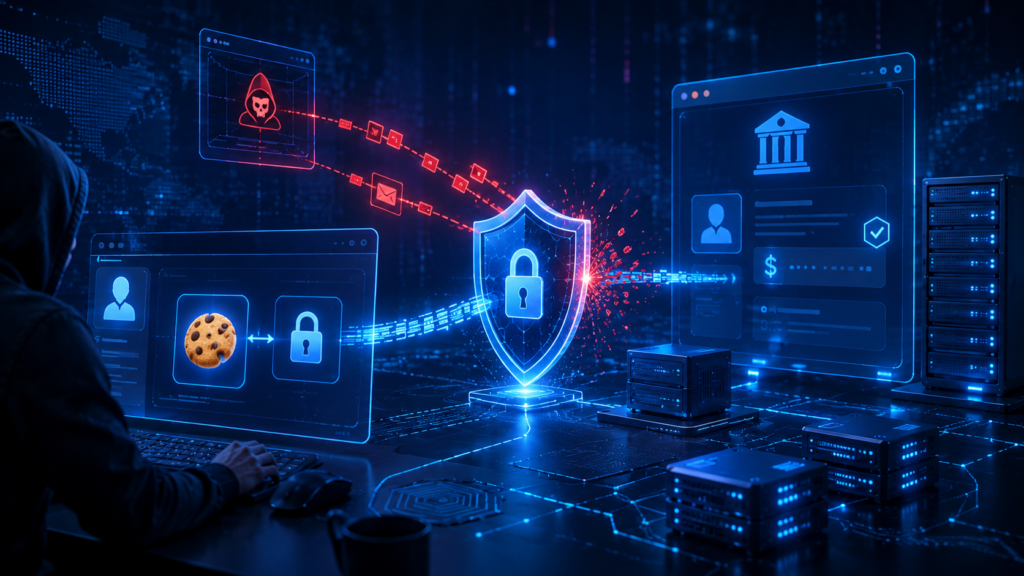
Web applications often rely on browser sessions and cookies to identify authenticated users. Once a user logs in, the browser automatically sends...

Modern web applications do much more than display information. They process payments, manage accounts, apply discounts, transfer money, approve orders, assign permissions,...

Uploading a file to a website looks simple. A user selects a document, image, PDF, or profile picture, and the application stores...
A user logs into a web application once and then moves between dashboards, profile pages, APIs, and other protected resources without entering...