Cyber Security covers a wide range of topics related to protecting systems, applications, networks, and digital assets against cyber threats and security vulnerabilities.
This category includes penetration testing, ethical hacking, vulnerability assessments, malware analysis, security awareness, incident response, and defensive security practices.
Readers can explore attack methodologies, security tools, cybersecurity frameworks, exploitation techniques, and practical guidance for improving organizational security posture.
The blog also shares technical tutorials, real-world case studies, security research, beginner-friendly learning content, and advanced cybersecurity concepts.
Whether you are a student, IT professional, pentester, SOC analyst, or security researcher, this category provides practical and up-to-date cybersecurity knowledge.
Penetration testing helps organizations identify security weaknesses before attackers can exploit them. However, even a well-planned security assessment can create operational problems...
Cybersecurity teams face a growing challenge: protecting an organization while its attack surface continues to expand. Cloud workloads, SaaS applications, remote employees,...
Data breaches, ransomware outbreaks, and supply chain compromises dominate global news cycles. In this high-stakes environment, organizations cannot rely on ad-hoc security...
An AI security checklist for organizations helps businesses identify weaknesses before they lead to data breaches, unauthorized access, financial losses, or compliance...
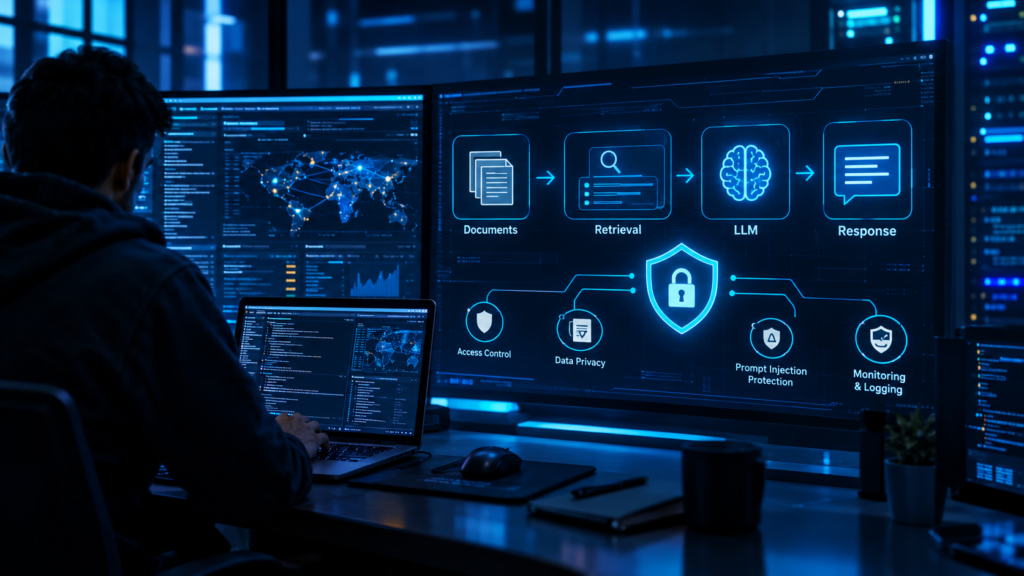
Retrieval-Augmented Generation (RAG) is becoming a common architecture for applications that need to answer questions using internal documents, enterprise knowledge bases, support...
Discovering an organization's internet-facing assets is one of the first steps in a professional security assessment. Before testing a website for vulnerabilities,...
Subdomain discovery is an important part of web application security testing. Before testing an application for vulnerabilities, a penetration tester needs to...
Web servers form the backbone of modern digital infrastructure. Whether powering customer portals, e-commerce platforms, or enterprise REST APIs, web applications are...
Network security relies heavily on robust authentication mechanisms. However, weak, default, or reused credentials remain one of the most common vectors exploited...
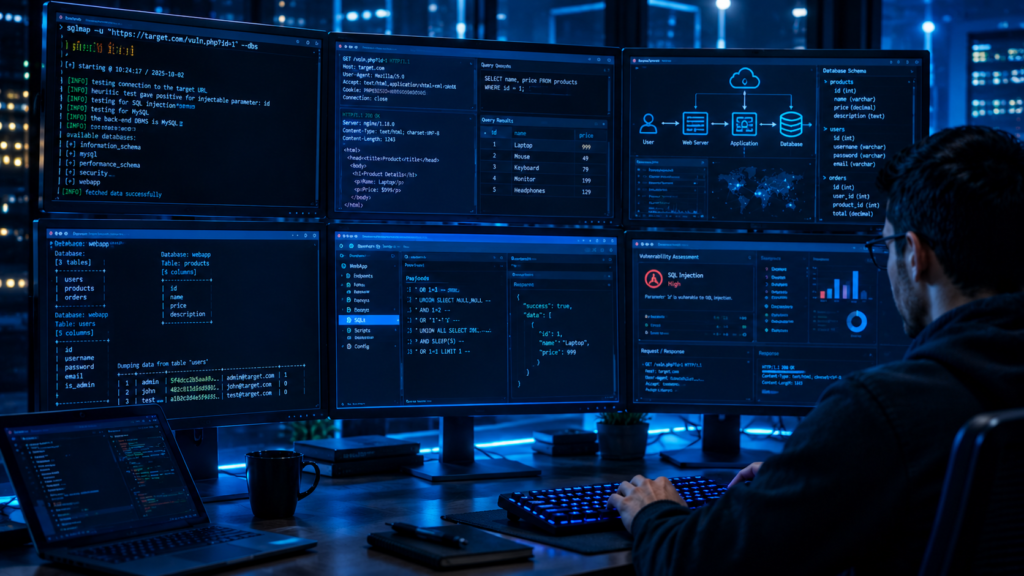
SQLMap Tutorial guides are useful for security professionals because SQL injection remains one of the most important web application vulnerabilities to understand....