
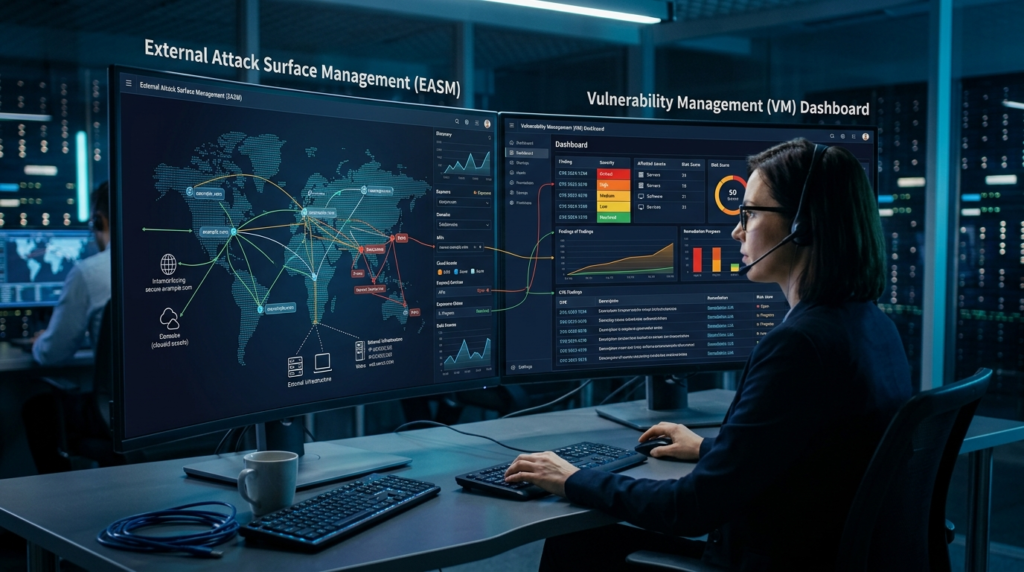
y teams understand what an external attacker could potentially discover and target.
What Does EASM Discover?
Depending on the platform and configuration, an EASM solution may identify:
- Public-facing IP addresses.
- Domains and subdomains.
- Internet-accessible web applications.
- Exposed APIs.
- Cloud infrastructure.
- Publicly accessible storage.
- Remote access services.
- Open network ports.
- Externally visible databases.
- Expired or misconfigured certificates.
- Forgotten development and testing environments.
- Potentially exposed third-party services.
For example, imagine a company operates its main website at example.com. Over several years, different teams create additional subdomains for testing, marketing, customer portals, and development.
Some of these environments may no longer be actively maintained. However, they could still be accessible from the internet.
An EASM platform can help discover these assets and identify exposures that the security team may not have included in its original asset inventory.
How Does EASM Work?
Although capabilities differ between products, an EASM workflow generally includes the following activities.
1. Asset Discovery
The platform collects information about an organization’s known and potentially related internet-facing assets. It may use domain information, DNS records, certificates, IP addresses, cloud metadata, and other external sources.
2. Asset Attribution
Discovered assets are evaluated to determine whether they are associated with the organization.
This step is important because a company may share infrastructure with hosting providers, cloud platforms, or unrelated businesses.
3. Exposure Identification
The platform examines discovered assets for externally visible security issues, such as exposed services, weak configurations, or potentially vulnerable technologies.
4. Risk Assessment
Identified exposures are evaluated according to their severity, accessibility, business relevance, and potential impact.
5. Continuous Monitoring
EASM solutions can monitor changes in the external attack surface, helping security teams identify newly exposed assets and configuration changes.
The result is a more complete understanding of what an external attacker may be able to see.
What Is Vulnerability Management?
Vulnerability Management is an ongoing security process used to identify, assess, prioritize, remediate, and verify security weaknesses in an organization’s systems and applications.
Unlike a one-time vulnerability scan, vulnerability management involves a continuous lifecycle. Security teams regularly evaluate assets, review findings, assign remediation responsibilities, and verify whether reported issues have been resolved.
A vulnerability may exist because of outdated software, insecure configurations, weak access controls, missing patches, or application coding errors.
For example, a company may run an internet-facing web server using an outdated version of a software component affected by a known Common Vulnerabilities and Exposures (CVE) entry.
A vulnerability management process can identify the affected component, evaluate the associated risk, assign remediation to the responsible team, and track the fix.
Main Activities in Vulnerability Management
1. Asset Identification
Security teams identify systems, applications, network devices, and other assets that need security assessment.
2. Vulnerability Scanning
Automated tools examine assets for known vulnerabilities, outdated software, and security misconfigurations.
3. Vulnerability Assessment
Security professionals validate findings, investigate false positives, and understand how vulnerabilities affect the environment.
4. Risk Prioritization
Findings are prioritized using factors such as CVSS severity, exploit availability, asset criticality, exposure, and business impact.
5. Remediation
The responsible teams apply patches, update software, modify configurations, or implement other security controls.
6. Verification and Retesting
Security teams perform follow-up checks to confirm whether the vulnerabilities have been successfully resolved.
This process helps organizations maintain visibility into known security weaknesses and manage remediation more effectively.
External Attack Surface Management vs Vulnerability Management: Key Differences
EASM and vulnerability management both contribute to reducing cyber risk, but their scope, objectives, and methods are different.
The simplest distinction is that EASM focuses on discovering and monitoring an organization’s external exposure, while vulnerability management focuses on identifying and managing security weaknesses in assets.
| Comparison Area | External Attack Surface Management | Vulnerability Management |
|---|---|---|
| Primary purpose | Discover and monitor external exposure | Identify and manage security vulnerabilities |
| Main focus | Internet-facing assets | Systems, applications, and infrastructure |
| Asset visibility | External digital footprint | Assets included in the assessment scope |
| Discovery | Domains, IPs, subdomains, APIs, cloud assets | Hosts, software, services, configurations |
| Testing approach | External reconnaissance and exposure analysis | Vulnerability scanning, assessment, and validation |
| Risk evaluation | External accessibility and exposure context | Vulnerability severity and business risk |
| Remediation | Reduce unnecessary external exposure | Patch, configure, or otherwise fix weaknesses |
| Monitoring | Changes to the external attack surface | Changes in vulnerability status |
| Typical users | Attack surface management and security teams | Vulnerability management and security operations teams |
| Key outcome | Better visibility of external exposure | Reduced known vulnerability risk |
1. Scope of Assessment
EASM concentrates on assets visible from the internet. Its purpose is to identify what an external party could discover about an organization.
Vulnerability management generally covers a broader range of systems, depending on the organization’s program. This can include internal servers, endpoints, databases, network equipment, cloud workloads, and applications.
2. Asset Discovery
EASM places significant emphasis on discovering unknown or unmanaged external assets.
Vulnerability management typically assesses assets already included in its inventory or scanning scope, although asset discovery features may also be available.
3. Security Objectives
EASM aims to reduce unknown and unnecessary external exposure.
Vulnerability management aims to reduce the number and impact of known security weaknesses.
4. Remediation Activities
EASM findings may lead to removing unused assets, restricting public access, correcting DNS records, securing exposed services, or reviewing third-party ownership.
Vulnerability management findings may require installing patches, updating software, changing configurations, or correcting application code.
5. Monitoring Frequency
EASM platforms often monitor external changes continuously or at regular intervals.
Vulnerability management programs use scheduled scans, continuous assessment where available, and additional testing after significant changes or remediation.
Neither approach should be treated as a substitute for the other.
Why EASM and Vulnerability Management Are Both Important
Organizations cannot effectively manage security risks if they do not understand what assets they operate or which weaknesses affect those assets.
Using only one of these approaches can leave important security gaps.
Risks of Relying Only on Vulnerability Management
A vulnerability scanner can only assess assets that it can identify and reach within its configured scope.
Consider a company that scans all registered production servers every week. Its security team receives regular reports and fixes critical vulnerabilities.
However, an old cloud instance created by a development team is not included in the asset inventory. The instance remains publicly accessible and runs outdated software.
The vulnerability management process may be working correctly within its defined scope, but the unknown asset remains exposed.
EASM can help identify this type of external asset discovery gap.
Risks of Relying Only on EASM
Now consider an organization that uses an EASM platform to monitor all known internet-facing assets.
The platform discovers its domains, public IP addresses, and web applications. It also identifies an externally accessible server.
However, discovering that server does not automatically establish whether its installed software contains a critical vulnerability.
A dedicated vulnerability assessment is needed to identify and evaluate the weakness.
This is why both practices are necessary.
Real-World Examples: How EASM and Vulnerability Management Work Together
Understanding the difference becomes easier when we examine practical scenarios.
Example 1: Forgotten Development Server
A software company previously created a development server for testing a new application.
After the project ended, the team stopped using the server but did not remove it from the cloud environment.
The server remains accessible through a public IP address.
EASM role:
- Discovers the externally accessible server.
- Identifies the associated IP address and exposed services.
- Highlights that the asset may be unmanaged or unnecessary.
- Helps the security team investigate its ownership and business purpose.
Vulnerability management role:
- Assesses the server for outdated software and known vulnerabilities.
- Identifies missing security patches.
- Prioritizes findings based on severity and exposure.
- Tracks remediation and verifies the fixes.
Outcome: The organization can remove the unnecessary server or secure it appropriately while addressing its known vulnerabilities.
Example 2: Exposed API Endpoint
A company launches a new customer-facing API. During deployment, a configuration mistake makes an administrative endpoint publicly accessible.
EASM role:
- Identifies the externally reachable API.
- Monitors the endpoint as part of the organization’s external footprint.
- Highlights unexpected exposure.
Vulnerability management role:
- Assesses the API for authentication and authorization weaknesses.
- Evaluates whether sensitive functions are accessible without appropriate permissions.
- Tracks the required security changes.
Outcome: The company restricts access to the administrative endpoint and verifies that the relevant security controls work correctly.
Example 3: Vulnerable Internet-Facing Software
An organization operates a public-facing web server running an outdated software component associated with a known CVE.
EASM role:
- Confirms that the server is externally visible.
- Provides context about its public exposure.
- Helps identify the affected external asset.
Vulnerability management role:
- Identifies the vulnerable software version.
- Evaluates the CVE and available remediation.
- Prioritizes patching based on exploitability and business impact.
- Confirms whether the vulnerability has been resolved.
Outcome: The security team can prioritize the exposed vulnerable system instead of treating it like an isolated software finding.
Common Challenges in EASM and Vulnerability Management
Both approaches can provide valuable security information, but implementation challenges can reduce their effectiveness.
1. Incomplete Asset Inventory
Organizations may have assets created by different departments, contractors, or cloud administrators.
Without accurate ownership information, security teams may struggle to determine which assets belong to the business.
Best practice: Maintain a centralized asset inventory and establish clear ownership for external systems.
2. False Positives
An EASM platform may incorrectly associate an external asset with an organization. Vulnerability scanners may also report findings that cannot be reproduced or do not apply to the installed software version.
Best practice: Validate important findings before assigning remediation tasks or making major risk decisions.
3. Alert Overload
Large environments can generate many external exposure alerts and vulnerability findings.
If teams treat every alert as equally urgent, critical issues may receive insufficient attention.
Best practice: Prioritize findings using asset importance, exposure, exploitability, and business impact.
4. Limited Remediation Ownership
Security teams may discover problems but lack the authority or resources to fix them.
For example, a security team may identify an exposed cloud service, but the service could be managed by a separate development or infrastructure team.
Best practice: Assign clear remediation owners, deadlines, escalation paths, and verification responsibilities.
5. Third-Party Exposure
Businesses depend on cloud providers, SaaS platforms, vendors, and external service providers.
Some externally visible assets may belong to third parties or be hosted on shared infrastructure.
Best practice: Verify asset ownership and contractual responsibilities before attempting changes or remediation.
6. Lack of Continuous Monitoring
A secure external environment can change quickly when teams deploy new services, create cloud resources, or modify network configurations.
Similarly, newly disclosed vulnerabilities can affect previously assessed assets.
Best practice: Combine regular asset discovery with ongoing vulnerability assessment and monitoring.
Tools Used for External Attack Surface Management
Different EASM platforms offer different discovery, monitoring, attribution, and risk analysis capabilities.
Commonly used solutions include:
1. Microsoft Defender External Attack Surface Management
Microsoft Defender External Attack Surface Management helps organizations discover and monitor internet-facing assets associated with their business.
It provides visibility into external infrastructure and can help identify assets that may not be included in traditional asset inventories.
Official resource: https://www.microsoft.com/en-us/security/business/endpoint-security/microsoft-defender-external-attack-surface-management
2. Palo Alto Networks Cortex Xpanse
Cortex Xpanse focuses on discovering internet-facing assets and identifying external exposures.
It can help security teams understand their public attack surface and investigate potentially unmanaged or exposed infrastructure.
Official website: https://www.paloaltonetworks.com/
3. Censys
Censys provides internet-wide asset discovery and visibility into externally observable hosts, services, and certificates.
Security teams can use its capabilities to investigate exposed infrastructure and understand how assets appear from the public internet.
Official website: https://censys.com/
4. Rapid7 Surface Command
Rapid7 Surface Command provides external attack surface visibility and helps organizations identify internet-facing assets and exposures.
It can support asset discovery and external risk investigation.
Official website: https://www.rapid7.com/
Tools Used for Vulnerability Management
Vulnerability management tools help security teams identify, assess, prioritize, and track weaknesses across their environments.
1. Tenable Nessus
Nessus is widely used for vulnerability scanning and security assessment.
It can identify known vulnerabilities, missing patches, and configuration issues across supported systems.
Official website: https://www.tenable.com/products/nessus
2. Qualys VMDR
Qualys Vulnerability Management, Detection and Response (VMDR) provides capabilities for asset discovery, vulnerability assessment, prioritization, and remediation workflows.
Official website: https://www.qualys.com/apps/vulnerability-management-detection-response/
3. Rapid7 InsightVM
InsightVM helps organizations identify vulnerabilities, assess risk, and manage remediation activities across their environments.
Official website: https://www.rapid7.com/products/insightvm/
4. Greenbone OpenVAS
Greenbone’s OpenVAS technology supports vulnerability scanning and assessment.
It is commonly used by security professionals to identify known weaknesses in systems and network services.
Official website: https://www.greenbone.net/
5. Nmap
Nmap is a network discovery and security auditing tool. Although it is not a complete vulnerability management platform, it is useful for identifying hosts, open ports, and running services during authorized assessments.
Official website: https://nmap.org/
How to Integrate EASM With Vulnerability Management
Organizations can achieve better security visibility by connecting external asset discovery with vulnerability assessment and remediation workflows.
A practical integration process can follow these steps.
Step 1: Discover External Assets
Use an EASM solution to identify internet-facing domains, IP addresses, applications, APIs, and cloud resources.
Review discovered assets and determine whether they belong to the organization.
Step 2: Verify Asset Ownership
Assign each confirmed asset to a responsible department, application owner, or infrastructure team.
This prevents security findings from remaining unresolved because nobody knows who manages the affected resource.
Step 3: Assess Discovered Assets for Vulnerabilities
Bring relevant assets into the vulnerability management process.
Perform authorized vulnerability scans and additional manual validation where required.
Step 4: Correlate Exposure and Vulnerability Data
Combine information from both processes.
For example, an externally accessible server with a known critical vulnerability may require more urgent attention than an isolated vulnerability on a restricted internal test system.
Consider:
- Internet accessibility.
- Vulnerability severity.
- Exploit availability.
- Known active exploitation.
- Asset criticality.
- Data sensitivity.
- Business impact.
CVSS can help describe vulnerability severity, while the CISA Known Exploited Vulnerabilities (KEV) Catalog can help identify vulnerabilities known to be exploited in the wild.
Useful references:
- NIST National Vulnerability Database: https://nvd.nist.gov/
- CISA KEV Catalog: https://www.cisa.gov/known-exploited-vulnerabilities-catalog
- FIRST EPSS: https://www.first.org/epss/
Step 5: Prioritize Remediation
Create remediation tasks based on risk rather than relying only on the number of findings or their severity labels.
A critical vulnerability on a publicly exposed business-critical application may deserve immediate attention.
A lower-severity issue on an isolated development system may follow a different remediation timeline.
Step 6: Verify Remediation
After the responsible team implements a fix, perform appropriate validation.
Confirm that the external exposure has been removed or restricted and that the reported vulnerability is no longer reproducible.
Update the asset inventory and vulnerability records with the verification result.
EASM vs Vulnerability Management: Which One Should Your Organization Choose?
The decision depends on the organization’s security requirements, asset visibility, and existing security processes.
However, choosing one does not eliminate the need for the other.
EASM may be the immediate priority when:
- The organization has limited visibility into internet-facing assets.
- Multiple cloud environments are in use.
- New domains and subdomains are frequently created.
- Unknown or unmanaged external assets are a concern.
- The business depends heavily on public-facing applications and APIs.
Vulnerability Management may be the immediate priority when:
- The organization already maintains a reliable asset inventory.
- Regular vulnerability scans are required.
- Security teams need structured remediation tracking.
- Patch management needs improvement.
- Known vulnerabilities are not being resolved within acceptable timelines.
For mature security programs: Integrating both practices provides a stronger approach. EASM helps identify the external assets that need attention, while vulnerability management helps determine which known weaknesses require remediation.
Best Practices for EASM and Vulnerability Management
To get meaningful results from both approaches, organizations should follow a consistent security process.
- Maintain accurate asset inventories: Keep records of domains, IP addresses, applications, cloud services, and asset owners.
- Monitor external changes: Review newly discovered assets, exposed services, and configuration changes.
- Validate important findings: Investigate suspected exposures and vulnerabilities before treating them as confirmed security issues.
- Prioritize based on business risk: Consider exploitability, exposure, asset criticality, and potential impact.
- Establish remediation ownership: Assign clear responsibilities and realistic remediation deadlines.
- Integrate security tools: Connect discovery, vulnerability assessment, ticketing, and reporting workflows where practical.
- Verify remediation: Confirm that security fixes work instead of relying only on task completion updates.
- Review third-party exposure: Understand which external services are owned by the organization and which are managed by vendors.
- Track security metrics: Measure asset coverage, critical exposure, remediation time, overdue findings, and recurring vulnerabilities.
- Improve continuously: Reassess the external attack surface and vulnerability management process as the business environment changes.
Security professionals who want to build practical assessment skills can explore cyber security labs and learn cyber security through structured learning resources.
Frequently Asked Questions (FAQs)
1. What is the main difference between EASM and vulnerability management?
External Attack Surface Management focuses on discovering and monitoring an organization’s internet-facing assets and exposures. Vulnerability management focuses on identifying, prioritizing, remediating, and verifying security weaknesses across systems and applications.
2. Is EASM a type of vulnerability management?
No. EASM and vulnerability management are related but distinct security practices. EASM focuses on external asset visibility and exposure, while vulnerability management manages security weaknesses. Some commercial platforms combine capabilities from both areas.
3. Can EASM replace vulnerability scanning?
No. EASM can identify external assets and certain exposures, but it does not necessarily provide the depth of vulnerability assessment offered by dedicated vulnerability scanning and validation tools. Organizations should use appropriate vulnerability assessment methods to investigate discovered assets.
4. What types of assets does EASM discover?
Depending on the platform, EASM can discover public IP addresses, domains, subdomains, web applications, APIs, cloud resources, exposed services, certificates, and other internet-facing assets associated with an organization.
5. Which tools are used for External Attack Surface Management?
Common EASM solutions include Microsoft Defender External Attack Surface Management, Palo Alto Networks Cortex Xpanse, Censys, and Rapid7 Surface Command. Their discovery and monitoring capabilities vary.
6. Which tools are commonly used for vulnerability management?
Popular vulnerability management solutions include Tenable Nessus, Qualys VMDR, Rapid7 InsightVM, and Greenbone OpenVAS. Nmap is also useful for network discovery and security auditing.
7. How does EASM help prevent cyberattacks?
EASM helps organizations discover externally visible assets and identify exposures that may otherwise remain unnoticed. By improving asset visibility and supporting timely remediation, it can reduce opportunities for attackers to target forgotten or misconfigured systems.
8. Should small businesses use EASM and vulnerability management?
Yes, although the implementation should match the organization’s size, infrastructure, and risk level. Small businesses can begin with an accurate asset inventory, regular vulnerability assessments, external exposure reviews, and clear remediation responsibilities. They can expand to dedicated EASM platforms as their external environment grows.
Conclusion
External Attack Surface Management and Vulnerability Management address two connected but different areas of cybersecurity.
EASM helps organizations understand what is exposed to the internet, including forgotten domains, cloud resources, APIs, and publicly accessible services. Vulnerability management identifies and manages the security weaknesses that may affect those assets.
Using only one approach can leave important gaps. An organization may scan its known systems regularly but miss an unmanaged external server. Another organization may discover its entire external footprint but fail to identify vulnerable software running on those assets.
Combining EASM with vulnerability management creates a more complete security process: discover external assets, verify ownership, assess vulnerabilities, prioritize risk, remediate weaknesses, and validate the results.
At PentestHint, we aim to help cybersecurity professionals strengthen their knowledge of vulnerability assessment, penetration testing, and modern security practices. Explore our resources to develop practical skills and understand how organizations identify and manage real-world security risks.
Remember: You cannot protect every asset effectively if you do not know it exists, and discovering an exposed asset is only the first step toward securing it.



