
Cyber Security
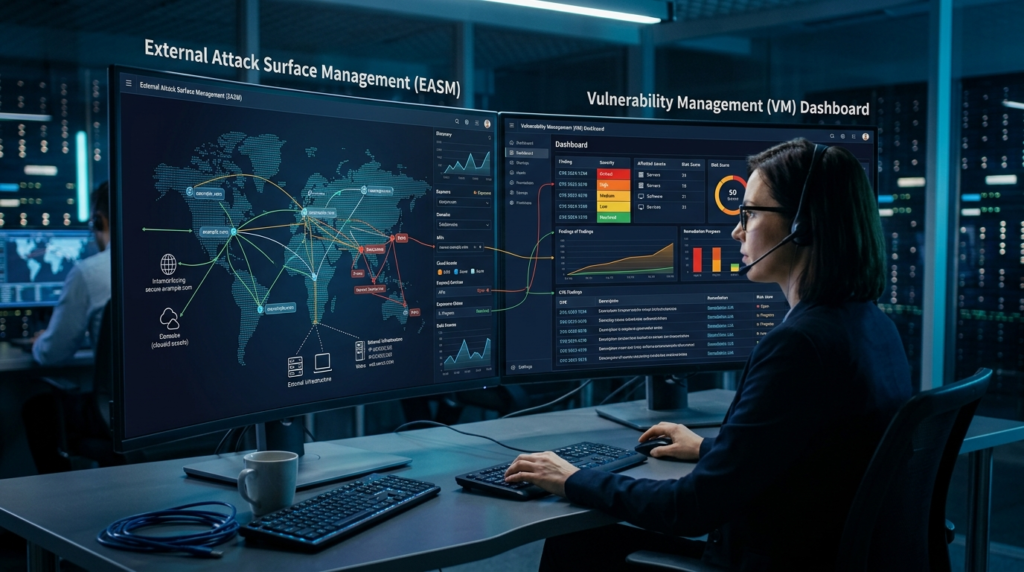
External Attack Surface Management vs Vulnerability Management
y teams understand what an external attacker could potentially discover and target. What Does EASM Discover? Depending on the platform and configuration,...
y teams understand what an external attacker could potentially discover and target. What Does EASM Discover? Depending on the platform and configuration,...
Vulnerability management is a critical part of every organization's cybersecurity strategy. Security teams regularly use automated scanners to identify weaknesses across networks,...
Penetration testing helps organizations identify security weaknesses before attackers can exploit them. However, even a well-planned security assessment can create operational problems...
Data breaches, ransomware outbreaks, and supply chain compromises dominate global news cycles. In this high-stakes environment, organizations cannot rely on ad-hoc security...
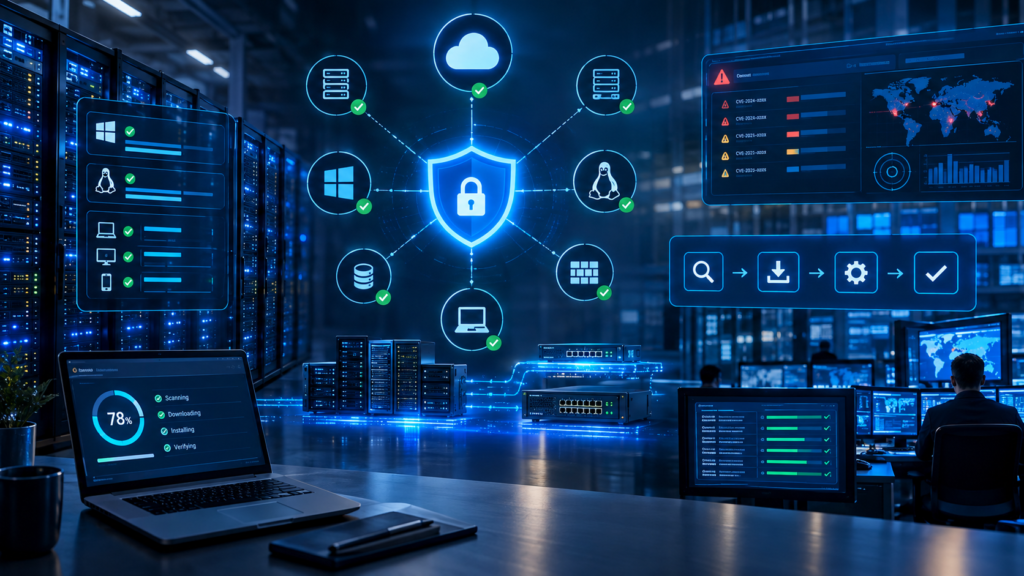
Patch management best practices are essential for keeping modern IT environments secure, stable, and resilient. Every operating system, application, server, endpoint, network...
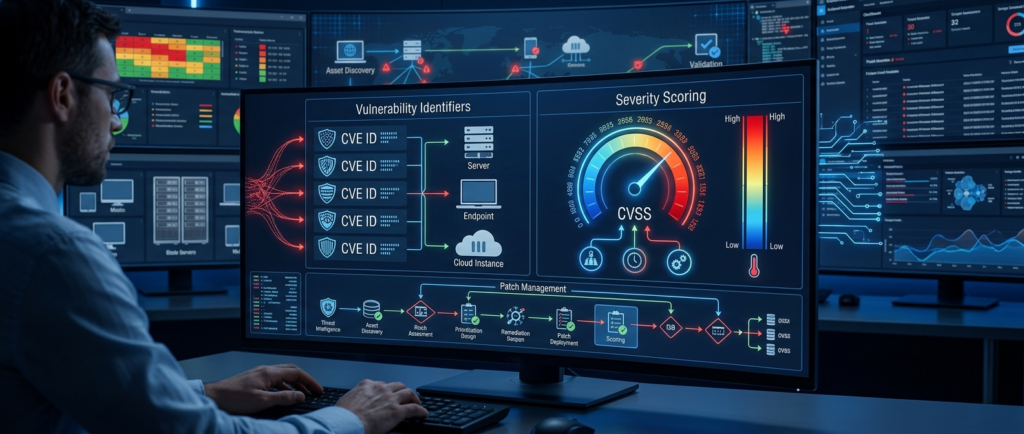
Modern organizations deal with thousands of software vulnerabilities across operating systems, applications, cloud services, network devices, libraries, and third-party components. Two terms...

The vulnerability management lifecycle is a continuous security process used to identify, assess, prioritize, remediate, and verify security weaknesses across an organization's...
Preparing for a major compliance audit often feels like getting ready for a strict building inspection. You can paint the walls and...

Securing venture capital or angel investment is one of the most critical milestones for a growing technology startup. Founders spend months refining...

Cyber security is no longer limited to firewalls, antivirus solutions, or penetration testing. Modern organizations now focus heavily on policies, compliance, business...