
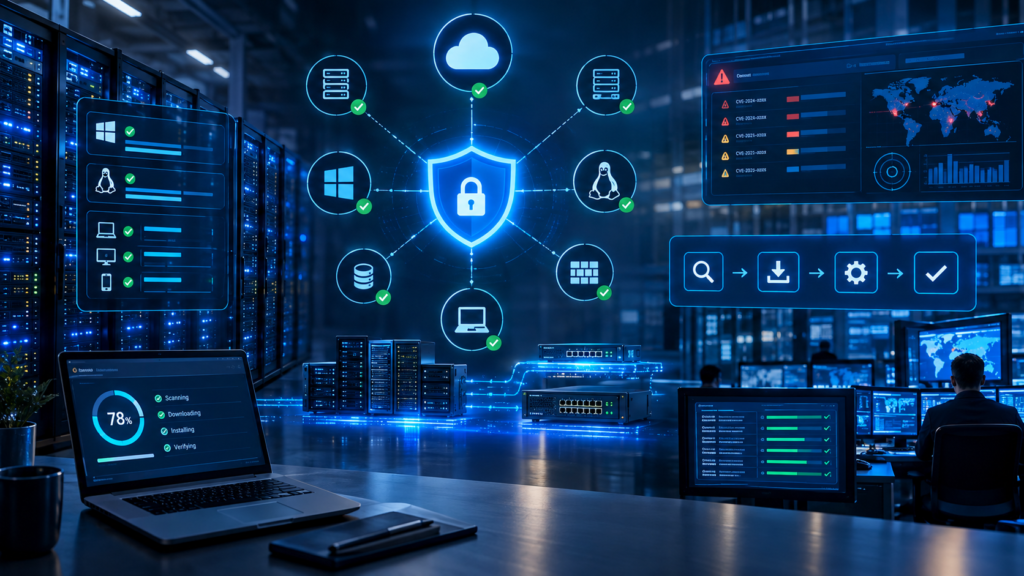
Patch management best practices are essential for keeping modern IT environments secure, stable, and resilient. Every operating system, application, server, endpoint, network device, cloud workload, and firmware component can contain vulnerabilities. Once attackers discover an exploitable weakness, an unpatched system can quickly become an entry point into the organization.
Patching is not simply a matter of clicking an “Update” button. Enterprise patch management involves discovering assets, identifying vulnerabilities, prioritizing updates, testing patches, deploying them, and verifying that remediation was successful. NIST describes patch management as a form of preventive maintenance and recommends an enterprise-wide strategy rather than an isolated IT task.
The challenge becomes greater as organizations adopt hybrid infrastructure, cloud services, remote endpoints, containers, third-party applications, and internet-facing systems. Security teams must therefore balance security risk with availability, compatibility, and business requirements.
A well-designed patch management program reduces the attack surface while giving security and IT teams a repeatable process for responding to vulnerabilities.
What Is Patch Management?
Patch management is the structured process of identifying, evaluating, acquiring, testing, deploying, and verifying software and firmware updates.
A patch can fix several types of problems, including:
- Security vulnerabilities
- Software bugs
- Performance issues
- Stability problems
- Compatibility issues
- Configuration weaknesses
- Operating system defects
Security patches are particularly important because attackers frequently target publicly known vulnerabilities in operating systems, applications, appliances, and other technologies.
For example, imagine an organization running an outdated web server. A vulnerability is publicly disclosed that allows remote code execution. If the organization delays patching, an attacker may exploit the vulnerability to execute commands on the server, steal credentials, deploy malware, or move deeper into the internal network.
Patch management helps prevent this situation by turning vulnerability remediation into a controlled and measurable process.
Why Patch Management Is Important
A large percentage of successful attacks do not necessarily depend on previously unknown vulnerabilities. Attackers can also exploit weaknesses for which security updates already exist but have not been deployed.
This makes patch management one of the most practical forms of preventive cybersecurity.
NIST’s current enterprise patch management guidance emphasizes that organizations should treat patching as an ongoing business and risk-management process rather than an occasional technical activity.
Reduces the Attack Surface
Every unpatched system represents potential exposure.
Removing known vulnerabilities reduces the number of weaknesses attackers can exploit during reconnaissance and initial access.
Helps Prevent Data Breaches
A compromised endpoint or server can become a pathway to sensitive information. Timely patching reduces the likelihood that known vulnerabilities will be used to gain unauthorized access.
Protects Internet-Facing Systems
Public-facing applications, VPN gateways, firewalls, remote-access systems, web servers, and email infrastructure are particularly important because attackers can often reach them directly from the internet.
Supports Compliance
Many security frameworks and regulatory programs expect organizations to maintain vulnerability and configuration management processes. A documented patching program also provides useful evidence during security assessments and audits.
Improves System Stability
Not every patch is purely security-related. Vendors regularly release updates that fix bugs, improve compatibility, and resolve reliability problems.
Common Types of Patches
Organizations should understand the different types of updates they may encounter.
Security Patches
These address vulnerabilities that could be exploited by attackers.
Security patches should generally receive higher priority than ordinary feature updates, especially when exploitation is active.
Critical Updates
Critical updates address serious defects that may cause significant security or operational consequences.
The exact classification varies between vendors, so organizations should combine vendor severity with their own environmental risk.
Bug Fixes
Bug-fix releases address software defects that may not directly create security vulnerabilities but can affect reliability or functionality.
Feature Updates
Feature updates introduce new functionality or significant product changes. They should still be evaluated for security and compatibility implications.
Firmware Updates
Firmware exists in devices such as routers, firewalls, servers, storage systems, printers, IoT devices, and network appliances.
Firmware vulnerabilities can be particularly dangerous because these devices often provide privileged access to infrastructure.
Patch Management Lifecycle
A mature patch management program should follow a repeatable lifecycle.
1. Asset Discovery
You cannot patch what you do not know exists.
Maintain an accurate inventory of:
- Workstations
- Laptops
- Servers
- Virtual machines
- Network appliances
- Cloud resources
- Applications
- Databases
- Containers
- Firmware
- IoT devices
- Mobile devices
Asset discovery should also identify software versions and operating system versions.
This is especially important in large environments where shadow IT, temporary cloud workloads, and unmanaged endpoints can easily be overlooked.
2. Vulnerability Identification
The next step is determining which assets contain vulnerabilities.
Organizations can use:
- Vulnerability scanners
- Endpoint management platforms
- Software inventory systems
- Vendor security advisories
- CVE databases
- Threat intelligence
- Security monitoring platforms
Security teams should correlate vulnerabilities with the actual assets running the affected software.
A vulnerability in an unused internal test server may have a very different risk profile from the same vulnerability on an internet-facing production server.
3. Prioritize Patches
Patching everything immediately is often unrealistic.
Instead, prioritize vulnerabilities based on risk.
Important factors include:
- Severity
- Exploit availability
- Active exploitation
- Internet exposure
- Asset criticality
- Data sensitivity
- Business impact
- Availability of compensating controls
- Ease of exploitation
- Existing threat activity
CISA recommends prioritizing vulnerabilities known to be exploited in the wild and maintaining rapid-response processes for actively exploited vulnerabilities.
This means a medium-severity vulnerability that attackers are actively exploiting may deserve faster remediation than a higher-severity issue with no known exploitation and strong network controls.
4. Test the Patch
Testing helps identify unexpected problems before deployment across the production environment.
A typical process can include:
- Apply the patch to a test system.
- Verify the application starts normally.
- Test critical business functions.
- Check integrations.
- Monitor logs and performance.
- Validate security controls.
- Approve the deployment.
Organizations with critical applications should maintain representative test environments where practical.
5. Deploy in Phases
Avoid deploying a major patch to every system simultaneously unless the risk justifies it.
A phased approach may look like:
Pilot group → IT systems → Low-risk production → Critical production
This provides an opportunity to detect compatibility problems before they affect the entire organization.
6. Verify Installation
Deployment does not automatically mean remediation was successful.
After patching, verify:
- Installed software version
- Patch status
- Reboot status
- Vulnerability scanner results
- Endpoint management status
- Application functionality
- Relevant system logs
NIST specifically includes verification as part of the enterprise patch management process.
7. Document Exceptions
Some systems cannot be patched immediately.
Examples include:
- Legacy applications
- Unsupported operating systems
- Industrial control systems
- Systems requiring vendor certification
- Business-critical applications with strict availability requirements
An exception should never simply mean “we cannot patch it.”
Document:
- The affected asset
- Vulnerability
- Reason for delay
- Business owner
- Security owner
- Compensating controls
- Planned remediation date
- Approval
CISA guidance also recognizes that when immediate patching is not possible, organizations may use measures such as isolation, access restrictions, service disabling, firewall controls, or increased monitoring until a patch can be safely applied.
Patch Management Best Practices
Maintain an Accurate Asset Inventory
Asset inventory is the foundation of patch management.
Security teams should know what devices and applications exist, who owns them, where they are located, what software versions they run, and whether they are supported.
An incomplete inventory creates blind spots that attackers can exploit.
Prioritize Known Exploited Vulnerabilities
Do not rely only on CVSS scores.
CVSS can help measure technical severity, but real-world exploitation should strongly influence remediation priority.
A vulnerability that is actively being exploited against organizations represents an immediate threat.
CISA’s Known Exploited Vulnerabilities approach is particularly useful for identifying vulnerabilities that attackers are known to exploit.
Establish Clear Patch SLAs
Define remediation targets based on severity and business risk.
For example:
| Risk Level | Example Target |
|---|---|
| Actively exploited critical vulnerability | Immediate / emergency |
| Critical vulnerability | 7 days |
| High-risk vulnerability | 14 days |
| Medium-risk vulnerability | 30 days |
| Low-risk vulnerability | 60–90 days |
These numbers should be adapted to the organization’s risk tolerance and operational requirements rather than treated as universal rules.
Automate Where Possible
Manual patching does not scale effectively.
Automation can help with:
- Software inventory
- Patch detection
- Update deployment
- Reboots
- Compliance reporting
- Vulnerability verification
- Failed-patch detection
Automation should still include safeguards such as testing, staged deployment, rollback procedures, and monitoring.
Separate Emergency Patching From Routine Patching
Not every patch requires an emergency response.
Routine patches can follow a predictable maintenance schedule.
Emergency patches should have a separate process for situations involving:
- Active exploitation
- Internet-facing critical vulnerabilities
- Security incidents
- High-impact zero-day vulnerabilities
- Vendor emergency advisories
This allows security teams to respond quickly without disrupting normal operational processes.
Use Compensating Controls
When immediate patching is impossible, reduce exposure using temporary controls.
Examples include:
- Network segmentation
- Firewall restrictions
- Access control changes
- Disabling vulnerable services
- Removing internet exposure
- Application isolation
- Increased monitoring
These controls reduce risk but should not become a permanent substitute for patching when a secure update is available.
Monitor Failed Patches
A failed patch is a security problem that can easily disappear inside a dashboard.
Track:
- Failed installations
- Offline endpoints
- Devices requiring reboot
- Unsupported systems
- Patch conflicts
- Systems missing management agents
- Repeated deployment failures
Security teams should investigate recurring failures rather than continuously retrying the same deployment.
Protect the Patch Management Infrastructure
Patch management systems themselves are highly privileged.
If an attacker compromises the patch management server or endpoint management platform, they may gain the ability to distribute malicious software across the organization.
Protect management infrastructure with:
- Strong authentication
- Least privilege
- Network segmentation
- Administrative access controls
- MFA
- Logging
- Change monitoring
- Secure backups
Patch Third-Party Applications
Organizations often focus on Windows or Linux updates while overlooking applications.
Common examples include:
- Web browsers
- PDF readers
- Java runtimes
- VPN clients
- Database software
- Remote-access tools
- Development frameworks
- Collaboration applications
- Security products
Third-party software should be included in the organization’s software inventory and patch lifecycle.
Do Not Ignore Cloud and Containers
Cloud infrastructure does not eliminate patch management.
Organizations may still need to maintain:
- Virtual machines
- Container images
- Kubernetes nodes
- Operating systems
- Cloud agents
- Application dependencies
- Self-managed databases
- Network appliances
For containerized environments, rebuilding images from updated base images is often preferable to manually modifying running containers.
Patch Management Tools
Different environments require different tools.
Endpoint Management Platforms
Endpoint management solutions can help organizations discover devices, deploy updates, enforce policies, and monitor compliance.
Examples include Microsoft Intune, Microsoft Configuration Manager, and other enterprise endpoint management platforms.
Vulnerability Scanners
Vulnerability scanners help identify outdated software and known vulnerabilities.
They can provide useful information such as:
- CVE identifiers
- Affected hosts
- Installed versions
- Severity
- Remediation guidance
Software Composition Analysis
Modern applications depend heavily on open-source libraries.
Software composition analysis tools can identify vulnerable dependencies inside applications and container images.
Configuration Management
Configuration management platforms can automate system configuration and software deployment across large fleets.
Patch Management and Vulnerability Management
Patch management and vulnerability management are closely related, but they are not identical.
Vulnerability management focuses on identifying, assessing, prioritizing, and remediating security weaknesses.
Patch management focuses specifically on obtaining, testing, deploying, and verifying updates and fixes.
A vulnerability management platform may identify a vulnerable package, while the patch management system actually deploys the appropriate update.
Together, these processes create a stronger remediation workflow.
Measuring Patch Management Performance
Organizations should measure patching instead of relying on assumptions.
Useful metrics include:
Patch Compliance Rate
Percentage of managed assets successfully patched within the required timeframe.
Mean Time to Remediate
Average time between vulnerability identification and successful remediation.
Critical Vulnerability Exposure
Number of critical vulnerabilities remaining unresolved.
Known Exploited Vulnerabilities
Track how many actively exploited vulnerabilities remain in the environment.
Failed Deployment Rate
Percentage of patch deployments that fail and require manual intervention.
Asset Coverage
Percentage of organizational assets included in the patch management system.
These metrics help security leaders identify gaps and demonstrate improvement over time.
Real-World Patch Management Scenario
Consider a company with 2,000 employee laptops and 150 servers.
A critical vulnerability is announced in a widely deployed enterprise application.
The security team first identifies all systems running the affected version. The vulnerability is then checked against threat intelligence and known exploitation information.
Internet-facing systems receive the highest priority.
The IT team tests the update on a representative group of machines before deploying it to a larger pilot group. After successful testing, the update is rolled out in phases.
Security scanners are then used to verify that the vulnerable version has disappeared.
A small number of systems fail because they are offline. Those devices are placed into a remediation queue, and their owners are notified.
This approach is much more effective than sending a generic email asking employees to update their software.
Common Patch Management Mistakes
Patching Without Asset Inventory
Unknown devices cannot be reliably patched.
Treating Every Vulnerability Equally
Risk-based prioritization is more effective than simply sorting vulnerabilities by severity.
Skipping Verification
A deployment report saying “successful” should not be the only evidence that remediation worked.
Ignoring Legacy Systems
Unsupported systems often require additional controls and replacement planning.
Relying Entirely on Manual Processes
Manual workflows become increasingly unreliable as environments grow.
Delaying Actively Exploited Vulnerabilities
When attackers are already exploiting a vulnerability, extended patch cycles can create unnecessary exposure.
Failing to Document Exceptions
Unpatched systems should have an owner, justification, compensating controls, and remediation plan.
How Patch Management Supports Penetration Testing
Patch management is also relevant during penetration tests and vulnerability assessments.
A penetration tester may discover:
- Outdated web servers
- Missing operating system updates
- Vulnerable third-party software
- Unsupported applications
- Exposed management interfaces
- Vulnerable firmware
- Outdated libraries
These findings can reveal weaknesses in the organization’s patch management process.
After remediation, security teams can perform validation testing to confirm that the vulnerable software is no longer exposed.
Organizations looking to strengthen their practical skills can also use “https://vuln.pentesthint.com/” hands-on labs and “https://vuln.pentesthint.com/“vulnerability labs to practice vulnerability identification and remediation workflows.
Building a Patch Management Policy
A formal patch management policy should define:
- Asset ownership
- Software inventory requirements
- Vulnerability assessment procedures
- Patch prioritization criteria
- Testing requirements
- Deployment schedules
- Emergency patching procedures
- Exception handling
- Verification procedures
- Reporting requirements
- Compliance targets
- Responsibilities and escalation paths
NIST recommends developing an enterprise strategy that brings technology, security, leadership, and business stakeholders into the patch management process.
A strong policy prevents patching from becoming an informal responsibility that falls between different teams.
Future of Patch Management
Patch management is becoming increasingly automated.
Modern environments can combine asset inventory, vulnerability intelligence, endpoint management, cloud security, threat intelligence, and automated remediation.
Organizations are also moving toward risk-based remediation rather than simply attempting to maintain a perfect patch score.
The future of patch management will likely focus more heavily on:
- Automated asset discovery
- Continuous vulnerability assessment
- Risk-based prioritization
- Cloud workload security
- Container image updates
- Software supply chain security
- Automated remediation
- Threat intelligence integration
- Continuous compliance monitoring
However, automation does not remove the need for human oversight. Security teams still need to understand business criticality, operational risk, exceptions, and the potential impact of changes.
Frequently Asked Questions
What is patch management in cybersecurity?
Patch management is the process of identifying, prioritizing, testing, deploying, and verifying updates for operating systems, applications, firmware, and other technologies to reduce security and operational risk.
Why is patch management important?
Patch management reduces exposure to known vulnerabilities and helps organizations prevent attackers from exploiting outdated software and systems.
How often should organizations patch systems?
There is no single schedule suitable for every organization. Routine updates may follow scheduled maintenance windows, while actively exploited or critical vulnerabilities may require emergency remediation.
Should all vulnerabilities be patched immediately?
Not necessarily. Organizations should prioritize vulnerabilities based on factors such as exploitation, severity, asset exposure, business criticality, and available mitigations.
What is the difference between patch management and vulnerability management?
Vulnerability management covers the broader process of discovering, assessing, prioritizing, and remediating vulnerabilities. Patch management specifically focuses on obtaining, deploying, and verifying updates and fixes.
What should organizations do if a system cannot be patched?
Organizations should document the exception and apply appropriate compensating controls such as network isolation, access restrictions, service disabling, firewall rules, or enhanced monitoring. The system should also have a plan for permanent remediation.
Can patch management be automated?
Yes. Organizations can automate asset discovery, patch detection, deployment, reboot management, reporting, and remediation verification. Critical environments should still use testing and staged deployment before broad automation.
What are the most important patch management metrics?
Useful metrics include patch compliance, mean time to remediate, critical vulnerability exposure, known exploited vulnerabilities, failed deployment rate, and the percentage of assets covered by the patch management program.
Conclusion
Patch management is one of the most practical defenses against known cybersecurity vulnerabilities. A mature program goes far beyond installing updates. It combines accurate asset inventory, vulnerability intelligence, risk-based prioritization, testing, controlled deployment, verification, exception management, and continuous measurement.
Organizations should pay particular attention to internet-facing systems and vulnerabilities that are actively exploited. When immediate patching is impossible, temporary controls can reduce exposure, but they should support—not replace—long-term remediation. CISA specifically recommends rapid remediation of actively exploited vulnerabilities and using mitigations when patches cannot be applied immediately.
For security teams, patch management should become part of normal operational security rather than an occasional emergency activity. Organizations that build a repeatable process can reduce attack surface, improve visibility, and respond faster when new vulnerabilities emerge.
For additional security resources, practical learning, and professional services, explore “https://pentesthint.com/” PentestHint and its broader “https://pentesthint.com/” cyber security services.



