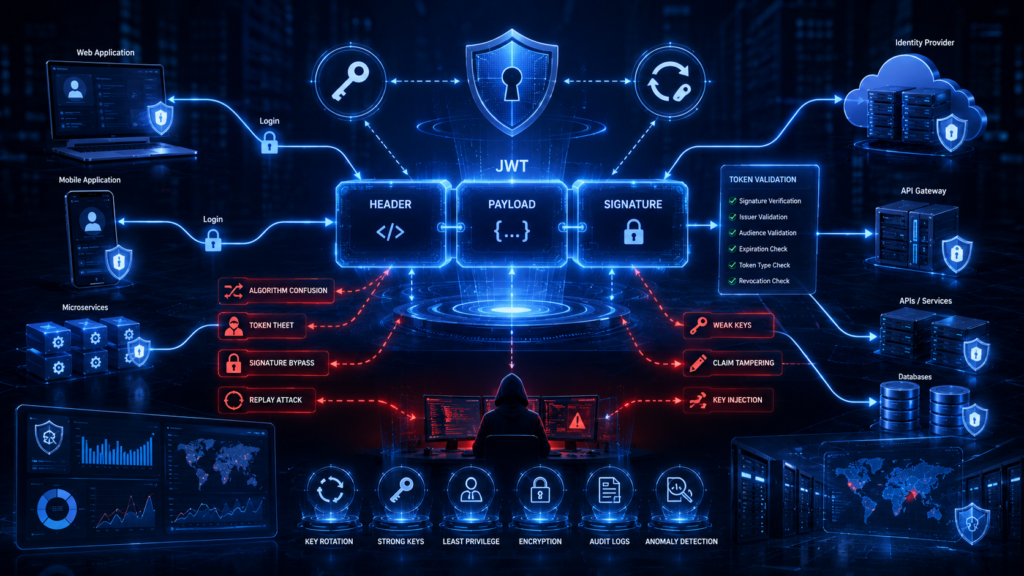
JWT Security Best Practices: Secure JSON Web Token Implementation
JSON Web Tokens are widely used to carry authentication and authorization information between applications, APIs, identity providers, and microservices. Because JWTs can...
OAuth 2.0 has become one of the most widely used authorization frameworks for modern web applications, APIs, mobile applications, and cloud services....
REST APIs are now a core part of modern software. Web applications, mobile applications, cloud platforms, SaaS products, payment systems, and microservices...
APIs have become the backbone of modern applications. Mobile apps, SaaS platforms, payment systems, cloud services, microservices, and third-party integrations all depend...
XML External Entity (XXE) is a web application security vulnerability that occurs when an application processes untrusted XML using an insecurely configured...
Cross-Site Scripting (XSS) is one of the most common web application security vulnerabilities. It occurs when an application allows untrusted data to...
SQL injection remains one of the most important web application security issues for developers, penetration testers, and security teams. SQL injection prevention...
Application Programming Interfaces (APIs) form the underlying backbone of modern digital infrastructure. They connect mobile apps to cloud services, enable microservices architectures,...
Modern web applications power everything from global finance to daily healthcare management. However, as applications grow more complex, they also open new...
As organizations accelerate their digital transformation, defending corporate networks, applications, and cloud environments becomes increasingly complex. Cybercriminals continuously refine their attack methods,...