Mobile applications have become a primary interface for banking, e-commerce, healthcare, social media, enterprise services, and digital payments. As more sensitive operations move to smartphones, attackers increasingly target not only the mobile application itself but also the APIs, authentication systems, local storage, and third-party services behind it.
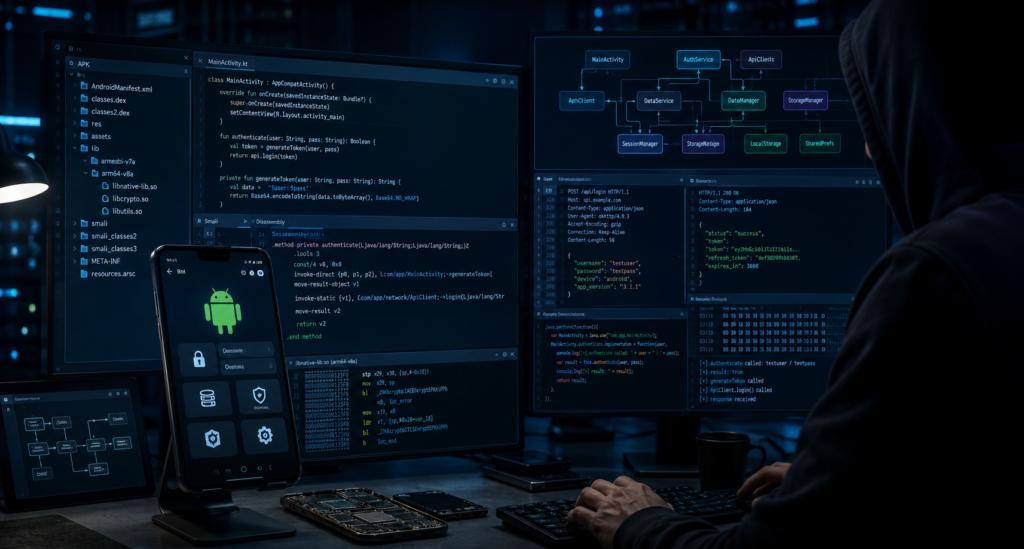
A mobile application security checklist helps penetration testers and developers assess these attack surfaces systematically. Instead of checking only whether an APK or IPA works correctly, security testing examines what happens when an attacker modifies requests, extracts application data, tampers with the binary, abuses permissions, or interacts directly with backend APIs.
The mobile security landscape is also evolving. OWASP’s Mobile Application Security Verification Standard (MASVS) remains an industry standard for assessing mobile applications and covers storage, cryptography, authentication, network communication, platform interaction, code quality, resilience, and privacy.
In August 2026, OWASP also released MASWE 1.0.0, providing a stable catalog of mobile application security weaknesses and strengthening the relationship between high-level MASVS controls and concrete testing findings.
This guide provides a practical mobile application security checklist that can be used during Android and iOS security assessments.
What Is Mobile Application Security Testing?
Mobile application security testing is the process of evaluating a mobile application for vulnerabilities that could compromise user accounts, sensitive information, application functionality, backend services, or the device itself.
Testing normally covers two major areas:
- Client-side security
- Backend and API security
The client-side assessment examines the application installed on the device. The backend assessment examines the APIs and services used by the application.
For example, an Android application may securely store a user’s token, but the API could still contain a broken authorization vulnerability.
Likewise, an API can be properly secured while the mobile application stores sensitive credentials in an insecure local database.
A complete assessment therefore needs to consider the entire mobile ecosystem.
Why Mobile Application Security Testing Is Important
Mobile applications often handle extremely sensitive information.
Examples include:
- Authentication tokens
- Personal information
- Payment information
- Private messages
- Location information
- Health-related information
- Business documents
- API credentials
- Session information
- Biometric authentication state
A compromised application can expose information even when the underlying mobile operating system is secure.
Android, for example, provides application sandboxing, permission controls, cryptographic APIs, and other security mechanisms. Developers still need to use those mechanisms correctly.
The same principle applies to iOS. Platform security features reduce risk, but application-specific vulnerabilities can still expose data or backend functionality.
For organizations, mobile application security should therefore be part of the software development lifecycle rather than a final step before release.
Mobile Application Security Checklist
1. Application Reconnaissance
Start by understanding the application before attempting exploitation.
For Android, collect the APK or relevant testing build.
For iOS, obtain an authorized application build suitable for testing.
Document:
- Application name
- Version
- Package or bundle identifier
- Supported operating systems
- Backend domains
- API endpoints
- Authentication mechanisms
- Third-party SDKs
- Permissions
- Deep links
- Universal Links
- Application components
- Security-sensitive functionality
Reconnaissance Checklist
- Identify application version.
- Identify package/bundle identifier.
- Identify backend domains.
- Identify API endpoints.
- Identify authentication methods.
- Identify third-party services.
- Identify application permissions.
- Identify deep links.
- Identify exported Android components.
- Identify iOS URL schemes.
- Identify WebView usage.
- Identify sensitive application functionality.
Documentation, store listings, application traffic, source code where available, and static analysis can all provide useful information during this phase.
2. Static Application Analysis
Static analysis examines the application without executing it.
For Android, testers can inspect:
AndroidManifest.xml- Activities
- Services
- Broadcast receivers
- Content providers
- Resources
- Strings
- Embedded URLs
- Configuration files
- Native libraries
- Cryptographic implementations
For iOS, examine:
- Application metadata
- Entitlements
- Property lists
- Embedded frameworks
- URL schemes
- Native libraries
- Configuration
- Embedded resources
The goal is to understand how the application is constructed and identify security-sensitive functionality.
Static Analysis Checklist
- Search for hardcoded secrets.
- Search for API keys.
- Search for URLs.
- Search for credentials.
- Review cryptographic implementations.
- Review exported components.
- Review permissions.
- Review third-party libraries.
- Review debug configurations.
- Review insecure logging.
- Review embedded certificates.
- Review application configuration.
Never assume a secret is safe simply because it is hidden inside compiled application code.
A mobile application distributed to users must be treated as potentially observable by an attacker.
3. Hardcoded Credentials and Secrets
One of the first things to investigate is whether developers accidentally embedded secrets into the application.
Search for:
- API keys
- Cloud credentials
- Private keys
- Passwords
- Client secrets
- Authentication tokens
- Internal URLs
- Database credentials
- Signing information
Android’s current security guidance specifically warns developers not to commit API keys into source code and recommends stronger key-management approaches such as Android Keystore.
A hardcoded API key may not always be directly exploitable. Its impact depends on what permissions the key provides and whether the backend restricts its usage.
The important question is:
What can an attacker do if this value is extracted from the application?
4. Insecure Data Storage
Mobile applications frequently store information locally to improve performance or provide offline functionality.
Possible storage locations include:
- SQLite databases
- SharedPreferences
- XML files
- JSON files
- Local databases
- Cache files
- Logs
- Temporary files
- Application preferences
- Keychain
- Android Keystore
- iOS secure storage mechanisms
Test whether sensitive information is stored unnecessarily or without appropriate protection.
Data Storage Checklist
- Check authentication tokens.
- Check refresh tokens.
- Check passwords.
- Check personal information.
- Check payment-related information.
- Check application logs.
- Check cached responses.
- Check temporary files.
- Check database files.
- Check backups.
- Check screenshots and clipboard exposure.
- Verify sensitive data is protected using platform security mechanisms.
Android recommends minimizing the storage and transmission of sensitive data and using appropriate platform mechanisms for protected information.
For iOS, sensitive credentials should similarly use platform-provided secure storage rather than ordinary application files.
5. Authentication Testing
Authentication determines whether a user is genuinely who they claim to be.
Test the complete authentication lifecycle.
Authentication Checklist
- Test login.
- Test logout.
- Test registration.
- Test password reset.
- Test account recovery.
- Test OTP verification.
- Test biometric authentication.
- Test session expiration.
- Test token expiration.
- Test token revocation.
- Test concurrent sessions.
- Test account lockout.
- Test authentication bypass.
- Test rate limiting.
Modern Android guidance recommends modern authentication mechanisms such as passkeys and Credential Manager, with biometrics being useful for sensitive applications.
However, biometric authentication should not be treated as a replacement for secure server-side authorization.
A mobile application can display a biometric prompt locally, but the backend must still correctly determine whether the requested operation is authorized.
6. Authorization Testing
Authentication and authorization are different.
A user may successfully authenticate but still be unauthorized to perform certain actions.
Test:
- User-to-user access
- User-to-admin access
- Access to other users’ objects
- Privileged API operations
- Account modification
- Payment operations
- Administrative functionality
For example:
User A → /api/profile/1001If User A changes the identifier to:
/api/profile/1002the backend should verify whether User A is authorized to access that resource.
Do not rely on the mobile application’s interface to enforce authorization.
Security controls must exist on the backend.
7. API Security Testing
Most modern mobile applications depend heavily on APIs.
The mobile application is often just the client.
The API performs operations such as:
Login
Profile management
Payments
Messaging
File uploads
Search
Account settings
Password changes
API Testing Checklist
- Identify API endpoints.
- Test authentication.
- Test authorization.
- Test BOLA.
- Test privilege escalation.
- Test parameter manipulation.
- Test rate limiting.
- Test input validation.
- Test excessive data exposure.
- Test business logic.
- Test deprecated API versions.
- Test API error handling.
For deeper API testing, use the API security testing checklist as a separate reference within your assessment methodology.
8. Network Security Testing
Mobile applications communicate with remote services constantly.
Test whether sensitive information is transmitted securely.
Network Checklist
- Verify HTTPS.
- Check TLS configuration.
- Check certificate validation.
- Check hostname validation.
- Test cleartext traffic.
- Inspect redirects.
- Check sensitive data in requests.
- Check sensitive data in responses.
- Review API authentication headers.
- Test certificate pinning where appropriate.
- Check third-party connections.
Android’s security recommendations explicitly emphasize HTTPS and protected network communication for application traffic.
A common testing mistake is to focus only on whether HTTPS appears in the URL.
The tester should also verify whether the application properly validates certificates and hostnames and whether sensitive information is unintentionally transmitted through insecure channels.
9. Certificate Validation and Pinning
Certificate pinning can provide an additional defense against certain man-in-the-middle scenarios.
During testing, determine:
- Whether certificate validation works correctly.
- Whether hostname validation is enforced.
- Whether the application accepts unexpected certificates.
- Whether sensitive endpoints use stronger transport controls.
- Whether certificate pinning, if implemented, behaves as intended.
Pinning should not be considered a universal solution.
Poorly implemented pinning can cause availability problems, and transport security still needs correct server-side configuration.
10. WebView Security
Many applications embed web content using WebView.
This creates another attack surface.
Test:
- JavaScript configuration.
- Allowed domains.
- URL handling.
- JavaScript interfaces.
- Local file access.
- Mixed content.
- External navigation.
- Sensitive data exposure.
- Web-to-native communication.
Android’s security guidance specifically warns that untrusted JavaScript and poorly controlled JavaScript interfaces can introduce security problems.
If a WebView loads attacker-controlled content and has access to powerful native interfaces, the impact can be significantly higher.
11. Deep Links and URL Schemes
Deep links allow users to open application functionality through URLs.
Examples include:
myapp://profile/1001or HTTPS-based app links.
Test whether an attacker can manipulate parameters to:
- Access another user’s content
- Bypass authentication
- Trigger privileged functions
- Open malicious URLs
- Inject unexpected data
- Expose sensitive information
Deep Link Checklist
- Identify custom URL schemes.
- Identify Android App Links.
- Identify iOS Universal Links.
- Test unauthenticated access.
- Test parameter manipulation.
- Test malicious URLs.
- Test redirect behavior.
- Verify authorization after deep-link navigation.
Never assume that a deep link is safe simply because it is launched through the operating system.
The application must validate the data it receives.
12. Android Component Security
Android applications contain components such as:
- Activities
- Services
- Broadcast receivers
- Content providers
Improperly exposed components can allow other applications to interact with functionality that was intended to remain private.
Android Checklist
- Review exported activities.
- Review exported services.
- Review broadcast receivers.
- Review content providers.
- Review intent filters.
- Review custom permissions.
- Test unauthorized IPC.
- Test malicious intents.
- Test content-provider access.
Android recommends using explicit intents where appropriate, particularly for services, because implicit service interactions can introduce security risks.
13. iOS Platform Security
For iOS assessments, examine how the application uses platform security mechanisms.
Review:
- Keychain usage
- App Transport Security
- Entitlements
- URL schemes
- Universal Links
- Pasteboard usage
- Background functionality
- Local authentication
- Data protection
- Push notification handling
The objective is to determine whether sensitive operations rely correctly on platform security controls.
14. Cryptography Testing
Applications often use cryptography to protect local or transmitted information.
Test:
- Identify cryptographic algorithms.
- Check key generation.
- Check key storage.
- Check random number generation.
- Check encryption modes.
- Check IV/nonce handling.
- Check hardcoded keys.
- Check password hashing.
- Check certificate handling.
- Check deprecated algorithms.
Avoid implementing custom cryptographic algorithms unless there is a compelling and reviewed reason.
Use well-tested platform and cryptographic libraries.
The OWASP MASVS includes a dedicated cryptography control group, MASVS-CRYPTO, covering cryptographic functionality used to protect sensitive data.
15. Permission Testing
Mobile applications request access to sensitive device capabilities.
Examples include:
- Camera
- Microphone
- Contacts
- Location
- Storage
- Bluetooth
- Notifications
- Phone-related functionality
Check whether the application requests only the permissions it genuinely needs.
Permission Checklist
- Identify requested permissions.
- Identify dangerous permissions.
- Check runtime permission handling.
- Test denied permissions.
- Test revoked permissions.
- Check whether functionality fails securely.
- Verify third-party SDK permissions.
- Check unnecessary background access.
Excessive permissions increase the potential impact of application compromise.
16. Reverse Engineering and Tampering
Mobile applications are distributed to users, which means attackers can obtain and inspect their binaries.
Test how easily an attacker can:
- Decompile the application
- Understand application logic
- Extract strings
- Identify endpoints
- Modify application behavior
- Repackage the application
- Bypass client-side restrictions
OWASP MASVS includes a dedicated resilience category covering resistance to reverse engineering and tampering.
The important distinction is that obfuscation and anti-tampering controls are defense-in-depth measures.
They should never replace server-side authorization.
If the application hides an administrator button but the backend still accepts the administrative request from an ordinary user, the application remains vulnerable.
17. Root and Jailbreak Detection
Some applications attempt to detect compromised devices.
During testing, evaluate:
- Whether detection exists.
- Whether detection can be bypassed.
- Whether sensitive functionality depends entirely on it.
- Whether the backend independently enforces authorization.
Root or jailbreak detection can increase resistance against certain attacks, but it should not be treated as a primary security boundary.
Security-critical decisions should remain enforceable by trusted backend systems.
18. Logging and Sensitive Information Exposure
Application logs can unintentionally reveal secrets.
Search logs for:
- Passwords
- Access tokens
- Refresh tokens
- API keys
- Personal information
- Session identifiers
- Internal URLs
- Debug messages
Also check crash reports and analytics systems.
A developer may remove sensitive information from the visible UI while leaving it in debug logs.
This can create a significant privacy problem.
19. Third-Party SDK and Supply Chain Testing
Mobile applications frequently depend on third-party SDKs for:
- Analytics
- Advertising
- Authentication
- Payments
- Crash reporting
- Social login
- Push notifications
- Maps
- Customer support
These components increase the application’s attack surface.
OWASP’s current MASVS guidance highlights SDKs as an important part of the mobile application ecosystem and notes the scale of third-party code used in modern applications.
SDK Checklist
- Identify third-party SDKs.
- Check SDK versions.
- Identify known vulnerabilities.
- Review permissions.
- Review data collection.
- Review network communication.
- Review SDK configuration.
- Remove unnecessary dependencies.
- Monitor dependency updates.
Third-party libraries should be treated as part of the application’s security boundary.
20. Input Validation
Mobile applications receive data from many sources:
- User input
- Network responses
- Deep links
- Files
- IPC
- WebViews
- External applications
Every one of these sources should be treated as potentially untrusted.
OWASP MASVS explicitly requires applications to validate and sanitize untrusted inputs to reduce the risk of injection and security-control bypasses.
Test:
- Form inputs.
- API responses.
- Deep-link parameters.
- File names.
- Imported files.
- WebView input.
- IPC data.
- Serialized objects.
21. Session Management
Session handling is one of the most important areas of mobile security testing.
Check:
- Token expiration.
- Refresh token handling.
- Logout behavior.
- Token revocation.
- Multiple sessions.
- Password change invalidation.
- Account recovery.
- Device removal.
- Session fixation.
- Token storage.
A logout button is not enough.
After logout, verify whether previously issued credentials can still access protected resources.
22. Privacy Testing
Privacy should be considered independently from traditional vulnerability testing.
Review:
- What data the application collects.
- Why it collects the data.
- Where the data is stored.
- Which third parties receive the data.
- Whether data is transmitted unnecessarily.
- Whether analytics contain sensitive information.
- Whether users can delete or control relevant information.
The current OWASP MASVS includes privacy as its own control group, MASVS-PRIVACY.
23. Error Handling
Application errors can reveal useful information to attackers.
Look for:
- Stack traces
- API endpoints
- Internal hostnames
- Database errors
- File paths
- Debug information
- Framework versions
- Sensitive identifiers
A production application should return useful errors without exposing internal implementation details.
24. Secure Update Mechanism
Mobile applications need a reliable update process.
Test:
- Update integrity.
- Signature validation.
- Version enforcement where appropriate.
- Deprecated version handling.
- Dependency updates.
- Emergency update capability.
- Secure distribution channels.
Android’s security guidance recommends keeping source code, dependencies, SDKs, and related components up to date to reduce exposure to known vulnerabilities.
Mobile Application Security Testing Tools
A professional mobile security assessment usually requires several tools rather than a single scanner.
Static Analysis Tools
Common options include:
- MobSF
- jadx
- apktool
- Ghidra
- strings
- semgrep
These tools help identify application structure, secrets, endpoints, libraries, and potentially dangerous code patterns.
Dynamic Analysis Tools
Common tools include:
- Burp Suite
- Frida
- Objection
- Android Debug Bridge
- LLDB
- Drozer for applicable legacy scenarios
Dynamic analysis allows testers to observe application behavior while it is running.
Network Testing
Burp Suite is particularly useful for analyzing:
- API requests
- Authentication flows
- Headers
- Tokens
- Request parameters
- Response data
- TLS behavior
Always perform interception and modification testing only against applications and environments for which you have authorization.
Mobile Security Standards
OWASP MASVS should be one of the primary references for a structured assessment. The OWASP Mobile Application Security project also provides MASTG for testing techniques and MASWE for mobile security weaknesses.
The current MASVS control groups include:
- MASVS-STORAGE
- MASVS-CRYPTO
- MASVS-AUTH
- MASVS-NETWORK
- MASVS-PLATFORM
- MASVS-CODE
- MASVS-RESILIENCE
- MASVS-PRIVACY
Complete Mobile Application Security Checklist
Use this condensed checklist during an authorized assessment.
Reconnaissance
- Identify application version.
- Identify package/bundle ID.
- Identify backend services.
- Identify API endpoints.
- Identify third-party SDKs.
- Identify permissions.
- Identify deep links.
Static Analysis
- Search for hardcoded secrets.
- Review application configuration.
- Review permissions.
- Review exported components.
- Review third-party libraries.
- Review cryptography.
- Review embedded URLs.
Authentication
- Test login.
- Test logout.
- Test registration.
- Test password reset.
- Test OTP.
- Test biometric authentication.
- Test session expiration.
- Test token revocation.
Authorization
- Test BOLA.
- Test privilege escalation.
- Test administrative functions.
- Test object ownership.
- Test backend authorization.
Storage
- Check local databases.
- Check preferences.
- Check cache.
- Check logs.
- Check temporary files.
- Check backups.
- Check tokens and credentials.
Network
- Verify HTTPS.
- Test TLS validation.
- Test certificate validation.
- Test sensitive data transmission.
- Test third-party connections.
- Review API authentication.
Platform
- Test Android components.
- Test intents.
- Test content providers.
- Test deep links.
- Test iOS URL schemes.
- Review entitlements.
- Review permissions.
Code and Resilience
- Test reverse engineering resistance.
- Check obfuscation.
- Test tampering controls.
- Check debug configuration.
- Check native libraries.
- Check outdated dependencies.
Privacy
- Review collected data.
- Review analytics.
- Review third-party sharing.
- Review local storage.
- Review permissions.
- Check unnecessary data collection.
Common Mobile Application Security Testing Mistakes
Testing Only the Mobile Client
A mobile application is rarely the entire system.
If you test only the APK or IPA, you may miss serious backend vulnerabilities.
Always evaluate the APIs and backend authorization model.
Trusting Client-Side Controls
Hiding a button is not authorization.
Disabling a feature in the interface is not authorization.
Blocking an operation inside the mobile client is not authorization.
The backend must enforce security-critical decisions.
Ignoring Local Storage
Attackers with access to a device, backup, debugging environment, or compromised runtime may be able to inspect application data.
Always review local storage and caching behavior.
Ignoring Third-Party SDKs
A vulnerable SDK can introduce risks even when the application’s own code appears secure.
Maintain a current software bill of materials and monitor dependencies.
Relying Only on Automated Scanners
Automated tools are useful for finding common problems, but they cannot fully understand business logic, authorization relationships, privacy requirements, or application-specific workflows.
Manual analysis remains essential.
Mobile Application Security Best Practices
Developers and security teams can reduce risk by following a few core principles.
Minimize Sensitive Data
Do not store or transmit information unless the application actually needs it.
Use Platform Security Features
Use Android and iOS security mechanisms instead of creating custom security controls whenever practical.
Protect Authentication Tokens
Use appropriate secure storage and limit token lifetime and permissions.
Enforce Authorization Server-Side
Never rely on client-side checks for sensitive operations.
Encrypt Sensitive Data
Use established cryptographic libraries and secure key-management mechanisms.
Secure Network Communication
Use HTTPS and correctly validate certificates and hostnames.
Keep Dependencies Updated
Third-party libraries can introduce vulnerabilities that attackers may exploit.
Test Before Release
Security testing should happen during development and before major releases rather than only after an incident.
For teams looking to build practical security skills, cyber security training and hands-on labs can complement formal mobile security methodology with practical exercises.
Career Opportunities in Mobile Application Security
Mobile application security is a specialized area within application security and penetration testing.
Professionals with mobile security skills can pursue roles such as:
- Mobile Application Security Tester
- Android Security Researcher
- iOS Security Researcher
- Application Security Engineer
- Mobile Penetration Tester
- VAPT Analyst
- Security Consultant
- Bug Bounty Researcher
- Red Team Operator
A strong mobile security professional should understand more than APK analysis.
Important skills include:
- HTTP and APIs
- Android internals
- iOS security
- Authentication
- Cryptography
- Secure storage
- Reverse engineering
- Network security
- Application architecture
- Backend authorization
- Secure coding
Hands-on practice is particularly valuable because mobile security involves both application-level and platform-level concepts.
Future of Mobile Application Security
Mobile applications are becoming increasingly integrated with cloud services, AI-powered features, digital identity systems, payments, wearables, and third-party platforms.
This creates a larger security boundary.
Modern mobile security testing will increasingly need to consider:
- API-driven architectures
- Supply-chain security
- Third-party SDKs
- Privacy engineering
- Device integrity
- Application attestation
- Passkeys
- Hardware-backed key storage
- Runtime protection
- Cloud-connected mobile applications
OWASP’s ongoing Mobile Application Security work reflects this broader approach. MASVS now covers not only traditional storage and network controls but also resilience and privacy, while MASWE provides a structured weakness taxonomy.
FAQ
What is a mobile application security checklist?
A mobile application security checklist is a structured list of security tests used to assess Android and iOS applications. It typically covers authentication, authorization, local storage, APIs, network communication, cryptography, permissions, platform interaction, reverse engineering, privacy, and third-party components.
What should I test first in a mobile application?
Start with reconnaissance. Identify the application version, backend APIs, authentication mechanisms, permissions, third-party SDKs, deep links, and sensitive functionality. Then move into static analysis, dynamic testing, authentication, authorization, and data-storage testing.
What is the OWASP MASVS?
OWASP MASVS, or Mobile Application Security Verification Standard, is an industry standard for mobile application security. It provides security controls covering areas such as storage, cryptography, authentication, network communication, platform interaction, code, resilience, and privacy.
Which tools are used for mobile application penetration testing?
Common tools include MobSF, Burp Suite, Frida, Objection, jadx, apktool, Ghidra, ADB, and platform-specific debugging tools. The appropriate toolset depends on whether the assessment involves static analysis, dynamic analysis, network testing, reverse engineering, or API testing.
Is certificate pinning required for every mobile application?
Not necessarily. Certificate pinning can provide additional protection in some threat models, but it should be implemented carefully. Correct TLS configuration and certificate validation remain fundamental.
Can a mobile application be secure if its API is vulnerable?
No. A mobile client can have excellent local security controls while still exposing users to serious risk through a vulnerable backend API. Authentication and authorization must be enforced on trusted server-side systems.
What is the difference between static and dynamic mobile security testing?
Static testing examines application files and code without running the application. Dynamic testing examines application behavior while it executes, including network traffic, authentication flows, storage, runtime behavior, and interactions with the operating system.
Is mobile application security testing only for Android?
No. Mobile security testing applies to Android, iOS, cross-platform applications, hybrid applications, and applications that depend heavily on mobile SDKs and backend services. OWASP MASVS is designed to apply across native, cross-platform, and hybrid mobile applications.
Conclusion
A mobile application security assessment should never be limited to checking whether an APK or IPA contains obvious secrets.
Modern applications are ecosystems consisting of mobile clients, APIs, authentication systems, cloud infrastructure, third-party SDKs, local storage, platform services, and external integrations.
A strong mobile application security checklist should therefore cover the complete attack surface.
Start with reconnaissance and static analysis. Then test authentication, authorization, APIs, network communication, local storage, cryptography, WebViews, deep links, platform components, permissions, third-party dependencies, reverse engineering, privacy, and session management.
Use OWASP MASVS as the security baseline and MASTG and MASWE to support detailed testing and weakness classification. OWASP describes MASVS as an industry standard and provides the wider Mobile Application Security project as a framework for consistent mobile security verification.
For developers, security should be built into the application from the beginning. For penetration testers, the objective should be to understand how the application behaves when trusted assumptions are removed.
A secure mobile application is not simply one that hides its code or passes an automated scan.
It is an application where sensitive data is protected, authentication and authorization are correctly enforced, untrusted input is handled safely, APIs resist abuse, platform capabilities are used securely, and security decisions cannot be bypassed by modifying the client.
For organizations that need professional security assessment support, VAPT services and security consulting can help identify weaknesses before attackers do.