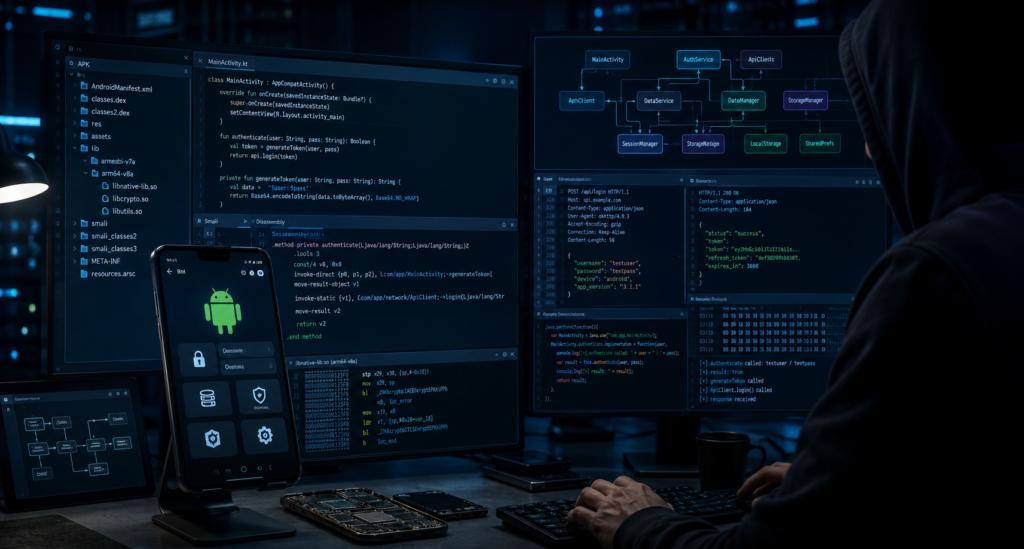
Reverse engineering Android applications is an important skill in mobile application security. It allows security researchers and penetration testers to understand how an application works internally, identify security weaknesses, inspect application logic, and validate whether security controls actually protect sensitive functionality.
Android provides a relatively accessible environment for application analysis. An APK contains resources, application metadata, compiled code, and often native libraries that can be examined with the right tools. OWASP’s Mobile Application Security Testing Guide (MASTG) specifically includes techniques for Android reverse engineering, including Java decompilation, Smali disassembly, native-code analysis, string extraction, and runtime analysis.
Reverse engineering is not limited to security research. Developers can use the same techniques to investigate unexpected application behavior, validate their own security controls, and understand how third-party components interact with an application.
For penetration testers, the real value comes from combining reverse engineering with dynamic analysis and API testing. Looking at the code can reveal where a security decision is made, while runtime testing can determine whether that decision can actually be bypassed.
What Is Reverse Engineering Android Applications?
Reverse engineering is the process of analyzing a compiled application to understand its internal structure, logic, resources, and runtime behavior.
Android applications are commonly distributed as APKs or as sets of APKs generated from Android App Bundles. An APK is essentially an archive containing application resources and compiled components.
Depending on the application, a researcher may encounter:
- Java or Kotlin application code
- DEX bytecode
- Smali representation
- Native ARM or ARM64 libraries
- XML resources
- AndroidManifest information
- Assets
- Configuration files
- Third-party SDKs
- Embedded certificates
- API endpoints
- Application strings
The purpose of reverse engineering is not necessarily to recover the original source code perfectly. Decompiled code can differ significantly from the original source, particularly when an application uses optimization or obfuscation.
The goal is to obtain enough information to understand how the application works.
Why Is Android Reverse Engineering Important?
Mobile applications frequently contain security-sensitive logic.
For example, an application might perform:
- Authentication checks
- License validation
- Root detection
- Certificate pinning
- Encryption
- API request signing
- Local authorization
- Feature restrictions
- Payment validation
A penetration tester needs to determine whether these controls are implemented securely and whether they can be manipulated.
Consider an application that checks whether a user is an administrator before displaying a sensitive feature.
If the application performs that check only on the client, reverse engineering may reveal the relevant logic. The tester can then determine whether the backend independently enforces the same authorization.
This distinction is critical.
A client-side control can improve user experience, but it should not be the ultimate authority for security-sensitive authorization.
How Android Applications Are Structured
Before reversing an application, it helps to understand the basic Android application architecture.
An application may contain several important components.
APK
The APK is the installable application package.
It may contain:
AndroidManifest.xml- DEX files
- Resources
- Assets
- Native libraries
- Compiled resources
- Application metadata
DEX Files
Android applications commonly contain Dalvik Executable (DEX) bytecode.
The DEX format represents compiled application code that Android’s runtime can execute.
Large applications may contain multiple DEX files, such as:
classes.dex
classes2.dex
classes3.dex
This is especially common in applications with many dependencies.
Smali
Smali is a human-readable representation of Android’s DEX bytecode.
When Java or Kotlin code is compiled, the resulting DEX instructions can be represented as Smali.
Smali is useful when a decompiler does not produce clean or complete high-level code.
OWASP documents Smali disassembly as one of the standard Android reverse-engineering techniques.
Native Libraries
Some applications contain native libraries such as:
lib/arm64-v8a/*.so
These libraries may contain C or C++ code compiled for ARM-based processors.
Native code requires a different analysis approach from Java or Kotlin code.
OWASP specifically identifies native-code disassembly as a separate Android reverse-engineering technique.
Android Reverse Engineering Methodology
A structured methodology produces better results than immediately opening an APK in a decompiler.
A practical workflow looks like this:
- Define scope and authorization
- Obtain the application
- Identify the application package
- Examine the APK structure
- Inspect the manifest
- Perform static analysis
- Decompile application code
- Analyze Smali where necessary
- Inspect native libraries
- Search for sensitive strings and secrets
- Analyze application security controls
- Perform dynamic analysis
- Inspect network behavior
- Test APIs and business logic
- Validate findings
- Document the results
OWASP’s Android methodology includes dedicated techniques for package exploration, static analysis, dynamic analysis, reverse engineering, Smali disassembly, Java decompilation, and native-code analysis.
Step 1: Define the Testing Scope
Only reverse engineer applications that you are authorized to assess.
For a professional penetration test, clarify:
- Application versions
- Test devices
- Test accounts
- Backend APIs
- Production or staging environments
- Allowed instrumentation techniques
- Whether application modification is permitted
- Whether third-party services are in scope
This prevents accidental testing outside the agreed engagement.
For personal learning, use applications specifically designed for security training or vulnerable test environments.
Step 2: Obtain and Identify the APK
Start by identifying the package and application version.
Useful information includes:
- Package name
- Version name
- Version code
- Target SDK
- Minimum SDK
- Signing information
- Supported architectures
- Number of DEX files
For applications distributed through Android App Bundles, you may encounter multiple APK splits rather than one universal APK. OWASP notes that XAPK files from third-party stores can also contain base APKs, split APKs, and additional data.
The exact package structure matters because analyzing only the base component may cause you to miss functionality contained in another split.
Step 3: Analyze AndroidManifest.xml
The Android manifest is one of the first files a security tester should examine.
It can reveal:
- Application components
- Permissions
- Exported activities
- Services
- Broadcast receivers
- Content providers
- Deep links
- Intent filters
- Debug configuration
- Network security configuration
- Minimum and target SDK information
Manifest analysis can reveal unexpected attack surfaces.
Example: Exported Activity
Suppose an application exposes an activity that handles sensitive account functionality.
If another application can invoke that activity without the intended authorization checks, the exposed component may create a security issue.
OWASP includes dedicated tests for exported and unprotected Android activities that expose sensitive functionality.
The important point is that an exported component is not automatically vulnerable. The tester needs to determine whether its exposure crosses a security boundary.
Step 4: Perform Static Analysis
Static analysis examines the application without relying primarily on runtime execution.
Look for:
- Hardcoded credentials
- API endpoints
- Authentication logic
- Authorization checks
- Encryption functions
- Certificate validation
- Debug functionality
- Root detection
- WebView configuration
- Insecure storage
- Logging
- Dangerous permissions
- Sensitive data processing
Static analysis can quickly reveal where important security decisions are implemented.
Searching for Sensitive Strings
Searching application resources and code for strings is a simple but useful technique.
Potential targets include:
passwordsecrettokenapi_keyauthorizationclient_secretdebugadmin- Internal domains
- Development endpoints
A string that looks sensitive is not automatically a vulnerability.
For example, a public API identifier may intentionally be embedded in a mobile application. The tester must determine whether the discovered value actually provides unauthorized privileges.
Step 5: Decompile Java and Kotlin Code
Tools such as JADX can produce a high-level representation of DEX bytecode.
The resulting code can make it easier to understand:
- Classes
- Methods
- Control flow
- API calls
- Application logic
- Security checks
- Third-party libraries
However, decompiled output should not be treated as the original source code.
Names may have been changed by obfuscation, compiler transformations may alter the structure, and some constructs may not decompile cleanly.
Use the decompiler as an analysis aid rather than assuming every line represents the original implementation exactly.
Step 6: Analyze Smali Code
When high-level decompilation is unclear, Smali can provide a more direct view of the application’s bytecode.
Smali can help answer questions such as:
- What method is actually called?
- Which branch executes?
- What value is returned?
- Which permission is checked?
- Which API endpoint is constructed?
- Which cryptographic method is invoked?
For example, suppose Java decompilation produces confusing control flow around an authentication check.
Examining the corresponding Smali instructions may make the comparison and branch logic much easier to understand.
OWASP specifically recommends using Smali when the bytecode-level representation is needed for analysis.
Step 7: Analyze Native Libraries
Some Android applications place important logic inside native .so libraries.
Reasons for doing this can include:
- Performance
- Existing C/C++ code
- Hardware integration
- Cross-platform components
- Legacy code
- Additional resistance to straightforward Java/Kotlin analysis
Native code can contain:
- Encryption routines
- Authentication logic
- Anti-tampering checks
- JNI interfaces
- Sensitive algorithms
- Application-specific functionality
OWASP notes that Android reverse engineering can require working with both Java bytecode and native code, particularly when applications move between the Java and native layers through JNI.
Common tools for native analysis include Ghidra, radare2, and similar disassemblers.
Understanding JNI During Reverse Engineering
The Java Native Interface allows Android applications to communicate between managed code and native libraries.
A typical flow might look like:
Kotlin/Java → JNI method → native library → result returned to application
This can complicate analysis.
A security-sensitive function may appear harmless in the Java code while the actual implementation exists inside a native library.
When you encounter a JNI method, identify:
- The Java/Kotlin declaration
- The native method name
- The corresponding native library
- The native implementation
- Data passed between both layers
This provides a much clearer picture of the application’s actual execution flow.
Step 8: Analyze Application Components
Android’s component model creates several areas worth examining.
Activities
Check for:
- Exported activities
- Sensitive screens
- Missing permissions
- Intent-based access
- Authentication bypass opportunities
Services
Review whether services expose sensitive functionality to other applications.
Broadcast Receivers
Look for receivers that process external broadcasts without adequate validation.
Content Providers
Content providers can expose structured data between applications.
A poorly protected provider may expose sensitive records or allow unauthorized modifications.
Intents
Intents can transfer information and trigger application components.
Review whether sensitive information is sent through implicit intents where another application could potentially intercept or access it.
OWASP’s Android testing catalog includes dedicated techniques for enumerating activities, services, broadcast receivers, content providers, and analyzing implicit communication.
Step 9: Inspect WebViews
WebViews deserve special attention because they bridge web content and native Android functionality.
Review:
- JavaScript configuration
- JavaScript interfaces
- URL handling
- Local file access
- Navigation controls
- External content
- SSL error handling
- Sensitive native methods exposed to web content
A dangerous JavaScript bridge can expose native functionality to untrusted content.
OWASP’s current Android testing material includes tests covering WebView behavior, native code exposure, local file access, URL loading, and Safe Browsing configuration.
Step 10: Look for Cryptographic Weaknesses
Reverse engineering is particularly useful for understanding how an application implements cryptography.
Look for:
- Hardcoded encryption keys
- Weak algorithms
- Insecure modes
- Poor random-number generation
- Hardcoded IVs
- Reused keys
- Weak hashing
- Custom cryptographic implementations
For example, an application may call a function named encryptData(), but that does not prove the implementation is secure.
The tester should inspect the algorithm, key generation, key storage, mode of operation, and lifecycle.
OWASP includes Android tests for hardcoded cryptographic keys, insecure random sources, weak algorithms, broken encryption modes, and insufficient key sizes.
Step 11: Search for Insecure Randomness
Random values are often used for:
- Tokens
- Nonces
- Session identifiers
- Cryptographic keys
- Password reset values
- PINs
Using predictable values for security-sensitive purposes can create serious vulnerabilities.
For example, generating a token based on the current time can make the value easier to predict.
OWASP specifically warns against using predictable sources such as timestamps for security-sensitive random values and recommends secure random-number generator APIs instead.
Step 12: Perform Dynamic Analysis
Static analysis tells you what the application contains.
Dynamic analysis tells you what the application actually does.
During runtime testing, observe:
- API requests
- Authentication flows
- Local storage
- Runtime values
- Function calls
- Error handling
- Security checks
- WebView behavior
- Application responses
Runtime reverse engineering can inspect application behavior directly in memory while the application is running. OWASP describes runtime reverse engineering as an on-the-fly approach that can help analyze application state and behavior.
Runtime Instrumentation
Tools such as Frida can be used in authorized environments to observe or instrument application behavior.
This can help answer questions such as:
- Which method handles authentication?
- What parameters reach a sensitive function?
- What value does a security check return?
- Which certificate validation method executes?
- Where is a decrypted value used?
The objective should be controlled security validation rather than indiscriminate modification.
Runtime analysis is particularly useful when static analysis alone cannot explain an application’s behavior.
Step 13: Analyze Network Traffic
Reverse engineering should be combined with network testing.
An application may contain API endpoints that are not obvious from normal usage.
Look for:
- Base URLs
- API paths
- Authentication headers
- Token formats
- Request parameters
- GraphQL endpoints
- WebSocket connections
- Certificate configuration
An intercepting proxy can help analyze application requests in an authorized test environment.
If certificate pinning prevents inspection, OWASP MASTG provides dedicated techniques for analyzing and testing certificate-pinning behavior.
The important security question is not simply whether pinning exists. The tester should understand whether the implementation actually provides the intended protection.
Step 14: Analyze Authentication and Authorization
Reverse engineering can reveal where authentication and authorization decisions occur.
Search for:
- Login methods
- Token validation
- Role checks
- Permission checks
- Session handling
- Account recovery
- Biometric checks
Then verify these controls dynamically.
For example, if the client contains:
if (user.isAdmin())
the tester should determine whether the server independently enforces administrative authorization.
If the backend trusts the client-provided role, the architecture may be vulnerable to privilege escalation.
Step 15: Investigate Hardcoded Secrets
Hardcoded secrets remain one of the most common reasons to reverse engineer mobile applications.
Search for:
- API keys
- Passwords
- Private tokens
- Cloud credentials
- Encryption keys
- Signing material
- Internal endpoints
But validate every suspected secret.
A public API key may have intentionally limited privileges.
A private cloud credential with administrative access is much more serious.
The impact depends on what the credential can actually access.
Common Vulnerabilities Found Through Android Reverse Engineering
Reverse engineering can help identify a wide range of security weaknesses.
Hardcoded Secrets
Credentials or sensitive keys embedded inside the application.
Insecure Cryptography
Weak algorithms, keys, modes, or random-number generation.
Client-Side Authorization
Security decisions made entirely inside the application.
Insecure Data Storage
Sensitive information written to files, databases, logs, or preferences without appropriate protection.
Exported Components
Sensitive application functionality exposed through Android components.
Insecure WebViews
Unsafe JavaScript interfaces or untrusted content handling.
Insecure Network Configuration
Cleartext traffic, weak trust configuration, or incorrect certificate validation.
Debug Features
Development functionality accidentally included in production builds.
Weak Root Detection
Security-sensitive functionality depending entirely on easily bypassed client-side checks.
Vulnerable Third-Party Libraries
Outdated dependencies that introduce known weaknesses.
Android Reverse Engineering Tools
A professional toolkit may include several specialized tools.
JADX
Useful for viewing a high-level representation of DEX code.
Apktool
Useful for decoding APK resources and disassembling DEX code into Smali. OWASP documents Apktool as one approach for inspecting and working with Android packages.
Ghidra
Useful for analyzing native binaries and understanding compiled machine code.
Frida
Useful for runtime instrumentation and observing application behavior.
Objection
Useful for mobile runtime exploration and security testing workflows.
Android Studio
Useful for application inspection, debugging, development, and understanding Android application structures.
ADB
Android Debug Bridge provides command-line interaction with authorized Android devices and emulators.
Burp Suite
Useful for analyzing HTTP and HTTPS traffic during authorized mobile application assessments.
No individual tool replaces a methodology. The best results come from combining multiple tools with manual reasoning.
Static Analysis vs Dynamic Analysis
Both approaches have strengths and limitations.
| Area | Static Analysis | Dynamic Analysis |
|---|---|---|
| Source/code inspection | Excellent | Limited |
| Runtime behavior | Limited | Excellent |
| Hardcoded secrets | Excellent | Sometimes |
| API behavior | Limited | Excellent |
| Control-flow analysis | Excellent | Useful |
| Memory values | Limited | Excellent |
| Configuration review | Excellent | Useful |
| Business logic | Useful | Excellent |
A strong Android security assessment normally uses both.
Static analysis tells you where to investigate.
Dynamic analysis tells you whether the suspected weakness matters in practice.
Common Mistakes Beginners Make
Relying Completely on Decompiled Code
Decompilation is an approximation.
Always validate important conclusions against bytecode, runtime behavior, or both.
Treating Every Hardcoded String as a Vulnerability
Not every key or identifier is secret.
Determine its privilege and impact.
Ignoring Native Code
Important functionality may be implemented in .so libraries.
Testing Only the APK
Mobile applications are often clients for backend APIs.
A complete assessment should consider the server-side attack surface when it is in scope.
Assuming Obfuscation Means Security
Obfuscation makes analysis harder, but it does not replace authentication, authorization, encryption, or server-side security controls.
Ignoring Application Components
Activities, services, receivers, content providers, and intents can all create security boundaries that require testing.
Best Practices for Developers
Developers can make reverse engineering more difficult and reduce the impact of exposed client-side logic.
Recommended practices include:
- Never embed privileged secrets in the application
- Enforce authorization on backend services
- Use secure cryptographic APIs
- Protect sensitive local data
- Keep dependencies updated
- Minimize exported components
- Validate external intents
- Secure WebViews
- Avoid unnecessary logging
- Disable production debugging
- Use appropriate code obfuscation
- Implement application integrity controls where justified
- Monitor third-party dependencies
- Test release builds before deployment
Obfuscation should be treated as defense in depth rather than a replacement for fundamental security controls.
Using Reverse Engineering for Mobile Penetration Testing
Reverse engineering becomes especially powerful when integrated into a larger penetration-testing workflow.
A tester might begin with static analysis and discover an API endpoint.
The endpoint can then be tested through an intercepting proxy.
The tester may discover that a parameter controls a user’s account identifier.
That parameter can then be tested for authorization weaknesses.
The final finding might therefore involve several components:
Reverse engineering → API discovery → dynamic testing → authorization testing → vulnerability validation
This is much more valuable than simply reporting that an endpoint exists.
For security professionals developing these skills, “https://vuln.pentesthint.com/” hands-on labs can provide controlled environments for practicing mobile security concepts. Structured “https://academy.pentesthint.com/” cyber security training can also help build the underlying knowledge of application security, networking, and penetration testing.
Reverse Engineering and OWASP MASTG
The OWASP Mobile Application Security Testing Guide is one of the most useful references for mobile security professionals.
Its Android material includes dedicated techniques for:
- Reverse engineering
- Static analysis
- Dynamic analysis
- Smali disassembly
- Java decompilation
- Native-code disassembly
- String extraction
- Runtime analysis
- Debugging
- Application patching
OWASP currently maintains separate Android techniques and test cases within MASTG, making it possible to map practical testing activities to specific security requirements.
Using MASTG as a reference also helps testers avoid an overly tool-focused approach.
Instead of asking, “Which tool should I run?”, the better question is:
“Which security property am I trying to verify?”
The tool then becomes a means of answering that question.
Career Opportunities in Android Reverse Engineering
Android reverse engineering is useful for several cybersecurity career paths.
Relevant roles include:
- Mobile Penetration Tester
- Android Security Researcher
- Mobile Application Security Engineer
- Malware Analyst
- Reverse Engineer
- Application Security Engineer
- Vulnerability Researcher
- VAPT Consultant
- Product Security Engineer
- Security Researcher
A strong foundation in Java or Kotlin, Linux, Android internals, networking, cryptography, and basic C/C++ can make the learning process much easier.
For penetration testers, knowledge of web and API security is particularly valuable because many serious mobile vulnerabilities ultimately involve backend services.
Future of Android Reverse Engineering
Android applications continue to become more complex.
Modern applications may use:
- Kotlin
- Jetpack libraries
- Native C/C++
- Flutter
- React Native
- WebViews
- Multiple DEX files
- Dynamic code loading
- Cloud APIs
- Third-party SDKs
- Device integrity services
This means reverse engineering is becoming less about simply decompiling an APK and more about understanding an entire application ecosystem.
Native code, runtime behavior, third-party dependencies, cloud APIs, and application architecture increasingly need to be considered together.
OWASP’s MASTG continues to expand its Android techniques to cover modern application technologies and security testing scenarios.
Android Reverse Engineering Checklist
- Confirm written authorization and testing scope
- Identify application package and version
- Examine APK structure
- Review AndroidManifest.xml
- Check permissions
- Enumerate application components
- Identify exported activities and services
- Review broadcast receivers
- Review content providers
- Analyze DEX files
- Decompile Java/Kotlin code
- Inspect Smali where necessary
- Extract application strings
- Search for hardcoded secrets
- Identify API endpoints
- Inspect third-party SDKs
- Analyze native
.solibraries - Review cryptographic implementations
- Check random-number generation
- Analyze WebViews
- Review local storage
- Perform dynamic analysis
- Analyze network traffic
- Test authentication
- Test authorization
- Validate business logic
- Document evidence
- Map findings to appropriate security standards
Conclusion
Reverse engineering Android applications is an essential skill for modern mobile application security testing.
A good assessment goes beyond decompiling an APK. It involves understanding the application’s package structure, manifest, DEX bytecode, Smali instructions, Java or Kotlin logic, native libraries, application components, network communication, cryptography, local storage, and runtime behavior.
The most effective approach combines static analysis and dynamic analysis. Static analysis helps identify potentially dangerous implementation patterns, while runtime testing determines whether those patterns result in exploitable security weaknesses.
OWASP’s MASTG provides a strong technical foundation for this work, with dedicated Android techniques covering reverse engineering, static analysis, dynamic analysis, Smali, Java decompilation, native code, and runtime inspection.
For beginners, the best way to improve is to practice on intentionally vulnerable applications and gradually move from APK inspection to complete mobile penetration-testing workflows.
For professionals and organizations, combining reverse engineering with API testing, secure development, dependency management, and “https://pentesthint.com/” VAPT services provides a much stronger view of the real mobile attack surface.
FAQ
What is reverse engineering Android applications?
Reverse engineering Android applications is the process of analyzing compiled Android applications to understand their code, resources, configuration, components, and runtime behavior. Security professionals use it to identify vulnerabilities and validate security controls.
Is Android reverse engineering legal?
It depends on the application, jurisdiction, licensing terms, and purpose of the activity. Security testing should always be performed with appropriate authorization. For learning, use applications specifically designed for security research or intentionally vulnerable lab environments.
Which tools are used for Android reverse engineering?
Common tools include JADX, Apktool, Ghidra, Frida, Objection, Android Studio, ADB, and network-analysis tools such as Burp Suite. Different tools are useful for different stages of static and dynamic analysis.
What is Smali in Android reverse engineering?
Smali is a human-readable representation of Android DEX bytecode. It provides a lower-level view of application instructions and can be useful when high-level Java or Kotlin decompilation is incomplete or misleading.
Can Android applications be completely decompiled?
Not necessarily. Decompilers can reconstruct a useful representation of application logic, but the output may differ from the original source code. Obfuscation, optimization, compiler transformations, native code, and dynamically generated behavior can make complete recovery difficult.
Why is the AndroidManifest important during reverse engineering?
The manifest contains important application configuration, including permissions, components, intent filters, exported functionality, and other security-relevant settings. Reviewing it can reveal potential attack surfaces before deeper code analysis begins.
Can reverse engineering find API vulnerabilities?
Reverse engineering can reveal API endpoints, request structures, authentication mechanisms, and client-side assumptions. The actual API vulnerability must then be validated through authorized dynamic and server-side testing.
Is reverse engineering useful for Android penetration testing?
Yes. Reverse engineering can reveal hidden functionality, security checks, API endpoints, cryptographic implementations, hardcoded secrets, and application components that may not be visible through normal application use. It becomes especially effective when combined with dynamic analysis and API security testing.