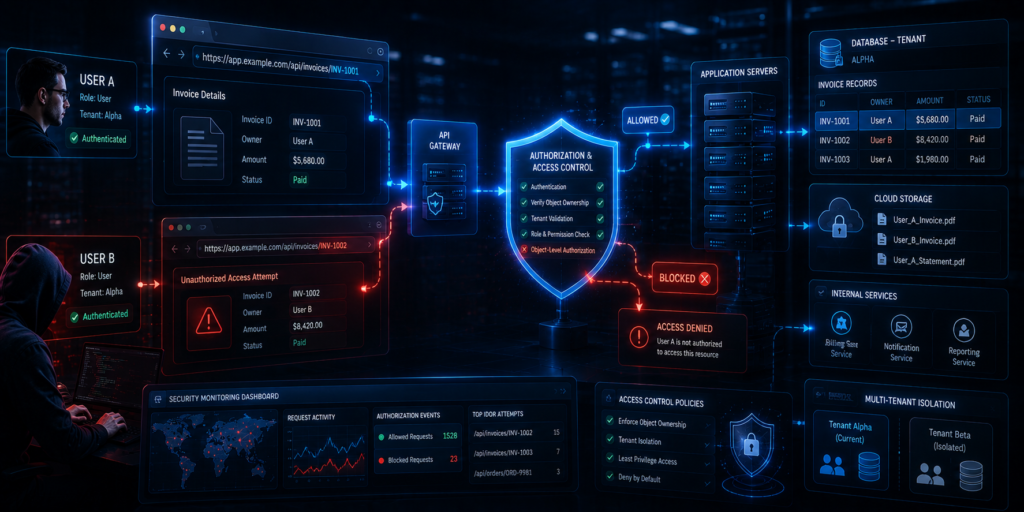
Security threats are becoming more sophisticated every year, yet many successful cyber attacks still rely on surprisingly simple weaknesses. One of the most common and dangerous issues is security misconfiguration.
Security misconfiguration occurs when systems, applications, cloud environments, databases, or network devices are deployed with insecure default settings or improper configurations. Attackers actively search for these weaknesses because they often provide an easy entry point into an organization’s infrastructure.
According to industry reports and security assessments, misconfigured systems remain one of the leading causes of data breaches worldwide. A single exposed cloud storage bucket, default administrator password, or improperly configured server can result in massive financial and reputational damage.
Understanding security misconfiguration is essential for developers, system administrators, penetration testers, and security professionals. Whether you are just beginning your cyber security journey or already working in the industry, learning how to identify and prevent configuration weaknesses is a critical skill.
What Is Security Misconfiguration?
Security misconfiguration refers to any incorrect, incomplete, or insecure configuration within software, hardware, cloud services, applications, operating systems, databases, or network devices.
The <a href=”https://owasp.org/”>OWASP</a> Top 10 consistently includes security misconfiguration because it remains one of the most frequently discovered vulnerabilities during security assessments.
Common examples include:
- Default usernames and passwords
- Unnecessary services running
- Open cloud storage buckets
- Exposed administrative interfaces
- Missing security headers
- Improper access permissions
- Verbose error messages
- Outdated software configurations
Unlike complex vulnerabilities, misconfigurations are often introduced accidentally during deployment or maintenance.
Why Security Misconfiguration Is a Serious Threat
Security misconfigurations create opportunities for attackers to gain unauthorized access without needing advanced exploitation techniques.
Easy Attack Surface
Attackers often begin reconnaissance by searching for:
- Open ports
- Default credentials
- Publicly accessible services
- Misconfigured cloud resources
These weaknesses can provide immediate access to critical systems.
Difficult to Detect
Many organizations focus heavily on vulnerability patching while overlooking configuration management.
A system may be fully patched but still remain vulnerable because of insecure settings.
High Impact
Misconfigured environments can expose:
- Customer records
- Financial data
- Intellectual property
- Authentication credentials
- Internal infrastructure information
In many cases, the resulting damage exceeds that caused by traditional software vulnerabilities.
Common Types of Security Misconfigurations
Default Credentials
Manufacturers often ship devices and applications with default usernames and passwords.
Examples include:
- admin/admin
- root/root
- administrator/password
If these credentials remain unchanged, attackers can easily gain access.
Unnecessary Services Enabled
Many operating systems and applications install services that may never be used.
Examples include:
- FTP services
- Telnet servers
- Legacy protocols
- Debugging interfaces
Every unnecessary service increases the attack surface.
Improper File Permissions
Incorrect permissions can allow unauthorized users to:
- Read sensitive files
- Modify application settings
- Execute malicious code
This issue is particularly common in Linux and cloud environments.
Exposed Cloud Resources
Cloud storage services frequently become public due to configuration mistakes.
Examples include:
- Public AWS S3 buckets
- Open Azure Blob Storage
- Misconfigured Google Cloud Storage
These exposures have resulted in numerous large-scale data breaches.
Missing Security Headers
Web applications often fail to implement security headers such as:
- Content Security Policy (CSP)
- X-Frame-Options
- X-Content-Type-Options
- Strict-Transport-Security (HSTS)
Missing headers increase susceptibility to various attacks.
Detailed Error Messages
Verbose application errors may reveal:
- Database structures
- Server versions
- Application frameworks
- Internal paths
Attackers can use this information during exploitation attempts.
How Security Misconfiguration Happens
Poor Deployment Processes
Organizations frequently prioritize functionality over security during deployment.
As a result:
- Default settings remain unchanged
- Security reviews are skipped
- Hardening procedures are ignored
Lack of Security Awareness
Developers and administrators may not fully understand secure configuration practices.
Organizations can address this through proper <a href=”https://academy.pentesthint.com/”>cyber security training</a> and continuous education.
Configuration Drift
Over time, systems change through updates, troubleshooting, and operational adjustments.
These modifications can gradually introduce insecure settings.
Inconsistent Environments
Development, testing, and production environments often differ significantly.
Security settings present in one environment may be missing in another.
Real-World Security Misconfiguration Breaches
Capital One Cloud Misconfiguration
One of the most well-known examples involved a cloud configuration issue that exposed sensitive customer information.
The breach affected over 100 million individuals and demonstrated how cloud security misconfigurations can have enormous consequences.
MongoDB Exposure Incidents
Thousands of internet-facing MongoDB databases have been discovered without authentication enabled.
Attackers have:
- Stolen data
- Deleted databases
- Demanded ransom payments
Many incidents occurred simply because default configurations were left unchanged.
Kubernetes Dashboard Exposures
Organizations deploying containerized environments have accidentally exposed Kubernetes dashboards to the internet.
Attackers gaining access can potentially:
- Deploy malicious containers
- Access secrets
- Compromise entire clusters
Common Attacks Resulting from Security Misconfiguration
Unauthorized Administrative Access
Exposed admin portals often become immediate attack targets.
Examples include:
- Database management panels
- Content management systems
- Cloud dashboards
Privilege Escalation
Misconfigured permissions can allow attackers to gain elevated privileges.
This often leads to full system compromise.
Data Exposure
Poor access controls frequently expose:
- Customer databases
- Internal documents
- Source code repositories
Remote Code Execution
Misconfigured application servers may permit attackers to execute arbitrary code.
This represents one of the most severe outcomes of security misconfiguration.
Information Disclosure
Configuration errors often reveal valuable intelligence that helps attackers identify additional weaknesses.
Detecting Security Misconfigurations
Automated Security Scanning
Organizations should regularly perform:
- Vulnerability assessments
- Configuration audits
- Compliance scans
Security professionals often use <a href=”https://vuln.pentesthint.com/”>hands-on labs</a> to learn how configuration weaknesses are identified in real-world environments.
Penetration Testing
Penetration testing helps uncover security gaps that automated scanners may miss.
Professional <a href=”https://pentesthint.com/”>VAPT services</a> can identify misconfigurations before attackers discover them.
Security Baseline Reviews
Comparing systems against established security baselines helps identify deviations from secure configurations.
Examples include:
- CIS Benchmarks
- NIST guidelines
- Vendor hardening recommendations
Log Analysis
Security logs often reveal:
- Unauthorized access attempts
- Suspicious configuration changes
- Administrative activity
Continuous monitoring improves detection capabilities.
Best Practices to Prevent Security Misconfiguration
Security Misconfiguration Prevention Strategies
Implement Secure Configuration Standards
Every system should follow documented hardening guidelines.
Examples include:
- Operating system hardening
- Database hardening
- Network device hardening
- Cloud security baselines
Change Default Credentials Immediately
Default accounts should never remain active in production environments.
Use:
- Strong passwords
- Multi-factor authentication
- Privileged access controls
Remove Unnecessary Components
Disable:
- Unused services
- Sample applications
- Test accounts
- Legacy protocols
Reducing the attack surface significantly improves security.
Automate Configuration Management
Infrastructure-as-Code (IaC) solutions help maintain consistent configurations.
Popular tools include:
- Ansible
- Terraform
- Puppet
- Chef
Automation reduces human error.
Apply Least Privilege Principles
Users and services should receive only the permissions necessary to perform their tasks.
This limits the impact of compromise.
Conduct Regular Security Reviews
Security assessments should be performed after:
- System deployments
- Major updates
- Infrastructure changes
Regular reviews help identify new risks early.
Tools Used to Identify Security Misconfigurations
Nmap
Used for:
- Port scanning
- Service detection
- Network reconnaissance
Nessus
Widely used for vulnerability and configuration assessments.
OpenVAS
An open-source vulnerability scanner capable of identifying numerous configuration weaknesses.
Lynis
A security auditing tool designed for Linux systems.
Scout Suite
A cloud security auditing tool that evaluates AWS, Azure, and Google Cloud environments.
Burp Suite
Useful for identifying web application configuration issues during security testing.
Professionals can practice with these tools using <a href=”https://vuln.pentesthint.com/”>cyber security labs</a> designed to simulate realistic environments.
Security Misconfiguration in Cloud Environments
Cloud adoption has increased the importance of configuration security.
Common cloud misconfigurations include:
- Public storage buckets
- Overly permissive IAM policies
- Exposed APIs
- Disabled logging
- Unencrypted storage
Organizations should continuously monitor cloud assets and enforce security baselines.
The <a href=”https://www.cisa.gov/”>CISA</a> and <a href=”https://www.nist.gov/”>NIST</a> provide valuable guidance for cloud security best practices.
Career Opportunities Related to Configuration Security
Security misconfiguration prevention is a critical responsibility across many cyber security roles.
Popular career paths include:
- Security Analyst
- Penetration Tester
- Security Engineer
- Cloud Security Engineer
- DevSecOps Engineer
- SOC Analyst
- Security Consultant
Individuals interested in building these skills can explore <a href=”https://academy.pentesthint.com/”>online cyber security courses</a> and practical training programs.
Future of Security Configuration Management
Modern environments are becoming increasingly complex.
Organizations now manage:
- Hybrid infrastructure
- Multi-cloud environments
- Containers
- Serverless applications
- Microservices
As complexity increases, automated configuration management and continuous compliance monitoring will become even more important.
Artificial intelligence, Infrastructure-as-Code, and policy-as-code technologies are helping organizations reduce configuration errors while improving security posture.
FAQ Section
What is security misconfiguration?
Security misconfiguration occurs when systems, applications, cloud services, or devices are deployed with insecure settings that expose them to cyber threats.
Why is security misconfiguration dangerous?
It creates vulnerabilities that attackers can exploit to gain unauthorized access, steal data, or compromise systems.
Is security misconfiguration part of the OWASP Top 10?
Yes. Security misconfiguration is consistently listed in the OWASP Top 10 because it remains one of the most common web application security risks.
What are examples of security misconfiguration?
Examples include default passwords, open cloud storage buckets, exposed admin panels, unnecessary services, and incorrect access permissions.
How can organizations prevent security misconfiguration?
Organizations should implement secure baselines, perform regular audits, remove unnecessary services, automate configuration management, and conduct penetration testing.
What tools help detect security misconfiguration?
Popular tools include Nmap, Nessus, OpenVAS, Lynis, Scout Suite, and Burp Suite.
Are cloud environments vulnerable to security misconfiguration?
Yes. Cloud environments are particularly vulnerable due to complex permission models and storage configurations.
How do penetration testers identify security misconfigurations?
Penetration testers use reconnaissance, vulnerability scanning, manual testing, configuration reviews, and exploitation techniques to identify weaknesses.
Conclusion
Security misconfiguration remains one of the most overlooked yet dangerous cyber security risks. While organizations invest heavily in vulnerability management and advanced security technologies, simple configuration mistakes continue to cause major breaches.
From default passwords and exposed cloud storage to insecure permissions and unnecessary services, attackers actively search for these weaknesses because they are often easy to exploit.
The good news is that security misconfiguration is largely preventable. By implementing secure configuration baselines, conducting regular assessments, automating configuration management, and investing in continuous security education, organizations can significantly reduce their attack surface.
For professionals looking to strengthen their skills, learn cyber security through practical training and hands-on experience. Businesses seeking stronger protection can leverage the expertise and <a href=”https://pentesthint.com/”>security consulting</a> solutions offered by <a href=”https://pentesthint.com/”>PentestHint</a> to identify and eliminate security misconfigurations before attackers do.